Free Practice Questions for the Cisco CCST 100-160 Exam (2026 Updated)
At Marks4sure, we are dedicated to providing IT professionals with the most accurate and reliable preparation materials for the Cisco 100-160 exam. To support your certification journey, we have made a selection of our premium 2026 CCST practice questions and answers available completely free. You can take this practice test as many times as you need. Every question includes a detailed, expertly verified explanation to ensure you fully grasp the core security concepts before test day.
Employees in the accounting department of a company receive an email about the latest federal accounting regulations. The email contains a hyperlink to register for a webinar providing updates on financial transaction security. The webinar claims to be hosted by a government agency.
As a security officer, you notice that the hyperlink points to an unknown third party.
Which type of cybersecurity threat should you investigate?
You are going to perform a penetration test on a company LAN. As part of your preparation, you access the company’s websites, view webpage source code, and run internet searches to uncover domain information. You also use social media to gather details about the company and its employees.
Which type of reconnaissance activities are you performing?
A restaurant installs a second wireless router that only employees can use.
Which statement describes how to securely configure the new router?
A security assessment reveals that a system administrator accessed files outside normal working hours. The assessment identifies the commands executed and records how long the administrator was connected to the system.
Which AAA component does this represent?
Your home network seems to have slowed down considerably. You look at the home router GUI and notice that an unknown host is attached to the network.
What should you do to prevent this specific host from attaching to the network again?
Which wireless security protocol provides the strongest protection for a home or small business network?
A threat actor sets up a rogue access point (AP) at a local cafe. The rogue AP captures traffic and then forwards the traffic to the cafe AP.
Which type of attack does this scenario describe?
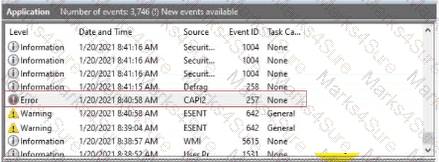
You are reviewing the Application log on a Windows computer. You see an event with an error-level message as shown.
What can you determine about the application that generated the event message?
A security assessment showed that a system administrator accessed files outside of normal working hours. The assessment listed the commands the administrator executed and indicated how long the administrator was connected to the system.
Which AAA component does this represent?
Your supervisor suspects that someone is attempting to gain access to a Windows computer by guessing user account IDs and passwords. The supervisor asks you to use the Windows Event Viewer security logs to verify the attempts.
Which two audit policy events provide information to determine whether someone is using invalid credentials to attempt to log in to the computer? (Choose 2.)
Note: You will receive partial credit for each correct selection.
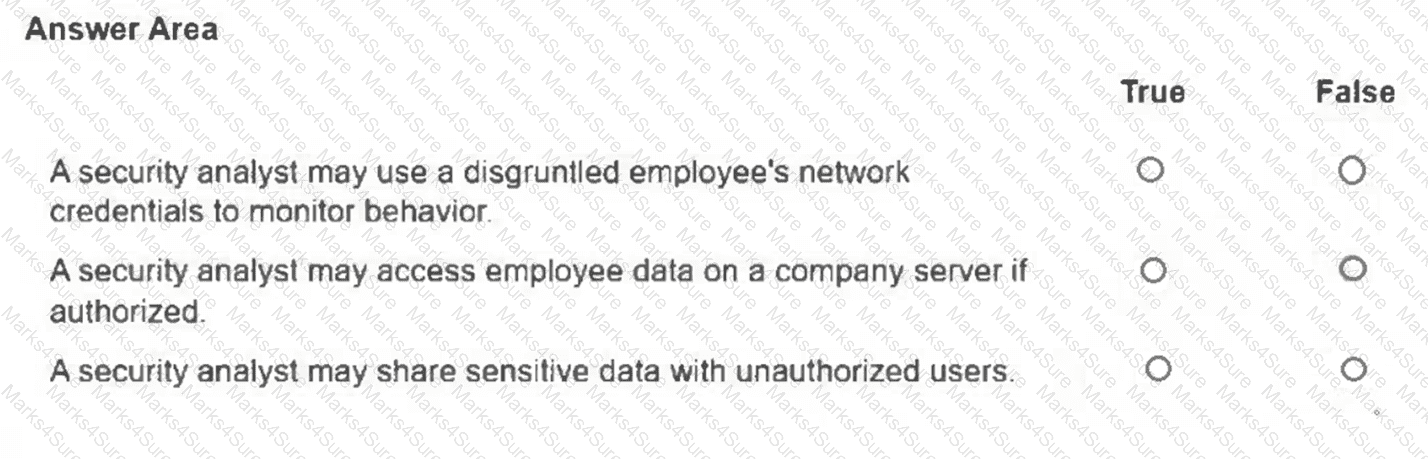
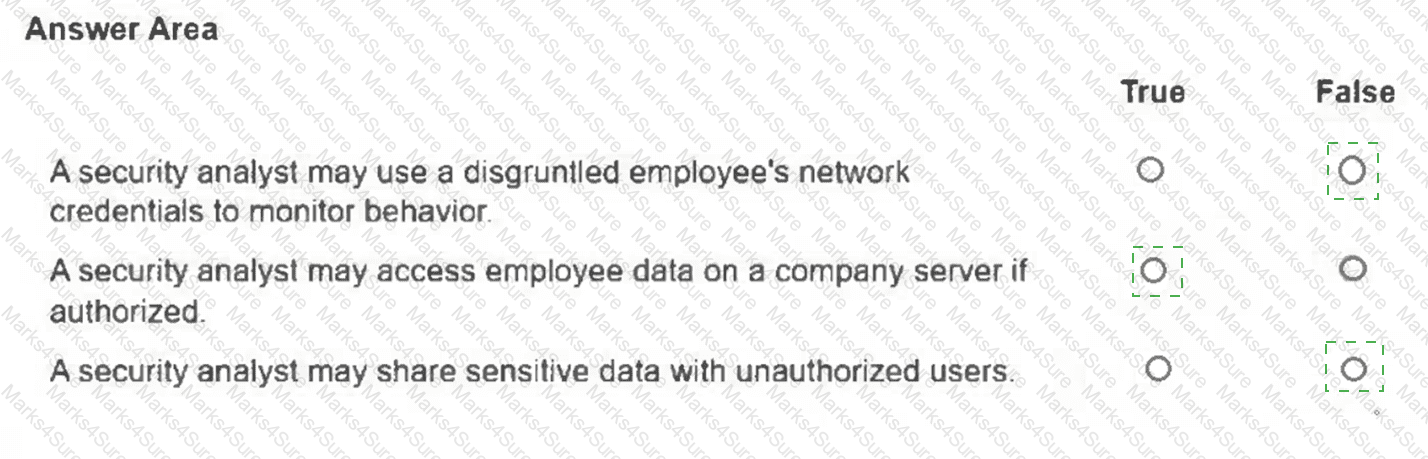
For each statement, select True if the statement adheres to the cybersecurity code of ethics, or False if it does not.
Note: You will receive partial credit for each correct selection.
A SOC analyst notices repeated failed login attempts from a foreign IP address followed by a successful login to a privileged account. What is the most appropriate next step?
Which Windows app is a command-line interface that includes a sophisticated scripting language used to automate Windows tasks?
Several employees complain that the company intranet site is no longer accepting their login information. You attempt to connect using the URL and notice some misspellings on the site. When you connect using the IP address, the site functions normally.
What should you do?
PDF + Testing Engine
Testing Engine
PDF (Q&A)