Free Practice Questions for the Cisco CyberOps Professional 300-215 Exam (2026 Updated)
At Marks4sure, we are dedicated to providing IT professionals with the most accurate and reliable preparation materials for the Cisco 300-215 exam. To support your certification journey, we have made a selection of our premium 2026 CyberOps Professional practice questions and answers available completely free. You can take this practice test as many times as you need. Every question includes a detailed, expertly verified explanation to ensure you fully grasp the core security concepts before test day.
Several previously unseen executable files are detected on an international bank’s transaction servers after an overnight batch-processing update. The executables make covert outbound connections to a server in a jurisdiction known for harboring threat actors. Their creation time also coincides with a network-intrusion attempt that the SOC initially classified as unsuccessful. The IT engineer has collected the observations and available data. Which set of actions should occur next?
An organization publishes a Microsoft Exchange Outlook Web App (OWA) server to provide access to enterprise email and deploys a web application firewall in front of it. Microsoft announces a newly discovered zero-day vulnerability that is being actively exploited. The vulnerability is triggered by a specially crafted request to an uncommonly used URL, and a patch is still being developed. Which action immediately protects the organization?
Which information is provided about the object file by the “-h” option in the objdump line command objdump –b oasys –m vax –h fu.o?
During a routine security audit, an organization ' s security team detects an unusual spike in network traffic originating from one of their internal servers. Upon further investigation, the team discovered that the server was communicating with an external IP address known for hosting malicious content. The security team suspects that the server may have been compromised. As the incident response process begins, which two actions should be taken during the initial assessment phase of this incident? (Choose two.)
A security team receives a SIEM notification that Cisco Secure Network Analytics detects abnormally high uploads from an internal workstation to external IP addresses over UDP port 53. Investigation confirms that the addresses are known malicious command-and-control servers. Which two actions effectively block these connections and prevent similar incidents? (Choose two.)
An incident response analyst is preparing to scan memory using a YARA rule. How is this task completed?
A company had a recent data leak incident. A security engineer investigating the incident discovered that a malicious link was accessed by multiple employees. Further investigation revealed targeted phishing attack attempts on macOS systems, which led to backdoor installations and data compromise. Which two security solutions should a security engineer recommend to mitigate similar attacks in the future? (Choose two.)
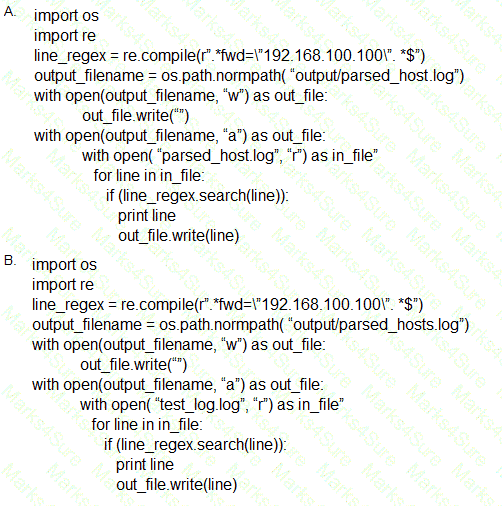
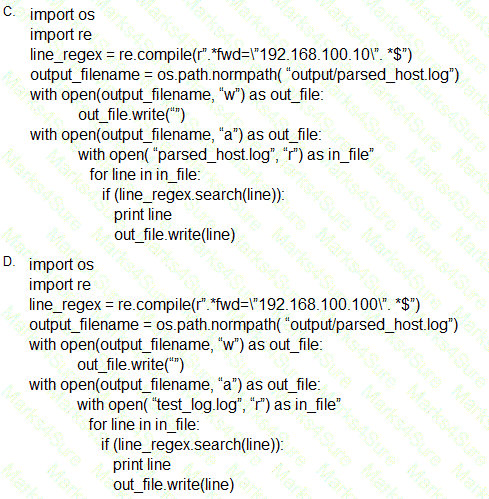
Which scripts will search a log file for the IP address of 192.168.100.100 and create an output file named parsed_host.log while printing results to the console?
Customers cannot access a company’s internal Apache web server. A security engineer investigates and determines that, several hours earlier, there were multiple failed SSH authentication attempts for the root account. After a successful login, the root user executed the sudo apt purge apache2 command. Which two Indicators of Attack can be determined from this information? (Choose two.)
What is the purpose of YARA rules in malware analysis and now do the rules atd in identifying, classifying, and documenting malware?
Refer to the exhibit.
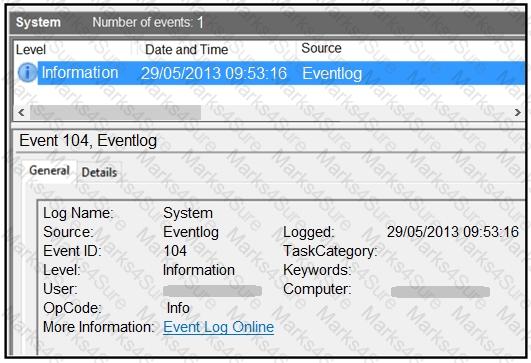
An employee notices unexpected changes and setting modifications on their workstation and creates an incident ticket. A support specialist checks processes and services but does not identify anything suspicious. The ticket was escalated to an analyst who reviewed this event log and also discovered that the workstation had multiple large data dumps on network shares. What should be determined from this information?
A data breach was recently experienced in which sensitive customer information was exfiltrated by an insider. After the incident was contained and affected customers were notified, a post-incident analysis was conducted to identify the root cause of the breach and develop recommendations to prevent similar incidents in the future. Which action should an engineer recommend?
Data has been exfiltrated and advertised for sale on the dark web. A web server shows:
Database unresponsiveness
PageFile.sys changes
Disk usage spikes with CPU spikes
High page faults
Which action should the IR team perform on the server?
A new zero-day vulnerability is discovered in the web application. Vulnerability does not require physical access and can be exploited remotely. Attackers are exploiting the new vulnerability by submitting a form with malicious content that grants them access to the server. After exploitation, attackers delete the log files to hide traces. Which two actions should the security engineer take next? (Choose two.)
A cybersecurity analyst detects fileless malware activity on secure endpoints. What should be done next?
Refer to the exhibit.
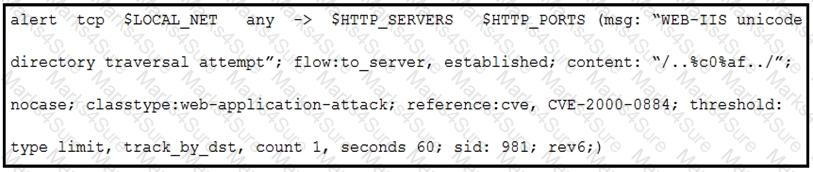
A company that uses only the Unix platform implemented an intrusion detection system. After the initial configuration, the number of alerts is overwhelming, and an engineer needs to analyze and classify the alerts. The highest number of alerts were generated from the signature shown in the exhibit. Which classification should the engineer assign to this event?
A cybersecurity analyst must identify an unknown service causing high CPU on a Windows server. What tool should be used?
Refer to the exhibit.
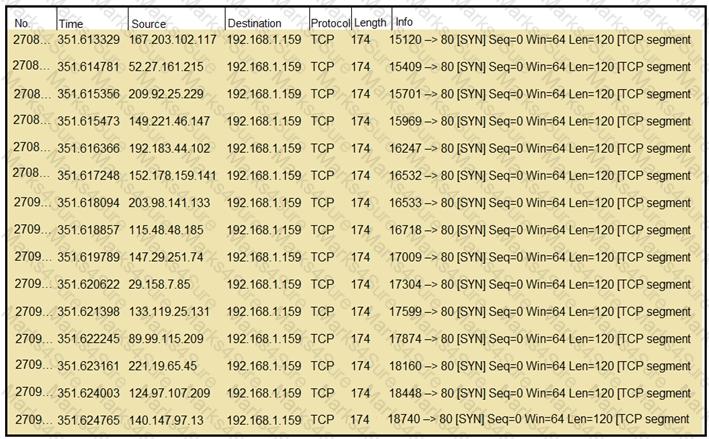
What should an engineer determine from this Wireshark capture of suspicious network traffic?
Which challenge is introduced by the dynamic nature of cloud environments during forensic analysis?
Which tool should an investigator use to extract information about running processes from RAM?
Refer to the exhibit.
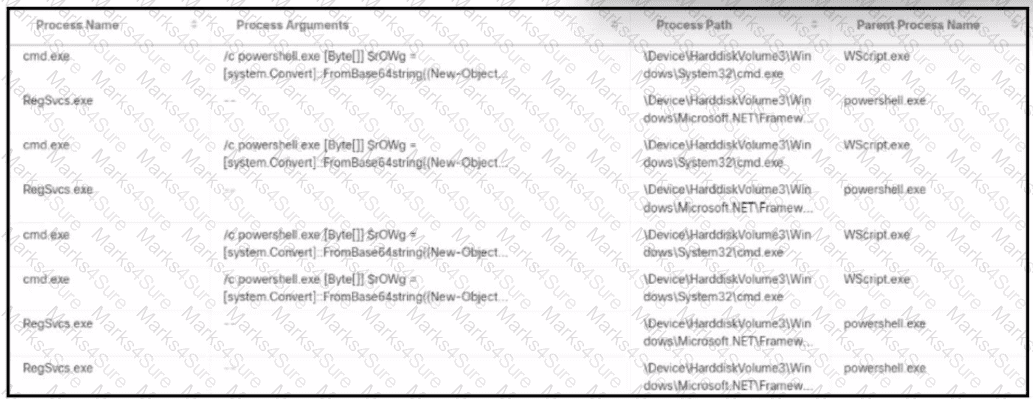
An alert came with a potentially suspicious activity from a machine in HR department. Which two IOCs should the security analyst flag? (Choose two.)
A company’s security engineer notices through the SIEM that an employee’s workstation sent several DNS requests involving the external IP address of the suspicious domain a4sn77d8z3dsci9416cov.com. After investigating multiple log sources, the security team determines that the employee downloaded an infected PDF file through a URL in an email. Which two elements must be included in the root cause analysis report? (Choose two.)
A security team received an alert of suspicious activity on a user’s Internet browser. The user’s anti-virus software indicated that the file attempted to create a fake recycle bin folder and connect to an external IP address. Which two actions should be taken by the security analyst with the executable file for further analysis? (Choose two.)
Which two tools conduct network traffic analysis in the absence of a graphical user interface? (Choose two.)
An investigator notices that GRE packets are going undetected over the public network. What is occurring?
An attacker embedded a macro within a word processing file opened by a user in an organization’s legal department. The attacker used this technique to gain access to confidential financial data. Which two recommendations should a security expert make to mitigate this type of attack? (Choose two.)
An investigator is analyzing an attack in which malicious files were loaded on the network and were undetected. Several of the images received during the attack include repetitive patterns. Which anti-forensic technique was used?
An attacker modifies a malicious file named TOPSECRET0523619132 by changing its file extension from a .png to a doc in an attempt to evade detection. Which technique is being used to disguise the file?
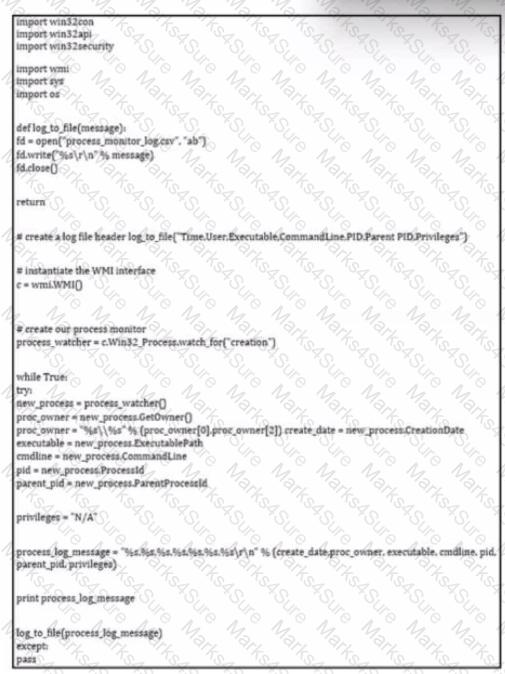
Refer to the exhibit.
import requests
def check_status(url):
response = requests.get(url)
return response.status_code
In which programming language is the code written, and what is it trying to accomplish?
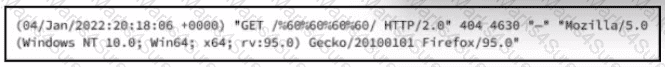
A security team needs to prevent a remote code execution vulnerability. The vulnerability can be exploited only by sending ' ${ string in the HTTP request. WAF rule is blocking ' ${ ' , but system engineers detect that attackers are executing commands on the host anyway. Which action should the security team recommend?
An EDR solution reports that a suspicious process dropped a malicious file on endpoint DE23X5940P. Sandbox analysis shows that the malware propagates through SMB and communicates through an encrypted command-and-control channel. A business-critical solution also depends on SMB. Which action should the security analyst take to respond to the incident and mitigate risk?
Refer to the exhibit.
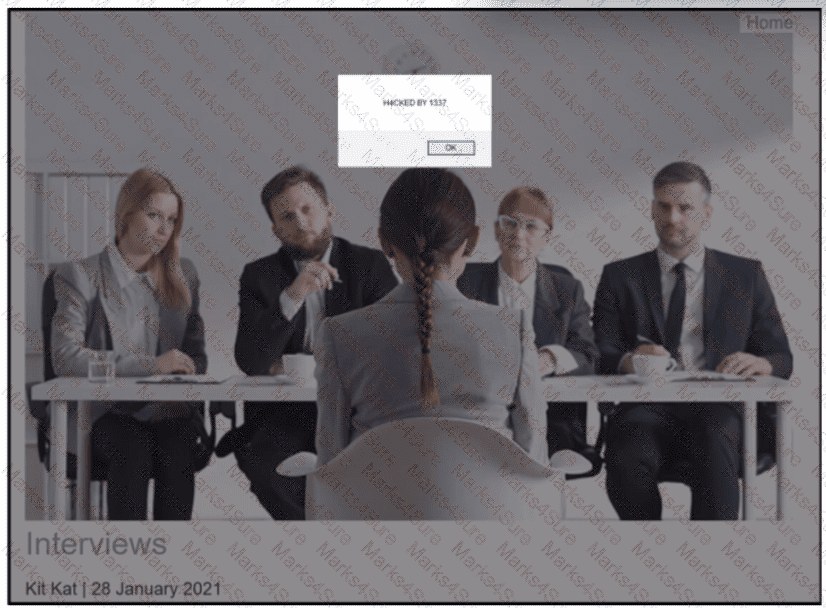
An engineer received a ticket to analyze a recent breach on a company blog. Every time users visit the blog, they are greeted with a message box. The blog allows users to register, log in, create, and provide comments on various topics. Due to the legacy build of the application, it stores user information in the outdated MySQL database. What is the recommended action that an engineer should take?
Drag and drop the steps from the left into the order to perform forensics analysis of infrastructure networks on the right.
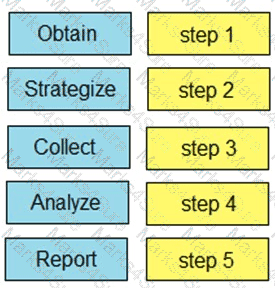
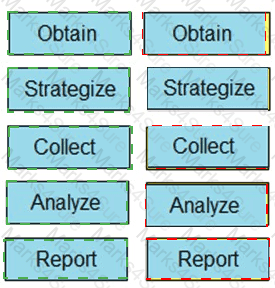
What describes the first step in performing a forensic analysis of infrastructure network devices?
A SOC team identifies the presence of APT29. The threat actor gained access to the environment through a phishing email sent to the communications manager one year earlier. APT29 is also known to exploit vulnerabilities remotely to gain access to victims’ systems. The SOC team takes the necessary actions and removes the backdoor. What is the next recommended step to protect the environment?
A security team received reports of users receiving emails linked to external or unknown URLs that are non-returnable and non-deliverable. The ISP also reported a 500% increase in the amount of ingress and egress email traffic received. After detecting the problem, the security team moves to the recovery phase in their incident response plan. Which two actions should be taken in the recovery phase of this incident? (Choose two.)
An enterprise security analyst is investigating a potential breach. Internal logs show repeated login failures from an internal IP address, followed by a successful login during the early morning when no staff should be active. External threat intelligence associates the IP range with a known malicious actor. Which action correctly interprets the threat-intelligence data and determines IOCs and IOAs?

A network host is infected with malware by an attacker who uses the host to make calls for files and shuttle traffic to bots. This attack went undetected and resulted in a significant loss. The organization wants to ensure this does not happen in the future and needs a security solution that will generate alerts when command and control communication from an infected device is detected. Which network security solution should be recommended?
What is the primary role of hex editors such as HxD in digital forensics and incident-response investigations?
Refer to the exhibit.
Registry Key Activity
MACHINE\SOFTWARE\MICROSOFT\WINDOWS\CURRENTVERSION\RUN modified (1)
MACHINE\SOFTWARE\MICROSOFT\WINDOWS\CURRENTVERSION\RUNONCE created (1), modified (2)
MACHINE\SOFTWARE\MICROSOFT\WINDOWS NT\CURRENTVERSION\WINLOGON modified (1)
MACHINE\SYSTEM\CURRENTCONTROLSET\CONTROL\SESSION MANAGER\ENVIRONMENT modified (1)
MACHINE\SOFTWARE\MICROSOFT\WINDOWS\CURRENTVERSION\POLICIES\EXPLORER modified (2)
MACHINE\SOFTWARE\MICROSOFT\COMMAND PROCESSOR modified (1)
For user S-5-21-0533532869, which registry key shows evidence of persistence through a newly created autorun entry?
Refer to the exhibit.
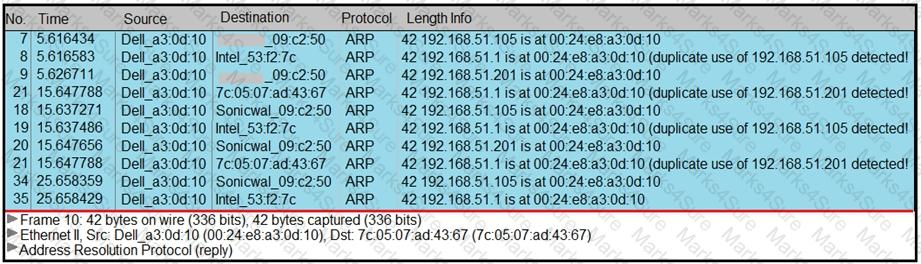
A security analyst notices unusual connections while monitoring traffic. What is the attack vector, and which action should be taken to prevent this type of event?
A cybersecurity analyst is investigating a high-priority incident involving a company executive’s workstation. The endpoint detection and response system flagged multiple file-modification events on the workstation. The files are normally read-only and contain sensitive financial data. The workstation’s antivirus software has not detected known malware or suspicious activity, and initial dynamic analysis of the files revealed no abnormal network behavior. Given this complex scenario, what is the recommended next step?
A company’s IIS web server is breached, and the attacker accesses a Microsoft Windows Server 2016 host by exploiting an SMB vulnerability on the same subnet. The intruder shuts down critical services on the Windows server. A security engineer must retrieve the IIS logs from the web server and service-related logs from the Windows server. Which two actions accomplish this task? (Choose two.)
PDF + Testing Engine
Testing Engine
PDF (Q&A)