Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: pass65

Free Practice Questions for the Cisco CCNP Security 300-715 Exam (2026 Updated)

At Marks4sure, we are dedicated to providing IT professionals with the most accurate and reliable preparation materials for the Cisco 300-715 exam. To support your certification journey, we have made a selection of our premium 2026 CCNP Security practice questions and answers available completely free. You can take this practice test as many times as you need. Every question includes a detailed, expertly verified explanation to ensure you fully grasp the core security concepts before test day.

Questions 4

A network administrator has just added a front desk receptionist account to the Cisco ISE Guest Service sponsor group. Using the Cisco ISE Guest Sponsor Portal, which guest services can the receptionist provide?

Options:

A.

Keep track of guest user activities

B.

Configure authorization settings for guest users

C.

Create and manage guest user accounts

D.

Authenticate guest users to Cisco ISE

Buy Now
Questions 5

A network engineer needs to deploy 802.1x using Cisco ISE in a wired network environment where thin clients download their system image upon bootup using PXE. For which mode must the switch ports be configured?
Options:

A.

closed

B.

restricted

C.

monitor

D.

low-impact

Buy Now
Questions 6

300-715 Question 6

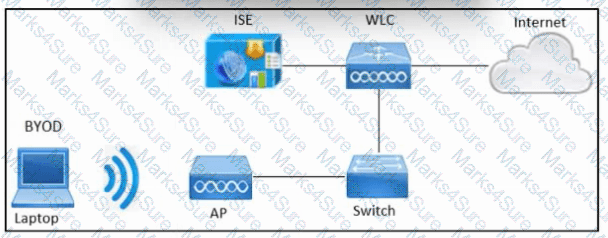
Refer to the exhibit. An engineer must configure BYOD in Cisco ISE. A single SSID must be used to allow BYOD devices to connect to the network. These configurations have been performed on Wireless LAN Controller already:

RADIUS server

BYOD-Dot1x SSID

Which two configurations must be done in Cisco ISE to meet the requirement? (Choose two.)

Options:

A.

FlexConnect ACL

B.

External identity source

C.

Authentication policy

D.

Redirect ACL

E.

Profiling policy

Buy Now
Questions 7

A network security administrator wants to integrate Cisco ISE with Active Directory. Which configuration action must the security administrator take to accomplish the task?

Options:

A.

Remove Cisco ISE user account from the domain.

B.

Remove the ISE machine account from the domain.

C.

Join Cisco ISE to the Active Directory domain.

D.

Search Active Directory to see if admin user account exists.

Buy Now
Questions 8

An administrator needs to connect ISE to Active Directory as an external authentication source and allow the proper ports through the firewall. Which two ports should be opened to accomplish this task? (Choose two)

Options:

A.

TELNET 23

B.

LDAP 389

C.

HTTP 80

D.

HTTPS 443

E.

MSRPC 445

Buy Now
Questions 9

Which statement about configuring certificates for BYOD is true?

Options:

A.

An Android endpoint uses EST, whereas other operating systems use SCEP for enrollment

B.

The SAN field is populated with the end user name.

C.

An endpoint certificate is mandatory for the Cisco ISE BYOD

D.

The CN field is populated with the endpoint host name

Buy Now
Questions 10

An engineer is configuring posture assessment for their network access control and needs to use an agent that supports using service conditions as conditions for the assessment. The agent should be run as a background process to avoid user interruption but when it is run. the user can see it. What is the problem?

Options:

A.

The engineer is using the " Anyconnect” posture agent but should be using the " Stealth Anyconnect posture agent

B.

The posture module was deployed using the headend instead of installing it with SCCM

C.

The user was in need of remediation so the agent appeared m the notifications

D.

The proper permissions were no! given to the temporal agent to conduct the assessment

Buy Now
Questions 11

When configuring an authorization policy, an administrator cannot see specific Active Directory groups present in their domain to be used as a policy condition. However, other groups that are in the same domain are seen What is causing this issue?

Options:

A.

Cisco ISE only sees the built-in groups, not user created ones

B.

The groups are present but need to be manually typed as conditions

C.

Cisco ISE ' s connection to the AD join point is failing

D.

The groups are not added to Cisco ISE under the AD join point

Buy Now
Questions 12

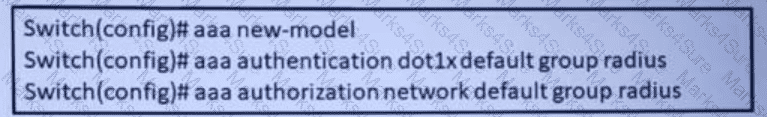
TION NO: 69

Refer to the exhibit.

300-715 Question 12

A network engineers configuring the switch to accept downloadable ACLs from a Cisco ISC server Which two commands should be run to complete the configuration? (Choose two)

Options:

A.

aaa authorization auth-proxy default group radius

B.

radius server vsa sand authentication

C.

radius-server attribute 8 include-in-access-req

D.

ip device tracking

E.

dot1x system-auth-control

Buy Now
Questions 13

Which are two characteristics of TACACS+? (Choose two)

Options:

A.

It uses TCP port 49.

B.

It combines authorization and authentication functions.

C.

It separates authorization and authentication functions.

D.

It encrypts the password only.

E.

It uses UDP port 49.

Buy Now
Questions 14

What are two differences between the RADIUS and TACACS+ protocols ' ? (Choose two.)

Options:

A.

RADIUS is a Cisco proprietary protocol, whereas TACACS+ is an open standard protocol

B.

TACACS+uses TCP port 49. whereas RADIUS uses UDP ports 1812 and 1813.

C.

RADIUS offers multiprotocol support, whereas TACACS+ does not

D.

RADIUS combines authentication and authorization, whereas TACACS+ does not

E.

RADIUS enables encryption of all the packets, whereas with TACACS+. only the password is encrypted.

Buy Now
Questions 15

A network engineer must configure a centralized Cisco ISE solution for wireless guest access with users in different time zones. The guest account activation time must be independent of the user’s time zone, and the guest account must be enabled automatically when the user self-registers on the guest portal. Which option in the time profile settings must be selected to meet the requirement?

Options:

A.

Set the Minimum Account Duration to 10 days.

B.

Set the Duration Hours to 24:00.

C.

Select From Creation Date from the Account Type drop-down list.

D.

Select From First Login from the Account Type drop-down list.

Buy Now
Questions 16

Which Cisco ISE deployment model is recommended for an enterprise that has over 50,000 concurrent active endpoints?

Options:

A.

large deployment with fully distributed nodes running all personas

B.

medium deployment with primary and secondary PAN/MnT/pxGrid nodes with shared PSNs

C.

medium deployment with primary and secondary PAN/MnT/pxGrid nodes with dedicated PSNs

D.

small deployment with one primary and one secondary node running all personas

Buy Now
Questions 17

A network engineer must create a new sponsored guest portal in Cisco ISE to provide secure wireless access for company guests. All required SSL certificates, external identity sources, and identity source sequences have already been configured. Drag and drop the remaining settings into the correct configuration sequence.

Options:

A.

Authorize the sponsored guest portal.

B.

Configure the Sponsor Change Password Settings option.

C.

Configure the Post-Login Banner Settings page.

D.

Create the sponsored guest portal.

Buy Now
Questions 18

What should be considered when configuring certificates for BYOD?

An endpoint certificate is mandatory for the Cisco ISE BYOD

Options:

A.

An Android endpoint uses EST whereas other operation systems use SCEP for enrollment

B.

The CN field is populated with the endpoint host name.

C.

The SAN field is populated with the end user name

Buy Now
Questions 19

A company manager is hosting a conference. Conference participants must connect to an open guest SSID and only use a preassigned code that they enter into the guest portal prior to gaining access to the network. How should the manager configure Cisco ISE to accomplish this goal?

Options:

A.

Create entries in the guest identity group for all participants.

B.

Create an access code to be entered in the AUP page.

C.

Create logins for each participant to give them sponsored access.

D.

Create a registration code to be entered on the portal splash page.

Buy Now
Questions 20

An engineer is configuring a guest password policy and needs to ensure that the password complexity requirements are set to mitigate brute force attacks. Which two requirement complete this policy? (Choose two)

Options:

A.

minimum password length

B.

active username limit

C.

access code control

D.

gpassword expiration period

E.

username expiration date

Buy Now
Questions 21

A network engineer must enable a profiling probe. The profiling must take details through the Active Directory. Where in the Cisco ISE interface would the engineer enable the probe?

Options:

A.

Policy > Policy Elements > Profiling

B.

Administration > Deployment > System > Profiling

C.

Policy > Deployment > System > Profiling

D.

Administration > System > Deployment > Profiling

Buy Now
Questions 22

Which media type must be used for zero-touch provisioning on a Cisco ISE hardware appliance?

Options:

A.

Network

B.

USB

C.

CD/DVD

D.

Virtual media

Buy Now
Questions 23

A user is attempting to register a BYOD device to the Cisco ISE deployment, but needs to use the onboarding policy to request a digital certificate and provision the endpoint. What must be configured to accomplish this task?

Options:

A.

A native supplicant provisioning policy to redirect them to the BYOD portal for onboarding

B.

The Cisco AnyConnect provisioning policy to provision the endpoint for onboarding

C.

The BYOD flow to ensure that the endpoint will be provisioned prior to registering

D.

The posture provisioning policy to give the endpoint all necessary components prior to registering

Buy Now
Questions 24

Which advanced option within a WLAN must be enabled to trigger Central Web Authentication for Wireless users on AireOS controller?

Options:

A.

DHCP server

B.

static IP tunneling

C.

override Interface ACL

D.

AAA override

Buy Now
Questions 25

A network engineer is in the predeployment discovery phase o! a Cisco ISE deployment and must discover the network. There is an existing network management system in the network. Which type of probe must be configured to gather the information?

Options:

A.

NetFlow

B.

RADIUS

C.

SNMP

D.

NMAP

Buy Now
Questions 26

What sends the redirect ACL that is configured in the authorization profile back to the Cisco WLC?

Options:

A.

Cisco-av-pair

B.

Class attribute

C.

Event

D.

State attribute

Buy Now
Questions 27

Which two fields are available when creating an endpoint on the context visibility page of Cisco IS? (Choose two)

Options:

A.

Policy Assignment

B.

Endpoint Family

C.

Identity Group Assignment

D.

Security Group Tag

E.

IP Address

Buy Now
Questions 28

An engineer must configure Cisco ISE to provide internet access for guests in which guests are required to enter a code to gain network access. Which action accomplishes the goal?

Options:

A.

Configure the hotspot portal for guest access and require an access code.

B.

Configure the sponsor portal with a single account and use the access code as the password.

C.

Configure the self-registered guest portal to allow guests to create a personal access code.

D.

Create a BYOD policy that bypasses the authentication of the user and authorizes access codes.

Buy Now
Questions 29

A network engineer is configuring Cisco TrustSec and needs to ensure that the Security Group Tag is being transmitted between two devices Where in the Layer 2 frame should this be verified?

Options:

A.

CMD filed

B.

802.1Q filed

C.

Payload

D.

802.1 AE header

Buy Now
Questions 30

A network administrator is configuring a new access switch to use with Cisco ISE for network access control. There is a need to use a centralized server for the reauthentication timers. What must be configured in order to accomplish this task?

Options:

A.

Configure Cisco ISE to replace the switch configuration with new timers.

B.

Configure Cisco ISE to block access after a certain period of time.

C.

Issue the authentication timer reauthenticate server command on the switch.

D.

Issue the authentication periodic command on the switch.

Buy Now
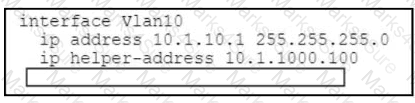
Questions 31

Refer to the exhibit.

300-715 Question 31

An engineer must configure a Cisco switch to send DHCP probes to a Cisco ISE Policy Service Node with IP address 10.1.100.6 on interface VLAN 10. Which code snippet completes the configuration?

Options:

A.

ip helper-address 10.1.100.6

B.

ip dhcp-address 10.1.100.6

C.

ip dhcp-relay 10.1.100.6

D.

ip helper-address 10.1.10.6

Buy Now
Questions 32

What are the minimum requirements for deploying the Automatic Failover feature on Administration nodes in a distributed Cisco ISE deployment?

Options:

A.

a primary and secondary PAN and a health check node for the Secondary PAN

B.

a primary and secondary PAN and no health check nodes

C.

a primary and secondary PAN and a pair of health check nodes

D.

a primary and secondary PAN and a health check node for the Primary PAN

Buy Now
Questions 33

Wireless network users authenticate to Cisco ISE using 802.1X through a Cisco Catalyst switch. An engineer must create an updated configuration to assign a security group tag to the user ' s traffic using inline tagging to prevent unauthenticated users from accessing a restricted server. The configurations were performed:

• configured Cisco ISE as a Cisco TrustSec AAA server

• configured the switch as a RADIUS device in Cisco ISE

• configured the wireless LAN controller as a TrustSec device in Cisco ISE

• created a security group tog for the wireless users

• created a certificate authentication profile

■ created an identity source sequence

• assigned an appropriate security group tag to the wireless users

• defined security group access control lists to specify an egress policy

• enforced the access control lists on the TrustSec policy matrix in Cisco ISE

• configured TrustSec on the switch

• configured TrustSec on the wireless LAN controller

Which two actions must be taken to complete the configuration? (Choose two.)

Options:

A.

Configure Security Group Tag Exchange Protocol on the wireless LAN controller.

B.

Configure Security Group Tag Exchange Protocol to distribute IP to security group tags on Cisco ISE.

C.

Configure inline tag propagation on the switch and wireless LAN controller.

D.

Create static IP-to-SGT mapping for the restricted web server.

E.

Configure Security Group Tag Exchange Protocol on the switch.

Buy Now
Questions 34

When planning for the deployment of Cisco ISE, an organization ' s security policy dictates that they must use network access authentication via RADIUS. It also states that the deployment provide an adequate amount of security and visibility for the hosts on the network. Why should the engineer configure MAB in this situation?

Options:

A.

The Cisco switches only support MAB.

B.

MAB provides the strongest form of authentication available.

C.

The devices in the network do not have a supplicant.

D.

MAB provides user authentication.

Buy Now
Questions 35

An engineer is implementing network access control using Cisco ISE and needs to separate the traffic based on the network device ID and use the IOS device sensor capability. Which probe must be used to accomplish this task?

Options:

A.

HTTP probe

B.

NetFlow probe

C.

network scan probe

D.

RADIUS probe

Buy Now
Questions 36

Which two external identity stores support EAP-TLS and PEAP-TLS? (Choose two.)

Options:

A.

Active Directory

B.

RADIUS Token

C.

Internal Database

D.

RSA SecurlD

E.

LDAP

Buy Now
Questions 37

An engineer is performing a bulk import of printer endpoints into a Cisco ISE local database by using LDAP. Which LDAP field must be configured to ensure that the devices are not profiled as Unknown?

Options:

A.

MAC Address Object Class

B.

MAC Address Profile Class

C.

Profile Attribute Name

D.

Device Profile Name

Buy Now
Questions 38

What must match between Cisco ISE and the network access device to successfully authenticate endpoints?

Options:

A.

SNMP version

B.

shared secret

C.

certificate

D.

profile

Buy Now
Questions 39

What are two differences of TACACS+ compared to RADIUS? (Choose two.)

Options:

A.

TACACS+ uses a connectionless transport protocol, whereas RADIUS uses a connection-oriented transport protocol.

B.

TACACS+ encrypts the full packet payload, whereas RADIUS only encrypts the password.

C.

TACACS+ only encrypts the password, whereas RADIUS encrypts the full packet payload.

D.

TACACS+ uses a connection-oriented transport protocol, whereas RADIUS uses a connectionless transport protocol.

E.

TACACS+ supports multiple sessions per user, whereas RADIUS supports one session per user.

Buy Now
Questions 40

An engineer is configuring TACACS+ within Cisco ISE for use with a non-Cisco network device. They need to send special attributes in the Access-Accept response to ensure that the users are given the appropriate access. What must be configured to accomplish this ' ?

Options:

A.

dACLs to enforce the various access policies for the users

B.

custom access conditions for defining the different roles

C.

shell profiles with custom attributes that define the various roles

D.

TACACS+ command sets to provide appropriate access

Buy Now
Questions 41

An administrator is adding network devices for a new medical building into Cisco ISE. These devices must be in a network device group that is identifying them as " Medical Switch " so that the policies can be made separately for the endpoints connecting through them. Which configuration item must be changed in the network device within Cisco ISE to accomplish this goal?

Options:

A.

Change the device type to Medical Switch.

B.

Change the device profile to Medical Switch.

C.

Change the model name to Medical Switch.

D.

Change the device location to Medical Switch.

Buy Now
Questions 42

Which personas can a Cisco ISE node assume ' ?

Options:

A.

policy service, gatekeeping, and monitoring

B.

administration, policy service, and monitoring

C.

administration, policy service, gatekeeping

D.

administration, monitoring, and gatekeeping

Buy Now
Questions 43

What is a difference between TACACS+ and RADIUS in regards to encryption?

Options:

A.

TACACS+ encrypts only the password, whereas RADIUS encrypts the username and password.

B.

TACACS+ encrypts the username and password, whereas RADIUS encrypts only the password.

C.

TACACS+ encrypts the password, whereas RADIUS sends the entire packet in clear text.

D.

TACACS+ encrypts the entire packet, whereas RADIUS encrypts only the password.

Buy Now
Questions 44

What is the Microsoft security policy recommendation (or fast user switching in Cisco ISE?

Options:

A.

Disable BYOD posture agent.

B.

Enable fast user switching.

C.

Disable fast user switching.

D.

Enable Cisco Secure Client posture agent.

Buy Now
Questions 45

An engineer is configuring ISE for network device administration and has devices that support both protocols. What are two benefits of choosing TACACS+ over RADUs for these devices? (Choose two.)

Options:

A.

TACACS+ is FIPS compliant while RADIUS is not

B.

TACACS+ is designed for network access control while RADIUS is designed for role-based access.

C.

TACACS+ uses secure EAP-TLS while RADIUS does not.

D.

TACACS+ provides the ability to authorize specific commands while RADIUS does not

E.

TACACS+ encrypts the entire payload being sent while RADIUS only encrypts the password.

Buy Now
Questions 46

An organization is hosting a conference and must make guest accounts for several of the speakers attending. The conference ended two days early but the guest accounts are still being used to access the network. What must be configured to correct this?

Options:

A.

Create an authorization rule denying sponsored guest access.

B.

Navigate to the Guest Portal and delete the guest accounts.

C.

Create an authorization rule denying guest access.

D.

Navigate to the Sponsor Portal and suspend the guest accounts.

Buy Now
Questions 47

Which nodes are supported in a distributed Cisco ISE deployment?

Options:

A.

Policy Service nodes tor automatic failover

B.

Administration nodes for session failover

C.

Monitoring nodes for PxGrid services

D.

Policy Service nodes for session failover

Buy Now
Questions 48

A user misplaces a personal phone and wants to blacklist the device from accessing the company network. The company uses Cisco ISE for corporate and BYOD device authentication. Which action must the user take in Cisco ISE?

Options:

A.

Sign in to the BYOD portal and mark the device as Lost.

B.

Sign in to the My Devices portal and mark the device as Lost.

C.

Sign in to the My Devices portal and mark the device as Irrecoverable.

D.

Sign in to the BYOD portal and mark the device as Irrecoverable.

Buy Now
Questions 49

An engineer is configuring a dedicated SSID for onboarding devices. Which SSID type accomplishes this configuration?
Options:

A.

dual

B.

hidden

C.

broadcast

D.

guest

Buy Now
Questions 50

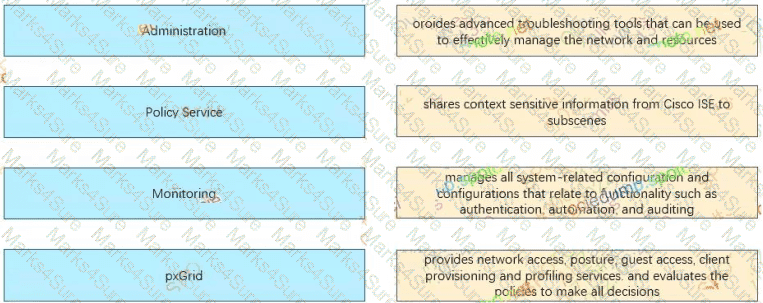
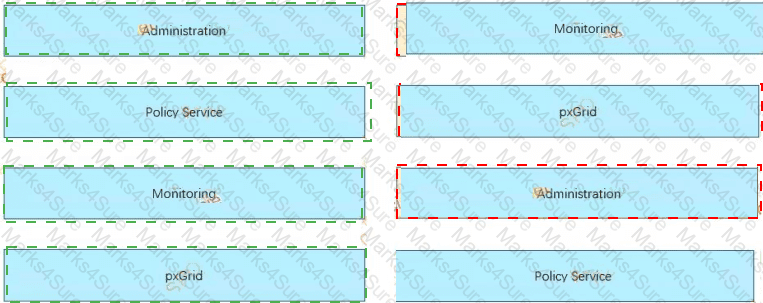
Select and Place

300-715 Question 50

Options:

Buy Now
Questions 51

What is the purpose of the ip http server command on a switch?

Options:

A.

It enables the https server for users for web authentication

B.

It enables MAB authentication on the switch

C.

It enables the switch to redirect users for web authentication.

D.

It enables dot1x authentication on the switch.

Buy Now
Questions 52

An engineer is configuring a virtual Cisco ISE deployment and needs each persona to be on a different node. Which persona should be configured with the largest amount of storage in this environment?

Options:

A.

policy Services

B.

Primary Administration

C.

Monitoring and Troubleshooting

D.

Platform Exchange Grid

Buy Now
Questions 53

An engineer must deploy a WLAN that supports identity networking. The Cisco Wireless LAN Controller must be configured to apply the VLAN tag for client traffic returned by the RADIUS server. Which configuration parameter on the Cisco Wireless LAN Controller must be enabled to meet the requirement?

Options:

A.

Change of Authorization

B.

CWA Redirect ACL

C.

Allow AAA Override

D.

FlexConnect

Buy Now
Questions 54

NO: 37

In which two ways can users and endpoints be classified for TrustSec?

(Choose Two.)

Options:

A.

VLAN

B.

SXP

C.

dynamic

D.

QoS

E.

SGACL

Buy Now
Questions 55

An engineer is migrating users from MAB to 802.1X on the network. This must be done during normal business hours with minimal impact to users. Which CoA method should be used?

Options:

A.

Port Bounce

B.

Port Shutdown

C.

Session Termination

D.

Session Reauthentication

Buy Now
Questions 56

An engineer must use Cisco ISE to provide network access to endpoints that cannot support 802.1X. The endpoint MAC addresses must be allowlisted by configuring an endpoint identity group. These configurations were performed:

• configured an identity group named allowlist

• configured the endpoints to use the MAC address of incompatible 802.1X devices

• added the endpoints to the allowlist identity group

• configured an authentication policy for MAB users

What must be configured?

Options:

A.

authorization profile that has the PermitAccess permission and matches the allowlist identity group

B.

logical profile that matches the allowlist identity group based on the configured policy

C.

authentication profile that has the PermitAccess permission and matches the allowlist identity group authorization policy that has the PermitAccess permission and matches the allowlist identity group

D.

authorization policy that has the PermitAccess permission and matches the allowtist identity group

Buy Now
Questions 57

In a standalone Cisco ISE deployment, which two personas are configured on a node? (Choose two )

Options:

A.

publisher

B.

administration

C.

primary

D.

policy service

E.

subscriber

Buy Now
Questions 58

An engineer is configuring Cisco ISE to reprofile endpoints based only on new requests of INIT-REBOOT and SELECTING message types. Which probe should be used to accomplish this task?
Options:

A.

MMAP

B.

DNS

C.

DHCP

D.

RADIUS

Buy Now
Questions 59

300-715 Question 59

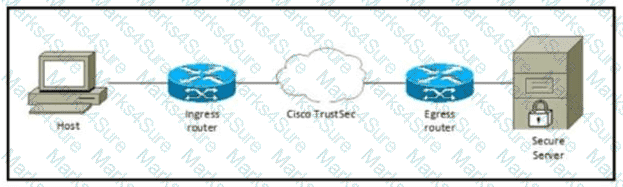
Refer to the exhibit Which component must be configured to apply the SGACL?

Options:

A.

egress router

B.

host

C.

secure server

D.

ingress router

Buy Now
Questions 60

An administrator is configuring posture with Cisco ISE and wants to check that specific services are present on the workstations that are attempting to access the network. What must be configured to accomplish this goal?

Options:

A.

Create a registry posture condition using a non-OPSWAT API version.

B.

Create an application posture condition using a OPSWAT API version.

C.

Create a compound posture condition using a OPSWAT API version.

D.

Create a service posture condition using a non-OPSWAT API version.

Buy Now
Questions 61

An engineer is deploying Cisco ISE in a network that contains existing security products from Cisco and other vendors. The customer requires support for Cisco TrustSec and the sharing of security group tags and policy objects between Cisco ISE and the other production security products. Which persona type must be enabled on one of the Cisco ISE nodes?

Options:

A.

SXP

B.

Policy Service

C.

pxGrid

D.

Identity Mapping

Buy Now
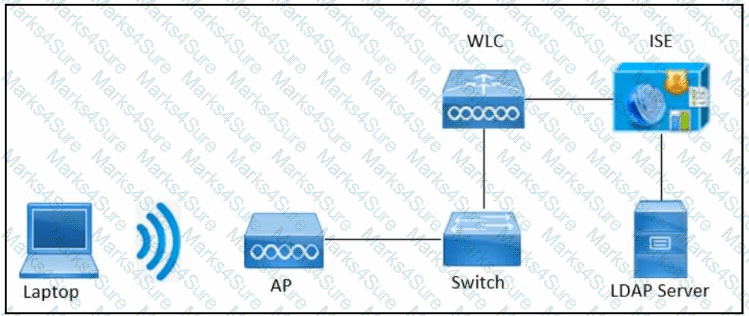
Questions 62

Refer to the exhibit.

300-715 Question 62

A laptop connects to the wireless network through the indicated access point. The Cisco Wireless LAN Controller must use Cisco ISE to authenticate users connected to the WLAN by using LDAP. What must be configured on Cisco ISE to authenticate the users?

Options:

A.

Federated server

B.

Single sign-on

C.

External identity source

D.

SAML identity provider

Buy Now
Questions 63

An engineer must use Cisco ISE profiler services to provide network access to Cisco IP phones that cannot support 802.1X. Cisco ISE is configured to use the access switch device sensor information — system-description and platform-type — to profile Cisco IP phones and allow access.

Which two protocols must be configured on the switch to complete the configuration? (Choose two.)

Options:

A.

LLDP

B.

CDP

C.

EAPOL

D.

SNMP

E.

STP

Buy Now
Questions 64

What is a valid guest portal type?

Options:

A.

Sponsored-Guest

B.

My Devices

C.

Sponsor

D.

Captive-Guest

Buy Now
Questions 65

Which two services must the administrator enable on the Cisco ISE deployment to ensure that the endpoint with MAC address 05:27:81:68:04:CA is authenticated, profiled, and added to the appropriate endpoint identity group? (Choose two.)

Options:

A.

RADIUS

B.

Posture

C.

TACACS+

D.

Profiling

E.

Session

Buy Now
Questions 66

Which permission is common to the Active Directory Join and Leave operations?

Options:

A.

Create a Cisco ISE machine account in the domain if the machine account does not already exist

B.

Remove the Cisco ISE machine account from the domain.

C.

Set attributes on the Cisco ISE machine account

D.

Search Active Directory to see if a Cisco ISE machine account already ex.sts.

Buy Now
Questions 67

When configuring Active Directory groups, what does the Cisco ISE use to resolve ambiguous group names?

Options:

A.

MIB

B.

TGT

C.

OMAB

D.

SID

Buy Now
Questions 68

What is a requirement for Feed Service to work?

Options:

A.

TCP port 3080 must be opened between Cisco ISE and the feed server

B.

Cisco ISE has a base license.

C.

Cisco ISE has access to an internal server to download feed update

D.

Cisco ISE has Internet access to download feed update

Buy Now
Questions 69

What is used by the Certificate Authority to issue a certificate to an endpoint?

Options:

A.

Certificate Provisioning Portal

B.

Device network address

C.

Certificate template

D.

Device unique identifier

Buy Now
Questions 70

A Cisco device has a port configured in multi-authentication mode and is accepting connections only from hosts assigned the SGT of SGT_0422048549 The VLAN trunk link supports a maximum of 8 VLANS What is the reason for these restrictions?

Options:

A.

The device is performing inline tagging without acting as a SXP speaker

B.

The device is performing mime tagging while acting as a SXP speaker

C.

The IP subnet addresses are dynamically mapped to an SGT.

D.

The IP subnet addresses are statically mapped to an SGT

Buy Now
Questions 71

An engineer is configuring web authentication using non-standard ports and needs the switch to redirect traffic to the correct port. Which command should be used to accomplish this task?

Options:

A.

permit tcp any any eq < port number >

B.

aaa group server radius proxy

C.

ip http port < port number >

D.

aaa group server radius

Buy Now
Questions 72

An administrator is configuring RADIUS on a Cisco switch with a key set to Cisc403012128 but is receiving the error “Authentication failed: 22040 Wrong password or invalid shared secret. “what must be done to address this issue?

Options:

A.

Add the network device as a NAD inside Cisco ISE using the existing key.

B.

Configure the key on the Cisco ISE instead of the Cisco switch.

C.

Use a key that is between eight and ten characters.

D.

Validate that the key is correct on both the Cisco switch as well as Cisco ISE.

Buy Now
Questions 73

A network administrator changed a Cisco ISE deployment from pilot to production and noticed that the JVM memory utilization increased significantly. The administrator suspects this is due to replication between the nodes What must be configured to minimize performance degradation?

Options:

A.

Review the profiling policies for any misconfiguration

B.

Enable the endpoint attribute filter

C.

Change the reauthenticate interval.

D.

Ensure that Cisco ISE is updated with the latest profiler feed update

Buy Now
Questions 74

Which use case validates a change of authorization?

Options:

A.

An authenticated, wired EAP-capable endpoint is discovered

B.

An endpoint profiling policy is changed for authorization policy.

C.

An endpoint that is disconnected from the network is discovered

D.

Endpoints are created through device registration for the guests

Buy Now
Questions 75

When creating a policy within Cisco ISE for network access control, the administrator wants to allow different access restrictions based upon the wireless SSID to which the device is connecting. Which policy condition must be used in order to accomplish this?

Options:

A.

Network Access NetworkDeviceName CONTAINS < SSID Name >

B.

DEVICE Device Type CONTAINS < SSID Name >

C.

Radius Called-Station-ID CONTAINS < SSID Name >

D.

Airespace Airespace-Wlan-ld CONTAINS < SSID Name >

Buy Now
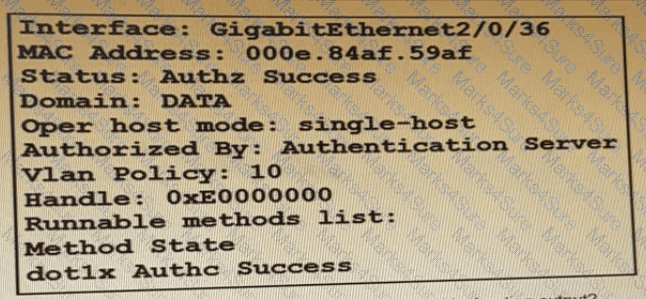
Questions 76

Refer to the exhibit:

300-715 Question 76

Which command is typed within the CU of a switch to view the troubleshooting output?

Options:

A.

show authentication sessions mac 000e.84af.59af details

B.

show authentication registrations

C.

show authentication interface gigabitethemet2/0/36

D.

show authentication sessions method

Buy Now
Questions 77

An engineer is testing Cisco ISE policies in a lab environment with no support for a deployment server. In order to push supplicant profiles to the workstations for testing, firewall ports will need to be opened. From which Cisco ISE persona should this traffic be originating?

Options:

A.

monitoring

B.

policy service

C.

administration

D.

authentication

Buy Now
Questions 78

An engineer is unable to use SSH to connect to a switch after adding the required CLI commands to the device to enable TACACS+. The device administration license has been added to Cisco ISE, and the required policies have been created. Which action is needed to enable access to the switch?

Options:

A.

The ip ssh source-interface command needs to be set on the switch

B.

802.1X authentication needs to be configured on the switch.

C.

The RSA keypair used for SSH must be regenerated after enabling TACACS+.

D.

The switch needs to be added as a network device in Cisco ISE and set to use TACACS+.

Buy Now
Questions 79

A user reports that the RADIUS accounting packets are not being seen on the Cisco ISE server.

Which command is the user missing in the switch’s configuration?

Options:

A.

radius-server vsa send accounting

B.

aaa accounting network default start-stop group radius

C.

aaa accounting resource default start-stop group radius

D.

aaa accounting exec default start-stop group radios

Buy Now
Questions 80

A Cisco ISE administrator needs to ensure that guest endpoint registrations are only valid for one day When testing the guest policy flow, the administrator sees that the Cisco ISE does not delete the endpoint in the Guest Endpoints identity store after one day and allows access to the guest network after that period. Which configuration is causing this problem?

Options:

A.

The Endpoint Purge Policy is set to 30 days for guest devices

B.

The RADIUS policy set for guest access is set to allow repeated authentication of the same device

C.

The length of access is set to 7 days in the Guest Portal Settings

D.

The Guest Account Purge Policy is set to 15 days

Buy Now
Questions 81

What service can be enabled on the Cisco ISE node to identity the types of devices connecting to a network?

Options:

A.

MAB

B.

profiling

C.

posture

D.

central web authentication

Buy Now
Questions 82

An organization is adding new profiling probes to the system to improve profiling on Oseo ISE The probes must support a common network management protocol to receive information about the endpoints and the ports to which they are connected What must be configured on the network device to accomplish this goal?

Options:

A.

ARP

B.

SNMP

C.

WCCP

D.

ICMP

Buy Now
Questions 83

Which two methods should a sponsor select to create bulk guest accounts from the sponsor portal? (Choose two )

Options:

A.

Random

B.

Monthly

C.

Daily

D.

Imported

E.

Known

Buy Now
Questions 84

Which port does Cisco ISE use for native supplicant provisioning of a Windows laptop?

Options:

A.

TCP 8909

B.

TCP 8905

C.

UDP 1812

D.

TCP 443

Buy Now
Questions 85

An engineer has been tasked with standing up a new guest portal for customers that are waiting in the lobby. There is a requirement to allow guests to use their social media logins to access the guest network to appeal to more customers What must be done to accomplish this task?

Options:

A.

Create a sponsor portal to allow guests to create accounts using their social media logins.

B.

Create a sponsored guest portal and enable social media in the external identity sources.

C.

Create a self-registered guest portal and enable the feature for social media logins

D.

Create a hotspot portal and enable social media login for network access

Buy Now
Questions 86

An engineer is assigned to enhance security across the campus network. The task is to enable MAB across all access switches in the network. Which command must be entered on the switch to enable MAB?

Options:

A.

Switch# authentication port-control auto

B.

Switch{conflg)# mab

C.

Switch{config-lf) # mab

D.

Switch(config)# authentication port-control auto

Buy Now
Questions 87

An engineer is configuring the remote access VPN to use Cisco ISE for AAA and needs to conduct posture checks on the connecting endpoints After the endpoint connects, it receives its initial authorization result and continues onto the compliance scan What must be done for this AAA configuration to allow compliant access to the network?

Options:

A.

Configure the posture authorization so it defaults to unknown status

B.

Fix the CoA port number

C.

Ensure that authorization only mode is not enabled

D.

Enable dynamic authorization within the AAA server group

Buy Now
Questions 88

An engineer is deploying a new Cisco ISE environment for a company. The company wants the deployment to use TACACS+. The engineer verifies that Cisco ISE has a Device Administration license. What must be configured to enable TACACS+ operations?

Options:

A.

Device Administration Work Center

B.

Device Admin service

C.

Device Administration Deployment settings

D.

Device Admin Policy Sets settings

Buy Now
Questions 89

An administrator plans to use Cisco ISE to deploy posture policies to assess Microsoft Windows endpoints that run Cisco Secure Client. The administrator wants to minimize the occurrence of messages related to unknown posture profiles if Cisco ISE fails to determine the posture of the endpoint. Secure Client is deployed to all the endpoints. and all the required Cisco ISE authentication, authorization, and posture policy configurations were performed. Which action must be taken next to complete the configuration?

Options:

A.

Install the latest version of the Secure Client client on the endpoints.

B.

Enable Cisco ISE posture on Secure Client configuration.

C.

Configure a native supplicant on the endpoints to support the posture policies.

D.

Install the compliance module on the endpoints.

Buy Now
Questions 90

An engineer is designing a new distributed deployment for Cisco ISE in the network and is considering failover options for the admin nodes. There is a need to ensure that an admin node is available for configuration of policies at all times. What is the requirement to enable this feature?

Options:

A.

one primary admin and one secondary admin node in the deployment

B.

one policy services node and one secondary admin node

C.

one policy services node and one monitoring and troubleshooting node

D.

one primary admin node and one monitoring and troubleshooting node

Buy Now
Questions 91

An administrator for a small network is configuring Cisco ISE to provide dynamic network access to users. Management needs Cisco ISE to not automatically trigger a CoA whenever a profile change is detected. Instead, the administrator needs to verify the new profile and manually trigger a CoA. What must be configuring in the profiler to accomplish this goal?

Options:

A.

Port Bounce

B.

No CoA

C.

Session Query

D.

Reauth

Buy Now
Questions 92

How is policy services node redundancy achieved in a deployment?

Options:

A.

by enabling VIP

B.

by utilizing RADIUS server list on the NAD

C.

by creating a node group

D.

by deploying both primary and secondary node

Buy Now
Questions 93

An engineer needs to configure Cisco ISE Profiling Services to authorize network access for IP speakers that require access to the intercom system. This traffic needs to be identified if the ToS bit is set to 5 and the destination IP address is the intercom system. What must be configured to accomplish this goal?

Options:

A.

NMAP

B.

NETFLOW

C.

pxGrid

D.

RADIUS

Buy Now
Questions 94

An engineer is configuring Central Web Authentication in Cisco ISE to provide guest access. When an authentication rule is configured in the Default Policy Set for the Wired_MAB or Wireless_MAB conditions, what must be selected for the " if user not found " setting?

Options:

A.

CONTINUE

B.

REJECT

C.

ACCEPT

D.

DROP

Buy Now
Questions 95

What is a difference between RADIUS and TACACS+?

Options:

A.

RADIUS uses connection-oriented transport, and TACACS+ uses best-effort delivery.

B.

RADIUS offers multiprotocol support, and TACACS+ supports only IP traffic.

C.

RADIUS combines authentication and authorization functions, and TACACS+ separates them.

D.

RADIUS supports command accounting, and TACACS+ does not.

Buy Now
Questions 96

What happens when an internal user is configured with an external identity store for authentication, but an engineer uses the Cisco ISE admin portal to select an internal identity store as the identity source?

Options:

A.

Authentication is redirected to the internal identity source.

B.

Authentication is redirected to the external identity source.

C.

Authentication is granted.

D.

Authentication fails.

Buy Now
Exam Code: 300-715
Exam Name: Implementing and Configuring Cisco Identity Services Engine (SISE)
Last Update: Sep 12, 2026
Questions: 322

PDF + Testing Engine

$64.99   $185.69

Testing Engine

$49.99   $142.83

PDF (Q&A)

$54.99   $157.11