Free Practice Questions for the Cisco CCNP Security 350-701 Exam (2026 Updated)
At Marks4sure, we are dedicated to providing IT professionals with the most accurate and reliable preparation materials for the Cisco 350-701 exam. To support your certification journey, we have made a selection of our premium 2026 CCNP Security practice questions and answers available completely free. You can take this practice test as many times as you need. Every question includes a detailed, expertly verified explanation to ensure you fully grasp the core security concepts before test day.
An engineer has enabled LDAP accept queries on a listener. Malicious actors must be prevented from quickly
identifying all valid recipients. What must be done on the Cisco ESA to accomplish this goal?
350-701 Report Card
A web hosting company must upgrade its older, unsupported on-premises servers. The company wants a cloud solution in which the cloud provider is responsible for:
Server patching
Application maintenance
Data center security
Disaster recovery
Which type of cloud meets the requirements?
An organization is trying to improve their Defense in Depth by blocking malicious destinations prior to a
connection being established. The solution must be able to block certain applications from being used within the network. Which product should be used to accomplish this goal?
In which two ways does a system administrator send web traffic transparently to the Web Security Appliance?
(Choose two)
A security engineer must configure a Splunk Universal Forwarder to send network traffic logs from Cisco Catalyst switches to a Splunk indexer cluster. Strict compliance requirements require all network traffic logs to be ingested into Splunk as an audit trail. The environment includes thousands of forwarders, and the data must be distributed across all indexers. Which two configuration actions must be performed? (Choose two.)
Refer to the exhibit. When creating an access rule for URL filtering, a network engineer adds certain categories and individual URLs to block. What is the result of the configuration?
What are two Detection and Analytics Engines of Cognitive Threat Analytics? (Choose two)
Which solution detects threats across a private network, public clouds, and encrypted traffic?
A security engineer must create a policy based on the reputation verdict of a file from a Cisco Secure Email Gateway. The file with an undetermined verdict must be dropped. Which action must the security engineer take to meet the requirement?
Which two methods must be used to add switches into the fabric so that administrators can control how switches are added into DCNM for private cloud management? (Choose two.)
How does Cisco Workload Optimization portion of the network do EPP solutions solely performance issues?
Which type of protection encrypts RSA keys when they are exported and imported?
What is the recommendation in a zero-trust model before granting access to corporate applications and
resources?
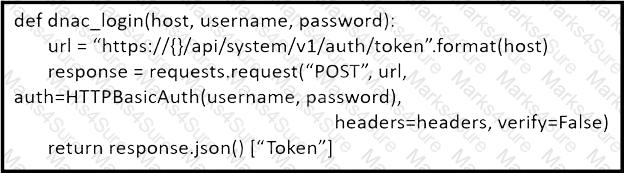
Refer to the exhibit.
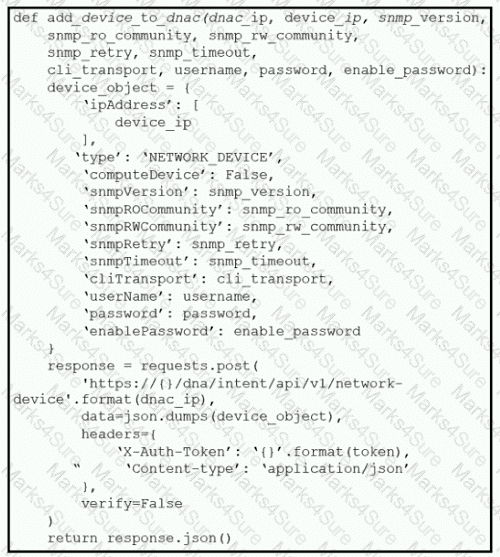
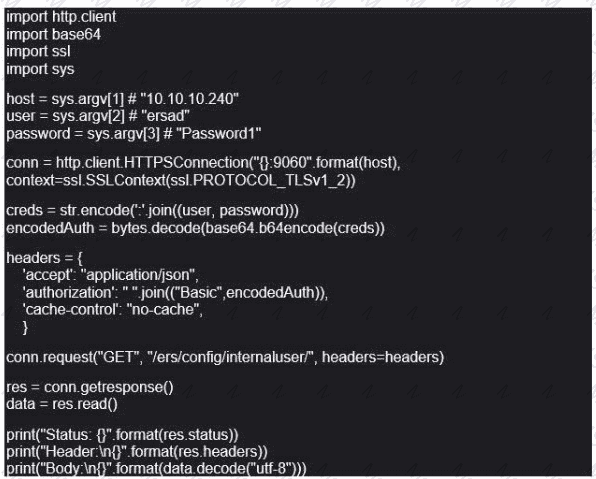
What is the result of this Python script of the Cisco DNA Center API?
Which license is required for Cisco Security Intelligence to work on the Cisco Next Generation Intrusion
Prevention System?
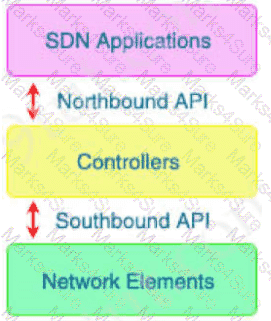
The main function of northbound APIs in the SDN architecture is to enable communication between which two areas of a network?
Which service allows a user to export application usage and performance statistics with Cisco Application Visibility and Control?
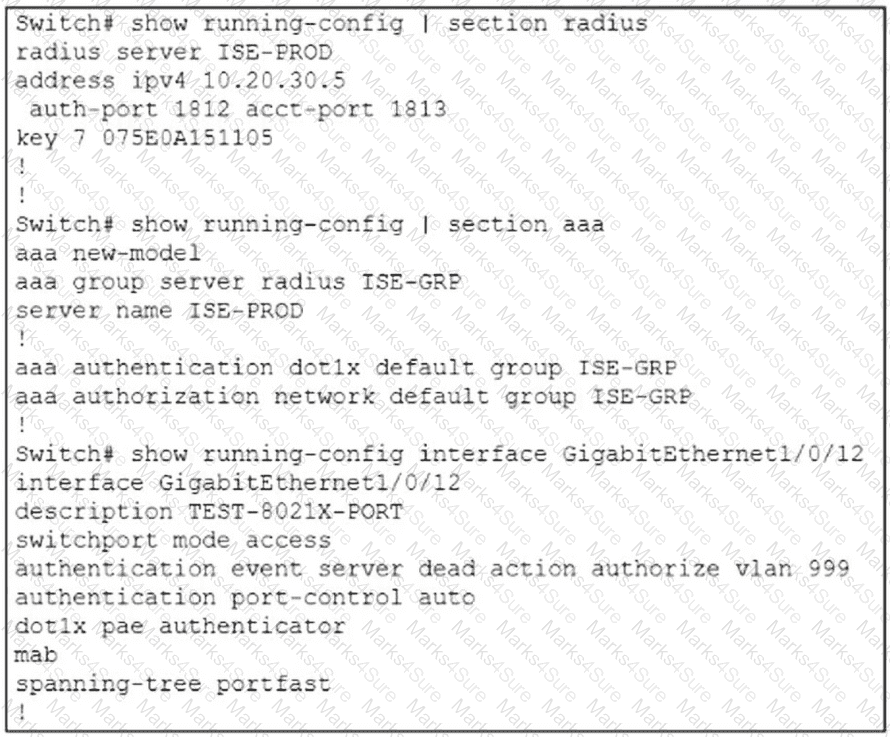
Refer to the exhibit.
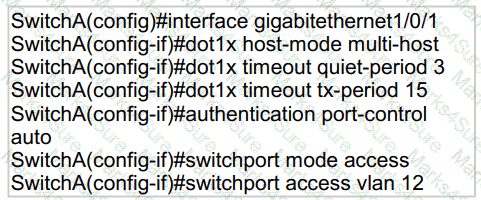
An engineer configured wired 802.1x on the network and is unable to get a laptop to authenticate. Which port configuration is missing?
An organization wants to implement a cloud-delivered and SaaS-based solution to provide visibility and threat detection across the AWS network. The solution must be deployed without software agents and rely on AWS VPC flow logs instead. Which solution meets these requirements?
How many interfaces per bridge group does an ASA bridge group deployment support?
Which open standard creates a framework for sharing threat intelligence in a machine-digestible format?
When a Cisco Secure Web Appliance checks a web request, what occurs if it is unable to match a user-defined policy?
A network engineer has entered the snmp-server user andy myv3 auth sha cisco priv aes 256
cisc0380739941 command and needs to send SNMP information to a host at 10.255.254.1. Which command achieves this goal?
Which solution for remote workers enables protection, detection, and response on the endpoint against known and unknown threats?
A Cisco FTD engineer is creating a new IKEv2 policy called s2s00123456789 for their organization to allow for additional protocols to terminate network devices with. They currently only have one policy established and need the new policy to be a backup in case some devices cannot support the stronger algorithms listed in the primary policy. What should be done in order to support this?
Which Cisco ASA deployment model is used to filter traffic between hosts in the same IP subnet using higher-level protocols without readdressing the network?
A switch with Dynamic ARP Inspection enabled has received a spoofed ARP response on a trusted interface.
How does the switch behave in this situation?
An organization is trying to implement micro-segmentation on the network and wants to be able to gain visibility on the applications within the network. The solution must be able to maintain and force compliance. Which product should be used to meet these requirements?
Which Cisco platform processes behavior baselines, monitors for deviations, and reviews for malicious processes in data center traffic and servers while performing software vulnerability detection?
Which cloud service model offers an environment for cloud consumers to develop and deploy applications
without needing to manage or maintain the underlying cloud infrastructure?
Based on the NIST 800-145 guide, which cloud architecture may be owned, managed, and operated by one or more of the organizations in the community, a third party, or some combination of them, and it may exist on or off premises?
Which network monitoring solution uses streams and pushes operational data to provide a near real-time view
of activity?
A company identified a phishing vulnerability during a pentest. What are two ways the company can protect employees from the attack? (Choose two.)
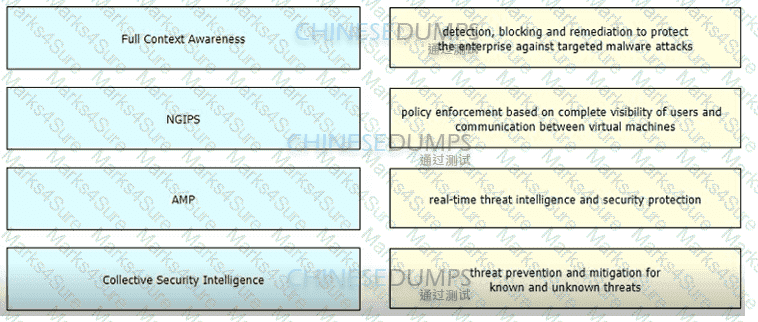
Drag and drop the features of Cisco ASA with Firepower from the left onto the benefits on the right.

Which threat involves software being used to gain unauthorized access to a computer system?
What are two functionalities of northbound and southbound APIs within Cisco SDN architecture? (Choose two.)
An attacker needs to perform reconnaissance on a target system to help gain access to it. The system has weak passwords, no encryption on the VPN links, and software bugs on the system’s applications. Which
vulnerability allows the attacker to see the passwords being transmitted in clear text?
A network security engineer must export packet captures from the Cisco FMC web browser while troubleshooting an issue. When navigating to the address https:// < FMC IP > /capure/CAPI/pcap/test.pcap, an error 403: Forbidden is given instead of the PCAP file. Which action must the engineer take to resolve this issue?
Which two criteria must a certificate meet before the WSA uses it to decrypt application traffic? (Choose two.)
Which kind of API that is used with Cisco DNA Center provisions SSIDs, QoS policies, and update software versions on switches?
A network administrator configures Dynamic ARP Inspection on a switch. After Dynamic ARP Inspection is applied, all users on that switch are unable to communicate with any destination. The network administrator checks the interface status of all interfaces, and there is no err-disabled interface. What is causing this problem?
Which two commands are required when configuring a flow-export action on a Cisco ASA? (Choose two.)
Which RADIUS feature provides a mechanism to change the AAA attributes of a session after it is
authenticated?
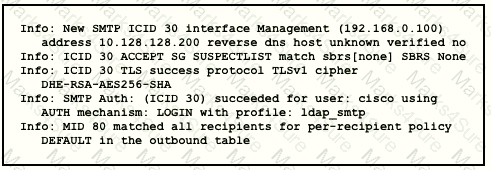
Refer to the exhibit. A network engineer must configure a Cisco router to send traps using SNMPv3. The engineer configures a remote user to receive traps and sets the security level to use authentication without privacy. Which command completes the configuration?
What is the function of the Internet Key Exchange (IKE) protocol in an IPsec VPN?
Which Cisco product provides proactive endpoint protection and allows administrators to centrally manage the
deployment?
What is a benefit of using telemetry over SNMP to configure new routers for monitoring purposes?
Which two request of REST API are valid on the Cisco ASA Platform? (Choose two)
Which feature of Cisco ASA allows VPN users to be postured against Cisco ISE without requiring an inline
posture node?
An organization has two systems in their DMZ that have an unencrypted link between them for communication.
The organization does not have a defined password policy and uses several default accounts on the systems.
The application used on those systems also have not gone through stringent code reviews. Which vulnerability
would help an attacker brute force their way into the systems?
When a next-generation endpoint security solution is selected for a company, what are two key
deliverables that help justify the implementation? (Choose two.)
An MDM provides which two advantages to an organization with regards to device management? (Choose two)
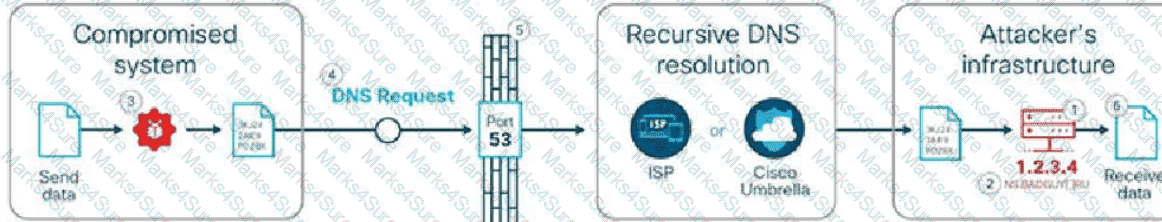
An administrator is configuring N I P on Cisco ASA via ASDM and needs to ensure that rogue NTP servers cannot insert themselves as the authoritative time source Which two steps must be taken to accomplish this task? (Choose two)
Which telemetry data captures variations seen within the flow, such as the packets TTL, IP/TCP flags, and payload length?
Which two components do southbound APIs use to communicate with downstream devices? (Choose two.)
Which two configurations must be made on Cisco ISE and on Cisco TrustSec devices to force a session to be adjusted after a policy change is made? (Choose two)
In which situation should an Endpoint Detection and Response solution be chosen versus an Endpoint Protection Platform?
A network engineer must distribute an operating system image to a network device and activate the image on that device by using the Cisco Catalyst Center API. Which two API requests perform the required operations? (Choose two.)
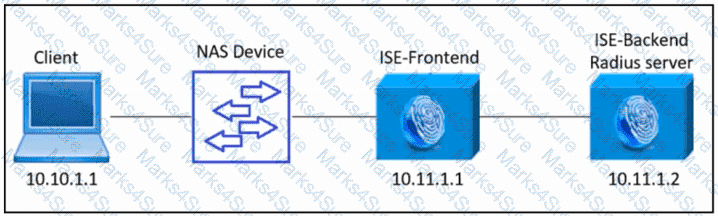
Refer to the exhibit. An engineer must configure a new Cisco ISE backend server as a RADIUS server to provide AAA for all access requests from the client to the ISE-Frontend server.
Which Cisco ISE configuration must be used?
What provides visibility and awareness into what is currently occurring on the network?
For a given policy in Cisco Umbrella, how should a customer block website based on a custom list?
A network engineer is deploying multiple Cisco Secure Firewall Threat Defense devices across two data centers. The solution has the following requirements:
Management must have no Internet dependency.
Management must remain accessible during major outages.
Policy management must be centralized.
Which solution must be implemented to meet the requirements?
Refer to the exhibit.
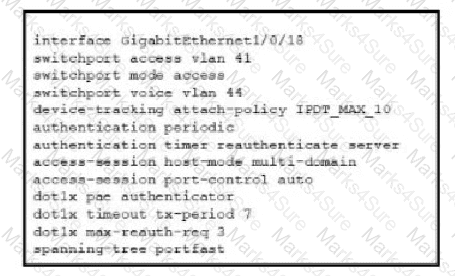
Refer to the exhibit. A Cisco ISE administrator adds a new switch to an 802.1X deployment and has difficulty with some endpoints gaining access.
Most PCs and IP phones can connect and authenticate using their machine certificate credentials. However printer and video cameras cannot base d on the interface configuration provided, what must be to get these devices on to the network using Cisco ISE for authentication and authorization while maintaining security controls?
Refer to the exhibit.
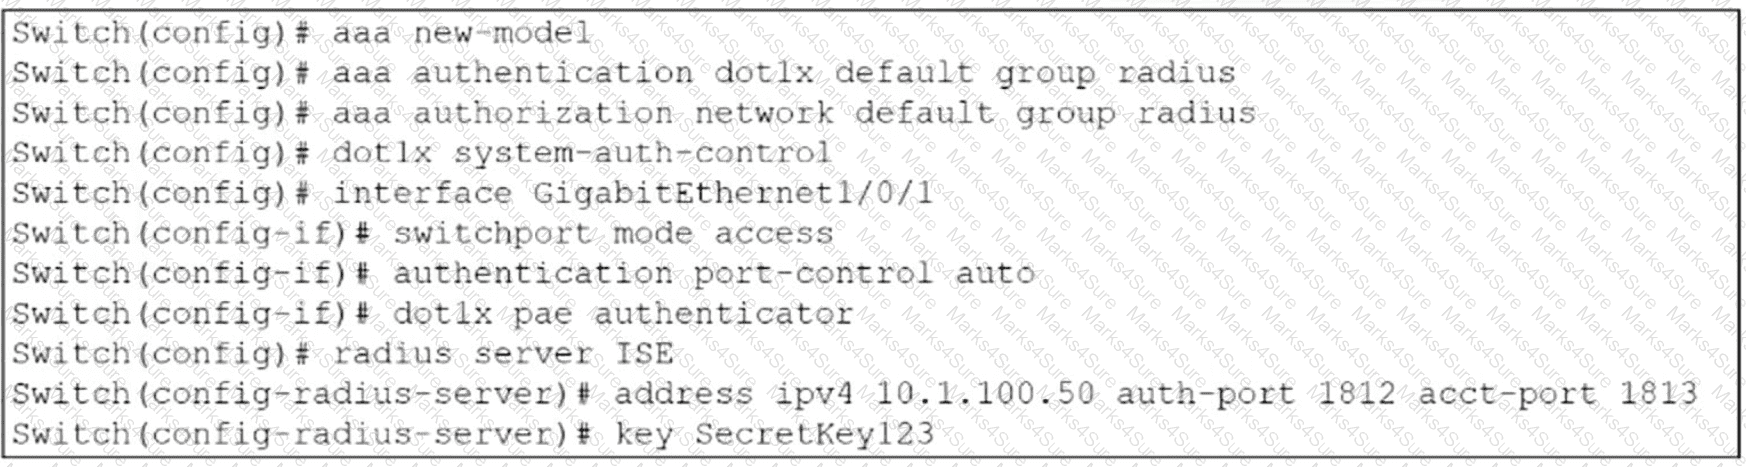
An engineer is implementing a network access control solution. Users can authenticate against the RADIUS server using 802.1X, and now the engineer wants to configure a downloadable access control list on the switchport using Cisco ISE. Which command must be used next on the Cisco Catalyst switch to complete the requirement?
An organization has DHCP servers set up to allocate IP addresses to clients on the LAN. What must be done to ensure the LAN switches prevent malicious DHCP traffic while also distributing IP addresses to the correct endpoints?
Refer to the exhibit.
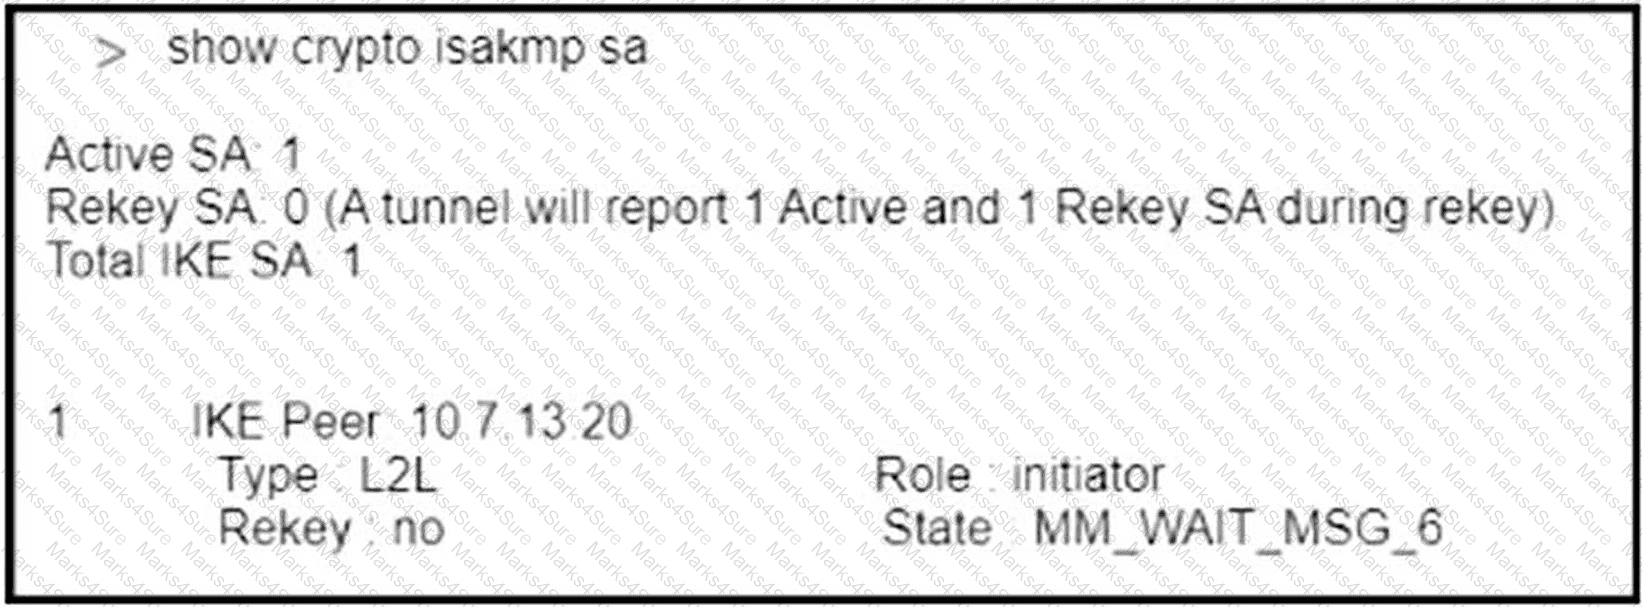
During the rollout of a new site-to-site VPN between a headquarters Cisco Secure Firewall Threat Defense device and a partner firewall, the tunnel never completes IKEv1 Phase 1 and remains in the MM_WAIT_MSG_6 state. Reachability between the firewalls over the Internet is verified, ISAKMP UDP port 500 is permitted end-to-end, and the IKE Phase 1 policy parameters—including encryption, hashing, DH group, and lifetime—match exactly on both ends. Which configuration action must be performed to resolve the issue?
A logistics company issues corporate laptops that must automatically establish a Cisco Secure Client VPN tunnel whenever users are outside the office and connected to an untrusted external network. Cisco Secure Firewall Threat Defense is the VPN headend and is already configured with remote-access profiles, address pools, and a PKI that distributes both machine and user certificates to endpoints. Management requires the tunnel to come up unattended before any user signs in to a laptop. Device-based authentication must be used, and the client must distinguish the corporate LAN from outside networks. The VPN must be connected when a user is outside the corporate network. Which configuration action must be performed to meet the requirements?
Which two preventive measures are used to control cross-site scripting? (Choose two)
What must be configured on Cisco Secure Endpoint to create a custom detection tile list to detect and quarantine future files?
A security engineer is deploying an IPsec site-to-site VPN between headquarters and a remote plant, protected by Cisco Secure Firewall Threat Defense managed by Cisco Secure Firewall Management Center. The following configurations have already been completed:
Matching IKEv2 proposals, preshared keys, and IPsec transform sets
Access control rules permitting the traffic
Crypto maps applied to the outside interfaces
VPN traffic exempted from inspection
During a packet capture on the firewall, the engineer observes that the traffic is translated to the public IP address, preventing tunnel establishment. Which configuration action must be performed next?
Which two services are provided by the Cisco Talos Incident Response group? (Choose two.)
Which type of dashboard does Cisco DNA Center provide for complete control of the network?
What is a functional difference between a Cisco ASA and a Cisco IOS router with Zone-based policy firewall?
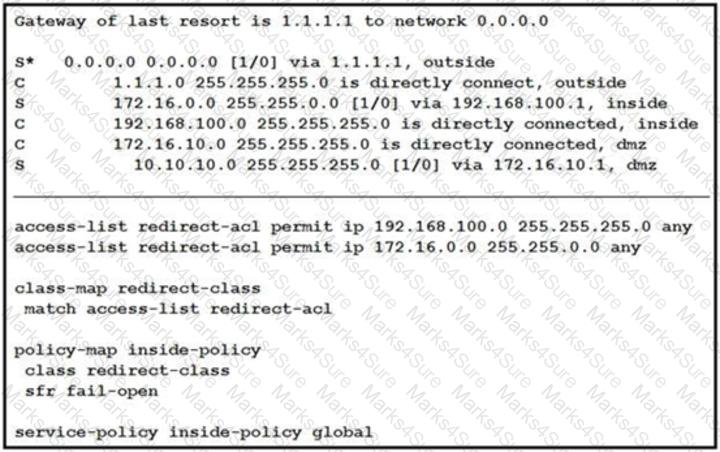
An engineer is configuring their router to send NetfFow data to Stealthwatch which has an IP address of 1 1 11 using the flow record Stea!thwatch406397954 command Which additional command is required to complete the flow record?
Which Secure Email Gateway implementation method segregates inbound and outbound email?
On Cisco Firepower Management Center, which policy is used to collect health modules alerts from managed
devices?
Which term describes when the Cisco Firepower downloads threat intelligence updates from Cisco Talos?
What do tools like Jenkins, Octopus Deploy, and Azure DevOps provide in terms of application and
infrastructure automation?
Which product allows Cisco FMC to push security intelligence observable to its sensors from other products?
Which Cisco security solution gives the most complete view of the relationships and evolution of Internet domains IPs, and flies, and helps to pinpoint attackers ' infrastructures and predict future threat?
Which Cisco DNA Center RESTful PNP API adds and claims a device into a workflow?
What provides the ability to program and monitor networks from somewhere other than the DNAC GUI?
A network engineer has been tasked with adding a new medical device to the network. Cisco ISE is being used as the NAC server, and the new device does not have a supplicant available. What must be done in order to securely connect this device to the network?
An engineer recently completed the system setup on a Cisco WSA Which URL information does the system send to SensorBase Network servers?
How does Cisco Workload Optimization Manager help mitigate application performance issues?
Refer to the exhibit.
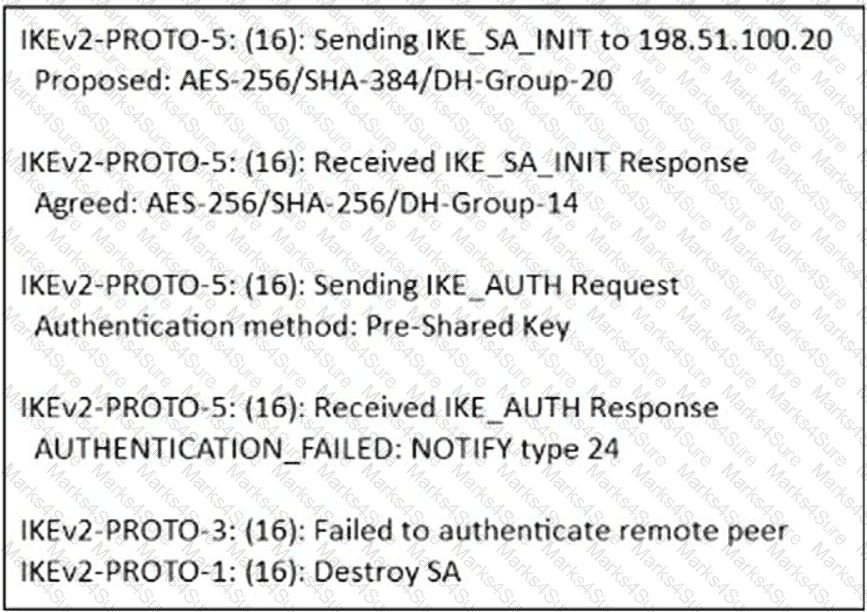
A site-to-site IKEv2 VPN between a Cisco Secure Firewall Threat Defense device with public IP address 203.0.113.10 and a third-party firewall with public IP address 198.51.100.20 is failing to establish at a logistics company. The engineer enables IKEv2 debugging on the FTD and captures the output. Which action must be performed to resolve the issue?
What are two characteristics of the RESTful architecture used within Cisco DNA Center? (Choose two.)
Refer to the exhibit.
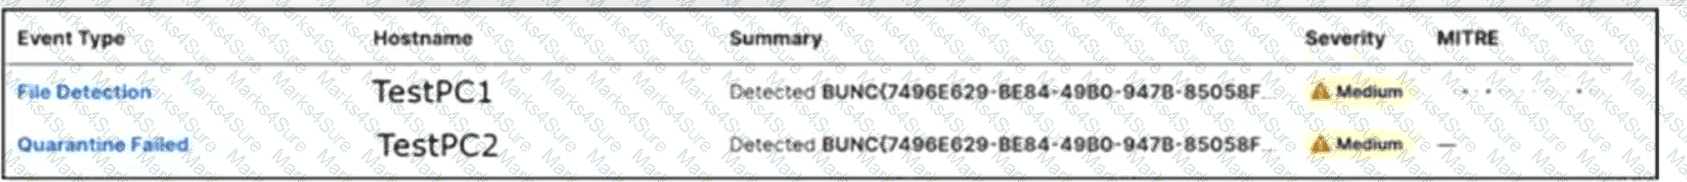
A Cisco Secure Endpoint malware event shows that a file was convicted as malicious and that its remediation status is Quarantine Failed. Before escalating the incident, the analyst must determine what can be concluded from the available event data. What is occurring based on the logs?
An engineer is configuring web filtering for a network using Cisco Umbrella Secure Internet Gateway.
The requirement is that all traffic needs to be filtered. Using the SSL decryption feature, which type of
certificate should be presented to the end-user to accomplish this goal?
What are the components of endpoint protection against social engineering attacks?
Which Cisco security solution secures public, private, hybrid, and community clouds?
An organization has a requirement to collect full metadata information about the traffic going through their AWS cloud services They want to use this information for behavior analytics and statistics Which two actions must be taken to implement this requirement? (Choose two.)
Which Talos reputation center allows for tracking the reputation of IP addresses for email and web traffic?
Which Splunk SOAR component automates multi-step security actions into a repeatable workflow?
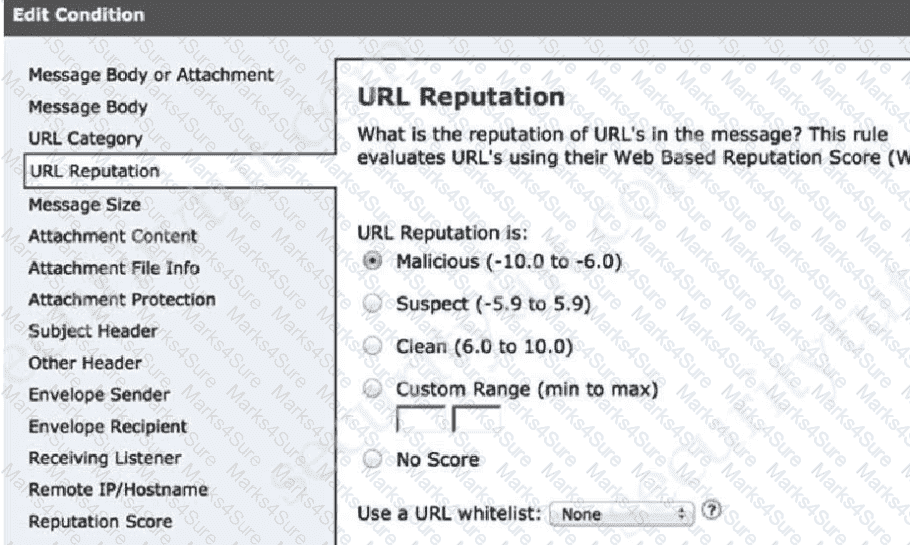
A network administrator is configuring a rule in an access control policy to block certain URLs and selects the “Chat and Instant Messaging” category. Which reputation score should be selected to accomplish this goal?
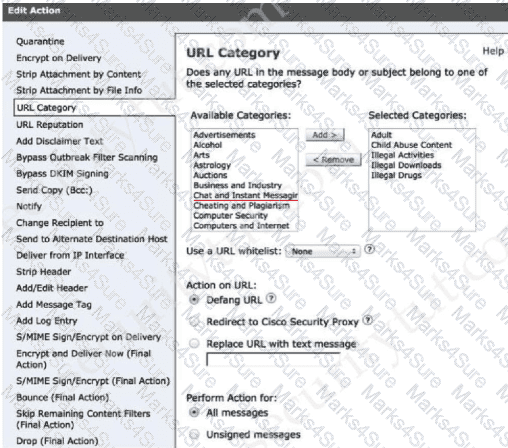
An engineer is deploying Cisco Advanced Malware Protection (AMP) for Endpoints and wants to create a policy that prevents users from executing file named abc424952615.exe without quarantining that file What type of Outbreak Control list must the SHA.-256 hash value for the file be added to in order to accomplish this?
Which Cisco cloud security software centrally manages policies on multiple platforms such as Cisco ASA, Cisco Firepower, Cisco Meraki, and AWS?
Which two types of policies are used by ZTNA to provide access to an application? (Choose two.)
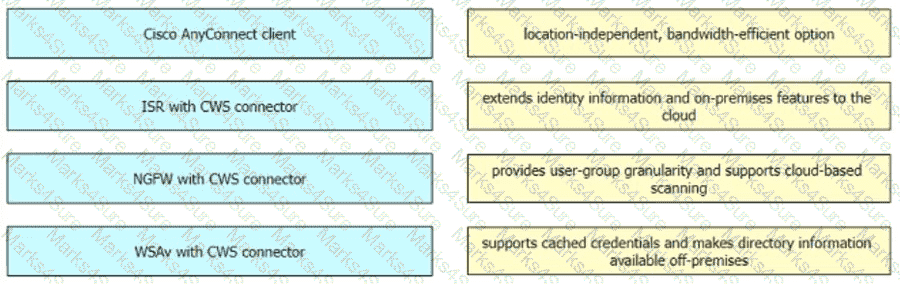
Drag and drop the Cisco CWS redirection options from the left onto the capabilities on the right.

Which type of API is being used when a controller within a software-defined network architecture dynamically
makes configuration changes on switches within the network?
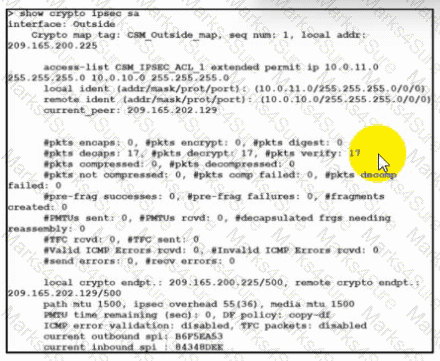
Refer to the exhibit. Traffic is not passing through IPsec site-to-site VPN on the Secure Firewall Threat Defense appliance. What is causing this issue?
Which Cisco product is open, scalable, and built on IETF standards to allow multiple security products from
Cisco and other vendors to share data and interoperate with each other?
Which two capabilities of Integration APIs are utilized with Cisco DNA center? (Choose two)
Which DevSecOps practice helps reduce vulnerabilities introduced through external open-source components?
An organization has two machines hosting web applications. Machine 1 is vulnerable to SQL injection while machine 2 is vulnerable to buffer overflows. What action would allow the attacker to gain access to machine 1 but not machine 2?
What provides total management for mobile and PC including managing inventory and device tracking, remote view, and live troubleshooting using the included native remote desktop support?
What is the purpose of the Decrypt for Application Detection feature within the WSA Decryption options?
A networking team must harden an organization ' s network from VLAN hopping attacks. The team disables Dynamic Trunking Protocol and puts any unused ports in an unused VLAN. A trunk port is used as a trunk link. What must the team configure next to harden the network against VLAN hopping attacks?
An organization is using Cisco Firepower and Cisco Meraki MX for network security and needs to centrally
manage cloud policies across these platforms. Which software should be used to accomplish this goal?
Refer to the exhibit.
=== Cisco Secure Endpoint - Detection Event ===
Endpoint : LAB-WKSTN-047 User: user1
Policy Group : Lab-Workstations Mode: Audit
Engine : ETHOS (fuzzy fingerprint)
Disposition : Malicious
File : C:\Users\user1\AppData\Local\Temp\svchost32.exe
SHA256 : 3a9f2c1d...e881b4a7
Parent Process: winword.exe
Threat Name : W32.Trojan.GenericKD.Agent
Retrospective : Previously UNKNOWN
Disposition changed to MALICIOUS at 09:31:55 UTC
File Activity : Created, Executed
Network : TCP outbound - > 91.205.188.47:4444
DNS query: c2-update.pharmadomain.ru
Quarantine : NOT quarantined (Audit mode active)
A security analyst at a pharmaceutical company is reviewing a Cisco Secure Endpoint malware-detection alert triggered on a laboratory workstation. The analyst observes the event data above. Which two things are occurring? (Choose two.)
With regard to RFC 5176 compliance, how many IETF attributes are supported by the RADIUS CoA feature?
A Cisco AMP for Endpoints administrator configures a custom detection policy to add specific MD5 signatures The configuration is created in the simple detection policy section, but it does not work What is the reason for this failure?
Which type of dashboard does Cisco Catalyst Center provide for complete control of the network?
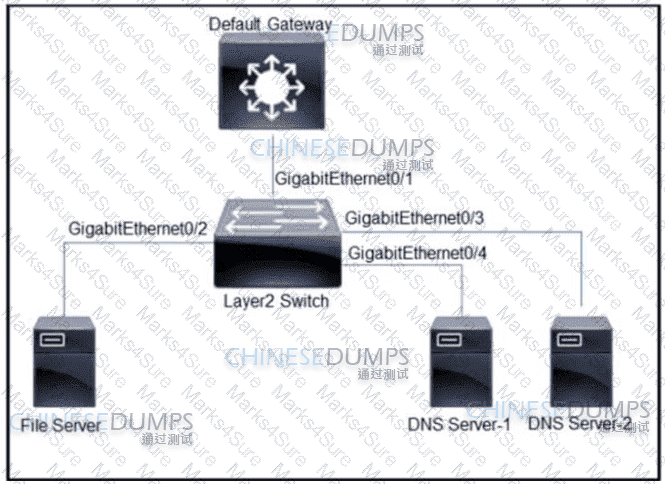
Refer to the exhibit. All servers are in the same VLAN/Subnet. DNS Server-1 and DNS Server-2 must communicate with each other, and all servers must communicate with default gateway multilayer switch. Which type of private VLAN ports should be configured to prevent communication between DNS servers and the file server?
Which two risks is a company vulnerable to if it does not have a well-established patching solution for
endpoints? (Choose two)
Which two deployment model configurations are supported for Cisco FTDv in AWS? (Choose two)
Which two request methods of REST API are valid on the Cisco ASA Platform? (Choose two.)
Which group within Cisco writes and publishes a weekly newsletter to help cybersecurity professionals remain
aware of the ongoing and most prevalent threats?
Which open source tool does Cisco use to create graphical visualizations of network telemetry on Cisco IOS XE devices?
What are two ways a network administrator transparently identifies users using Active Directory on the Cisco WSA? (Choose two.)
Which capability is exclusive to a Cisco AMP public cloud instance as compared to a private cloud instance?
What are two facts about WSA HTTP proxy configuration with a PAC file? (Choose two.)
A network engineer is configuring DMVPN and entered the crypto isakmp key cisc0380739941 address 0.0.0.0 command on hostA. The tunnel is not being established to hostB. What action is needed to authenticate the VPN?
Refer to the exhibit.
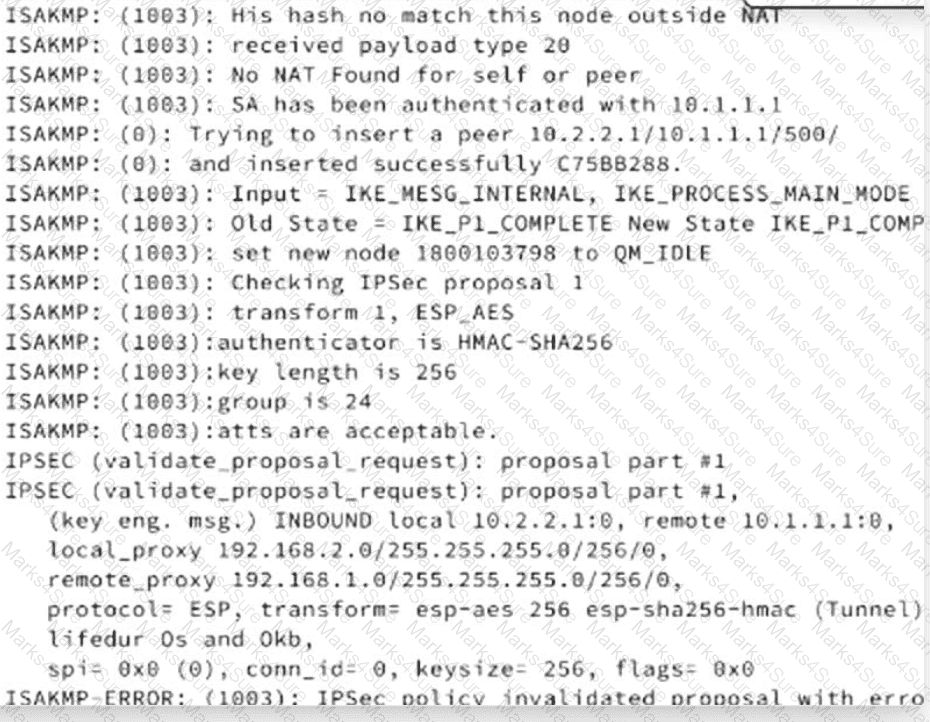
An engineer configures an IPsec VPN between two Cisco Secure Firewall Threat Defense devices named FTD1 and FTD2. However, the hosts behind FTD1 and FTD2 cannot communicate with each other. The engineer runs a debug command to troubleshoot the issue. What must be configured to resolve the issue?
What are the two types of managed Intercloud Fabric deployment models? (Choose two.)
An engineer is configuring Cisco Secure Endpoint to enhance security by preventing the execution of certain files by users. The engineer needs to ensure that the specific executable file name Cisco_Software_0505446151.exe is blocked from running while never being quarantined. What must the engineer configure to meet the requirement?
An administrator is trying to determine which applications are being used in the network but does not want the
network devices to send metadata to Cisco Firepower. Which feature should be used to accomplish this?
What is the primary difference between an Endpoint Protection Platform and an Endpoint Detection and
Response?
An administrator configures new authorization policies within Cisco ISE and has difficulty profiling the devices. Attributes for the new Cisco IP phones that are profiled based on the RADIUS authentication are seen however the attributes for CDP or DHCP are not. What should the administrator do to address this issue?
Which two authentication protocols are supported by the Cisco WSA? (Choose two.)
After deploying a Cisco ESA on your network, you notice that some messages fail to reach their destinations.
Which task can you perform to determine where each message was lost?
Which Cisco security solution integrates with cloud applications like Dropbox and Office 365 while protecting data from being exfiltrated?
An engineer is configuring IPsec VPN and needs an authentication protocol that is reliable and supports ACK
and sequence. Which protocol accomplishes this goal?
Refer to the exhibit.
A newly installed stack of Cisco Catalyst switches has been integrated with Cisco ISE for 802.1X port control and downloadable access control list (dACL) enforcement. Test workstations authenticate successfully, but the expected dACL never appears in the port configuration, leaving all traffic unrestricted. Packet captures confirm that Cisco ISE transmits the correct attributes, yet the switches classify them as “unknown” and ignore the instructions. A review of the running configuration shows complete AAA and 802.1X configuration. Which configuration command must be added to resolve the issue?
Which Cisco ASA Platform mode disables the threat detection features except for Advanced Threat Statistics?
A company discovered an attack propagating through their network via a file. A custom file policy was created in order to track this in the future and ensure no other endpoints execute the infected file. In addition, it was discovered during testing that the scans are not detecting the file as an indicator of compromise. What must be done in order to ensure that the created is functioning as it should?
Which Cisco Advanced Malware protection for Endpoints deployment architecture is designed to keep data
within a network perimeter?
An engineer integrates Cisco FMC and Cisco ISE using pxGrid Which role is assigned for Cisco FMC?
Which solution protects hybrid cloud deployment workloads with application visibility and segmentation?
A company is experiencing exfiltration of credit card numbers that are not being stored on-premise. The
company needs to be able to protect sensitive data throughout the full environment. Which tool should be used
to accomplish this goal?
An engineer is configuring Cisco WSA and needs to deploy it in transparent mode. Which configuration component must be used to accomplish this goal?
A security engineer requires social-media websites to be blocked through Cisco Secure Firewall Threat Defense. Which configuration action must the engineer apply to meet the requirement?
In which cloud services model is the customer responsible for scanning for and mitigation of application vulnerabilities?
Refer to the exhibit.
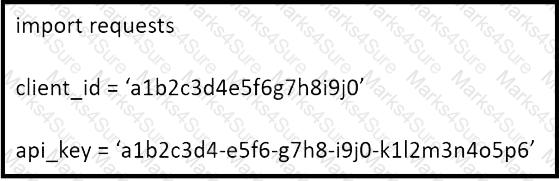
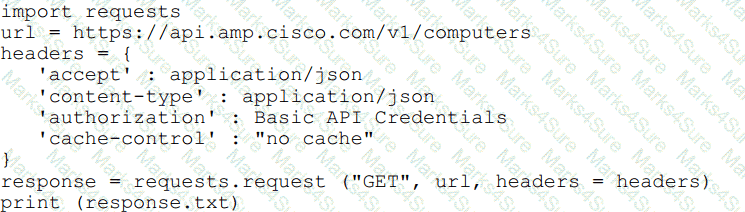
What does the API key do while working with https://api.amp.cisco.com/v1/computers?
What is the most common type of data exfiltration that organizations currently experience?
Which characteristic is unique to a Cisco WSAv as compared to a physical appliance?
An engineer must implement a file transfer solution between a company ' s data center and branches. The company has numerous servers hosted in a hybrid cloud implementation. The file transfer protocol must support authentication, protect the data against unauthorized access, and ensure that users cannot list directories or remove files remotely. Which protocol must be used?
An engineer has been tasked with implementing a solution that can be leveraged for securing the cloud users,
data, and applications. There is a requirement to use the Cisco cloud native CASB and cloud cybersecurity
platform. What should be used to meet these requirements?
Which technology provides a combination of endpoint protection endpoint detection, and response?
What are two reasons for implementing a multifactor authentication solution such as Duo Security provide to an
organization? (Choose two)
Which solution offers automated blocking of known threats and visibility into zero-day attack behavior, with the ability to respond directly from the console?
Which Cisco Umbrella package supports selective proxy for Inspection of traffic from risky domains?
An organization is selecting a cloud architecture and does not want to be responsible for patch management of the operating systems. Why should the organization select either Platform as a Service or Infrastructure as a Service for this environment?
A Cisco ESA network administrator has been tasked to use a newly installed service to help create policy based on the reputation verdict. During testing, it is discovered that the Cisco ESA is not dropping files that have an undetermined verdict. What is causing this issue?
An organization has noticed an increase in malicious content downloads and wants to use Cisco Umbrella to prevent this activity for suspicious domains while allowing normal web traffic. Which action will accomplish this task?
Which two services must remain as on-premises equipment when a hybrid email solution is deployed? (Choose two)
Which component of Cisco umbrella architecture increases reliability of the service?
Which solution stops unauthorized access to the system if a user ' s password is compromised?
In which two customer environments is the Cisco Secure Web Appliance Virtual connector traffic direction method selected? (Choose two.)
A network administrator needs to find out what assets currently exist on the network. Third-party systems need to be able to feed host data into Cisco Firepower. What must be configured to accomplish this?
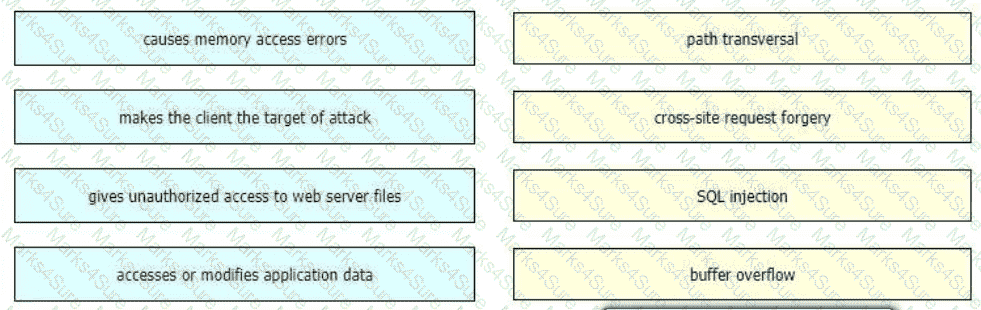
Drag and drop the exploits from the left onto the type of security vulnerability on the right.
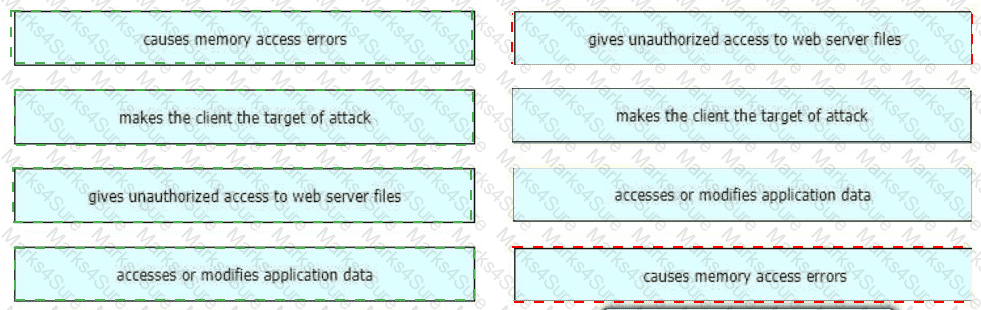
A network engineer is configuring a Cisco Catalyst switch. The network engineer must prevent traffic on the network from being interrupted by broadcast packets flooding the network using a predefined threshold. What must be configured on the switch?
An engineer is implementing NAC for LAN users on a segmented network. The engineer confirms that the device of each user is supported and the Cisco switch configuration is correct.
Which configuration should be made next to ensure there are no authentication issues?
A manufacturing company contracted an external software vendor to develop an application that dynamically creates marketing messages personalized to the business and audience. To ensure that communication between the sender and recipient email addresses does not create false positives, an exception rule must be configured in Cisco Secure Email Threat Defense. Which configuration must be performed?
Which ID store requires that a shadow user be created on Cisco ISE for the admin login to work?
Which two types of connectors are used to generate telemetry data from IPFIX records in a Cisco Secure Workload implementation? (Choose two.)
What is the Cisco API-based broker that helps reduce compromises, application risks, and data breaches in an environment that is not on-premise?
After a recent breach, an organization determined that phishing was used to gain initial access to the network before regaining persistence. The information gained from the phishing attack was a result of users visiting known malicious websites. What must be done in order to prevent this from happening in the future?
An organization must add new firewalls to its infrastructure and wants to use Cisco ASA or Cisco FTD.
The chosen firewalls must provide methods of blocking traffic that include offering the user the option to bypass the block for certain sites after displaying a warning page and to reset the connection. Which solution should the organization choose?
An engineer must implement an external application that authenticates against the Cisco Secure Email Threat Defense API to perform automated message searches. The application already presents a user bearer token, but the API requires an additional authentication header with each request. The engineer must configure the external application to include the required header alongside the bearer token so that the API calls are accepted. Which header must be configured?
A recent change left network engineers unable to SSH into a branch Cisco Catalyst switch. The engineer confirms that the TACACS server group TACACS-GROUP is defined but unreachable. There is no fallback to the local database when TACACS+ is unavailable. Security policy requires TACACS+ as the primary authentication method with automatic fallback to local accounts. Which configuration command must be added to resolve the issue?
Which two features of Cisco Email Security can protect your organization against email threats? (Choose two)
An engineer is configuring Cisco WSA and needs to enable a separated email transfer flow from the Internet and from the LAN. Which deployment mode must be used to accomplish this goal?
Which feature enforces continuous connectivity by preventing users from disconnecting the Cisco Secure Client tunnel?
Which type of API is being used when a security application notifies a controller within a software-defined network architecture about a specific security threat?
A healthcare organization is deploying Cisco Secure Access to prevent protected health information from being shared with generative AI services. The security team requires real-time DLP inspection only for traffic destined for AI applications, with minimal false positives during general web browsing. The policy must permit tuning based on the proximity and match counts of PHI identifiers. Which configuration action must the engineer perform?
PDF + Testing Engine
Testing Engine
PDF (Q&A)