Free Practice Questions for the CompTIA CySA+ CS0-004 Exam (2026 Updated)
At Marks4sure, we are dedicated to providing IT professionals with the most accurate and reliable preparation materials for the CompTIA CS0-004 exam. To support your certification journey, we have made a selection of our premium 2026 CompTIA CySA+ practice questions and answers available completely free. You can take this practice test as many times as you need. Every question includes a detailed, expertly verified explanation to ensure you fully grasp the core security concepts before test day.
Which of the following is the most likely reason an organization might implement compensating controls?
Which of the following allows an organization to leverage AI in various forms while protecting business objectives and data?
Which of the following is the most important component to include in the preparation phase of an incident response plan?
An analyst is assigned to a new cybersecurity improvement project. The analyst wants to better understand the workflow processes and the skill set of the cybersecurity engineers on this task force. The analyst sets up a recurring, weekly conference call.
Which of the following best describes the purpose for the conference call?
The vulnerability management team must scan the cloud environment to establish security baselines.
Which of the following assessment tools should the team use to perform this task?
A security operations center analyst is using the command line to display specific traffic.
The analyst uses the following command:
$tshark -r file.pcap -Y "http or udp"
Which of the following will the command line display?
Which of the following phases of the incident response process will permanently remove an attacker’s access to corporate resources?
A security operations center (SOC) manager makes significant updates to the incident response plan and wants to test these updates with all stakeholders collaboratively.
Which of the following is the best way to accomplish this task?
Despite removing malware from some of the affected hosts, several of an organization's internal resources are still unavailable two weeks after the discovery of a major incident.
Which of the following best describes this phase?
A Chief Information Security Officer (CISO) is notified of an ongoing incident.
Which of the following explains why the CISO instructs the Chief Executive Officer not to discuss the incident over email?
Which of the following best explains why sensitive data should be encrypted at rest on laptops?
Which of the following is the most difficult for threat actors to change according to the Pyramid of Pain model?
Which of the following is the most comprehensive type of report associated with a closed incident?
A cybersecurity analyst receives an unstructured text document that contains advanced persistent threat (APT)-related indicators of compromise (IoCs). The analyst needs to extract the IPv4 addresses.
Which of the following is the best tool to accomplish this task?
A security analyst uses a full pcap solution to extract all traffic from the last two days associated with the 10.213.4.27 file server.
This file server is under investigation due to concerns about potential data exfiltration using Domain Name System (DNS) traffic.
Which of the following commands should the analyst use to extract any potentially leaked data from the suspicious.pcap file?
A cybersecurity analyst requests a paid subscription to a threat intelligence feed relevant to a company's industry.
Which of the following best describes this type of feed?
An analyst uses an AI platform to help correlate events. The AI output contains events that did not happen. This results in inaccurate correlations.
Which of the following best describes what has occurred?
A security analyst must identify documents that contain encoded ActiveMime payloads in a directory containing thousands of files. The analyst runs the following command: grep -rail ActiveMime *
The command returns no output.
Which of the following Yet Another Recursive Acronym (YARA) rules should the analyst use to find the suspicious files?
A)
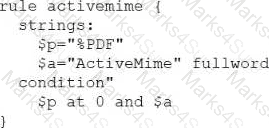
B)
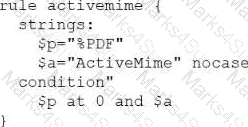
C)
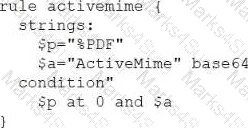
D)
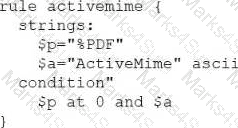
A binary file that might contain malicious code is hosted on an isolated machine. An analyst wants to quickly detect the malicious code.
Which of the following should the analyst use?
A security analyst receives a notice about a possible data breach. The report identifies unapproved, current access dates for files found in the following personnel archives:

Which of the following actions should the analyst take first?
A security analyst runs an Nmap scan against a host with multiple open ports using the following command:
nmap 10.10.10.1 -p-
The following output is obtained after the scan:
Starting Nmap 7.95 ( https://nmap.org ) at 2025-07-15 15:55 UTC
Note: Host seems down.
Nmap done: 1 IP address (0 hosts up) scanned in 3.16 seconds
Which of the following is the most accurate way to scan the target IP for open ports?
PDF + Testing Engine
Testing Engine
PDF (Q&A)