Black Friday Flash Sale: Get 70% Off! Use coupon code below to save big on all exam bundles! Use coupon code below to save on all exam bundles!
Code: bestfriday
Ends in: 0d 00h 00m 00s

Free Practice Questions for the ISTQB Tester Security CT-STE Exam (2026 Updated)

At Marks4sure, we are dedicated to providing IT professionals with the most accurate and reliable preparation materials for the ISTQB CT-STE exam. To support your certification journey, we have made a selection of our premium 2026 ISTQB Tester Security practice questions and answers available completely free. You can take this practice test as many times as you need. Every question includes a detailed, expertly verified explanation to ensure you fully grasp the core security concepts before test day.

Questions 4

Why do test oracles derived from standards and best practices benefit security testers?

Options:

A.

Best practices may determine expected results, which can be used as evidence of the application being secure or insecure.

B.

Standards may describe the way the test oracles should be formally defined and implemented.

C.

Best practices are an effective way to specify security requirements for software development.

D.

Standards are established by a consensus of subject matter experts and approved by a recognized body.

Buy Now
Questions 5

A tester used rainbow tables in a brute-force attack to uncover user passwords. What type of testing is this?

Options:

A.

Testing the authentication mechanism.

B.

Testing the accounting mechanism.

C.

Testing the authorization mechanism.

D.

Testing the system hardening mechanism.

Buy Now
Questions 6

Why should security-testing activities be planned with the software development lifecycle in mind?

Options:

A.

To identify security risk mitigation actions.

B.

To better identify and assess security risks.

C.

To make security testing more effective.

D.

To determine security test design techniques.

Buy Now
Questions 7

As a security tester, you established the following test prioritization:
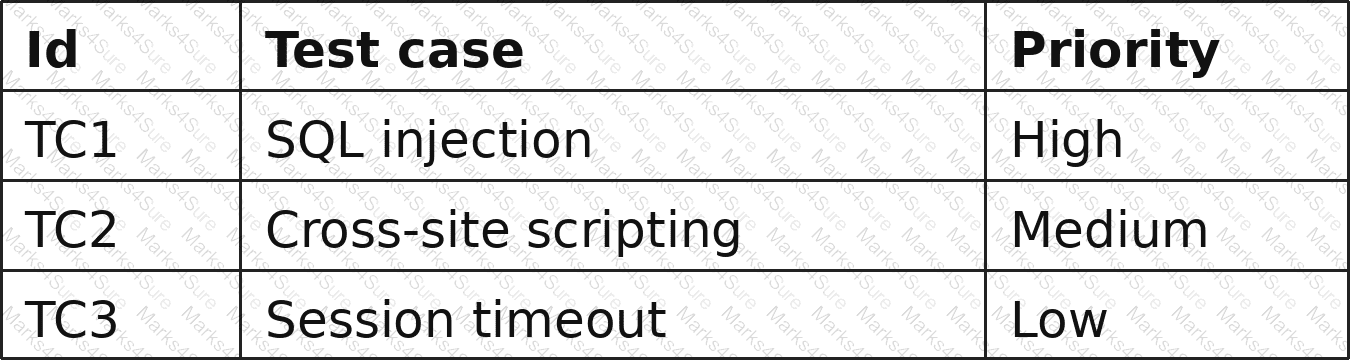
CT-STE Question 7

During which activity of the security test process was this action carried out?

Options:

A.

Security test analysis.

B.

Security test implementation.

C.

Security test planning.

D.

Security test design.

Buy Now
Questions 8

Which of the following illustrates grey-box security testing?

Options:

A.

A security test of a web application attempting to exploit file upload flaws by interacting with the application’s user interface without any access to the application’s source code.

B.

A network security audit performed by a security tester with no prior knowledge of the application or its infrastructure aimed to identify open ports or weak authentication.

C.

A network penetration test using partial knowledge of the system architecture to try to exploit vulnerabilities while remaining unaware of the system’s configuration and code details.

D.

A source code review of a web application, performed by the security test team, aimed to identify vulnerabilities such as SQL injection, with access to the application’s database.

Buy Now
Questions 9

An e-commerce website includes an integrated product inventory management system that communicates with an internal server to verify product availability. The system is complex, has a complicated architecture, and contains many interconnected components.

Because of a flaw in processing user-provided URLs, an attacker can manipulate a URL input to cause unauthorized internal requests to the server. This is an example of a Server-Side Request Forgery (SSRF) vulnerability.

You have only just discovered this vulnerability and have little time to improve this version of the software before delivering it to the customer.

What is the BEST technique for handling this vulnerability in the scenario described above?

Options:

A.

Avoid vulnerability by identifying and executing the risk mitigation actions.

B.

Redesign the system’s architecture and implement a new, corrected version.

C.

Hide vulnerability by blocking traffic on a firewall.

D.

Do nothing since the risk level is low.

Buy Now
Questions 10

You test a system that sends documents containing sensitive data between users. One risk is that an attacker who obtains access to such a document could read its contents.

What type of testing verifies a mechanism that prevents unauthorized persons from reading documents?

Options:

A.

Conformance testing of digital signatures.

B.

Conformance testing of public key encryption.

C.

Code reviews aiming to detect SQL injection.

D.

Brute force testing using rainbow tables.

Buy Now
Exam Code: CT-STE
Exam Name: Certified Tester Security Test Engineer
Last Update: Nov 22, 2026
Questions: 40

PDF + Testing Engine

$55.71   $185.69

Testing Engine

$42.85   $142.83

PDF (Q&A)

$47.13   $157.11