Free Practice Questions for the WGU Courses and Certificates Cybersecurity-Architecture-and-Engineering Exam (2026 Updated)
At Marks4sure, we are dedicated to providing IT professionals with the most accurate and reliable preparation materials for the WGU Cybersecurity-Architecture-and-Engineering exam. To support your certification journey, we have made a selection of our premium 2026 Courses and Certificates practice questions and answers available completely free. You can take this practice test as many times as you need. Every question includes a detailed, expertly verified explanation to ensure you fully grasp the core security concepts before test day.
An organization wants to implement a new encryption solution for a real-time video conferencing application. The organization wants to ensure that the encryption solution provides protection for the video stream without causing significant delays or latency in the conference.
Which type of encryption will meet the needs of the organization?
An IT organization has recently suffered multiple data breaches. The security operations center (SOC) team has been tasked with preventing future breaches by implementing user monitoring. The proposed solution must provide insights about unusual user behaviors from a variety of internal corporate resources.
Which solution meets the requirements?
A software development company is concerned about the potential risks associated with exploits that target vulnerabilities in the Linux operating system used by the company’s servers. The company has decided to implement hardening techniques and endpoint security controls to mitigate the risk.
Which hardening technique will meet the needs of this company?
Which algorithm is suitable for ensuring the integrity of digital documents and detecting any unauthorized modifications?
Which key exchange algorithm is based on advanced cryptography algorithms and is a more efficient alternative to traditional key exchange algorithms?
Which risk management strategy will supplement privacy requirements for data on an electronic health record (EHR) system?
An IT organization is deploying a new secure Simple Mail Transfer Protocol (SMTP) server to handle email communications for the company. The company must ensure that the servers are secure and protected from external threats. The SMTP servers should be able to communicate with the internal network and the internet, but all incoming and outgoing traffic should be inspected and filtered to prevent cyberattacks.
An IT team must allow on-premises users to log in to the Azure portal using their corporate credentials.
Which strategy should be used to enable identity federation in this scenario?
While undergoing a security audit, it is determined that an organization has several backup repositories nested in the cloud without any level of protection. Which action should be taken to protect the backup repositories first?
Which item information should be stored in a database to determine an order total?
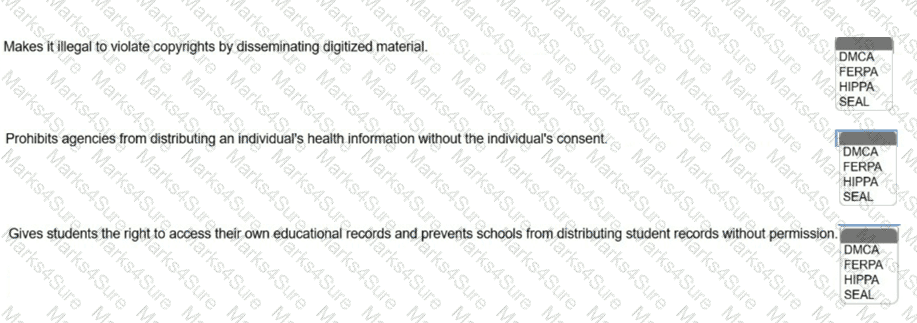
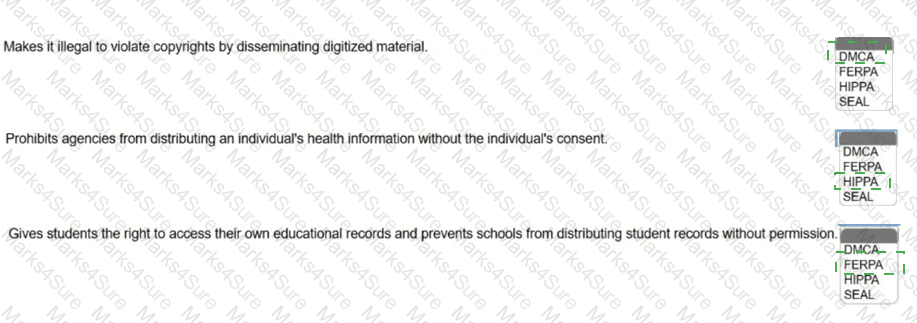
Match the legislative purpose with the corresponding legislation.
Answer options may be used more than once or not at all.
A company is looking to monitor and detect any suspicious activity on its servers. The company wants to implement a security solution that can detect any unauthorized access or unusual activity on the servers.
Which security technology will meet the needs of this company?
An e-learning company uses Amazon Simple Storage Service (Amazon S3) to store e-books and video files that are served to customers through a custom application. The company has realized that someone has been stealing its intellectual property.
Which threat actor is most likely in this scenario?
After a recent security assessment, it was discovered that many company devices have unnecessary ports opened to the network.
What should the company configure to fix this?
A cybersecurity analyst at a healthcare organization was tasked with analyzing the indicators of compromise (IOCs) to identify potential threats and vulnerabilities within the enterprise. Theanalyst notices unknown users logging on to the company's wireless local-area network (WLAN).
What is a potential vulnerability the healthcare organization is facing based on the IOCs identified?
A company has identified a potential risk associated with a new software implementation, which could result in a significant data breach.
Which step of the risk management life cycle involves implementing security controls to prevent the risk?
A small start-up is setting up its first network, and it needs to ensure that its network security is adequate. The start-up is aware of the latest cybersecurity threats and the need for strong security measures. In addition to network security, the start-up wants to ensure that it has a disaster recovery plan in place in case of any unexpected events.
Which approach will meet the needs of the start-up?
The cybersecurity analyst at a hardware company conducted a vulnerability assessment to identify potential security risks to the organization and discovered multiple vulnerabilities on the company's webpage. The analyst then provided the results to the chief information security officer (CISO), who then decided to decommission the website and create a new page with increased security controls.
Which risk mitigation strategy is demonstrated in this scenario?
Which IT role is responsible for the installation and maintenance of hardware and software that make up a computer network?
An organization sends customers e-mail messages based on their purchase patterns.
Which characteristic of quality data does this represent?
A cloud service provider is concerned about the potential risks associated with hardware-based attacks on its virtual machines. The provider has decided to implement hardening techniques and endpoint security controls to mitigate the risk.
Which hardening technique will meet the needs of this provider?
What are two differences between a handheld computer and a desktop?
Choose 2 answers.
Which system conversion method deploys the new system while the old system is still operational in order to compare output?
An IT team has been tasked with improving the security of a company’s web applications.
Which threats should the IT team consider detecting when defending the network with a web application firewall (WAF)?
A healthcare provider is required to comply with the Health Insurance Portability and Accountability Act (HIPAA), which sets requirements for the protection of patient health information. The provider uses various software applications to manage and store patient health information, which must be coded to protect its confidentiality and integrity.
Which protocol will meet the needs of this provider?
What does the following SQL statement produce when executed?
SELECT ‘ FROM Customers
WHERE State = 'Arizona';
A company has recently implemented a hybrid cloud deployment. The security team has been notified about thousands of failed attempts to connect to routers and switches in the on-premises network. A solution must be implemented to block connections after three unsuccessful SSH attempts on any network device.
Which block cipher mode of operation for encrypting data is simple and efficient and provides no confidentiality beyond that of the underlying block cipher?
A software development company uses file transfer protocol (FTP) to transfer software code between different teams.
Which security control is essential for protecting the integrity of software code that is transferred using FTP?
Which IT role is responsible for installing new hardware and troubleshooting existing hardware?
An organization wants to implement a new encryption solution to protect sensitive data stored in a database. The organization wants to ensure that the encryption solution provides strong protection for the data and is willing to sacrifice performance.
Which type of encryption meets the needs of the organization?
An IT organization recently implemented a hybrid cloud deployment. The security team must be able to correlate event data combined from different sources in a central location.
What is the best solution?
A cloud hosting provider is concerned about the potential risks associated with attacks that target the confidentiality and integrity of sensitive data stored on its servers’ volatile memory. The provider has decided to implement hardening techniques and endpoint security controls to mitigate the risk.
Which hardening technique will meet the needs of this provider?
An application team manages a large farm of web servers on virtual machines in the cloud. The team wants to reduce the server load by caching static content. Adding a second layer of protection is also a requirement.
What should this team recommend in this scenario?
A healthcare provider is required to comply with the Health Insurance Portability and Accountability Act (HIPAA), which sets requirements for the protection of patient health information. The provider uses various software applications to manage and store patient health information, which must be coded to protect its confidentiality and integrity.
Which protocol will meet the needs of this provider?
A project manager is working on a project that involves securing the network of a tall building. The manager is tasked with managing these risks effectively to ensure the successful completion of the project within a given time frame and budget. The manager identified multiple potential risks associated with the project.
What is the next step in the risk management life cycle?
Which type of systems testing includes having end users test the system with simulated data and the help of the developer?
A government agency needs to deploy a secure network connection between its offices in Chicago and New York.
What should be used to facilitate this connection?
The DevSecOps team for an organization manages a continuous integration and continuous deployment (CI/CD) pipeline for a three-tier web application. Management has asked the team to perform a series of comprehensive post-deployment tests to make sure that all of the components of the application can interact and function properly.
Which risk management strategy will ensure the secure configuration and deployment of a new online banking system and help prevent credit card fraud?
An organization needs to securely exchange confidential documents with a third-party vendor overan unsecured network connection. The organization wants to ensure that the documents can only be read by the intended recipient and cannot be intercepted or read by unauthorized parties.
Which type of encryption meets the needs of the organization?
An organization's engineering team is developing a mobile application that uses near-field communication (NFC) capabilities but wants to ensure that information communicated using this protocol remains confidential.
Which risk management strategy will ensure that data stored on an Enterprise Resource Planning (ERP) system is secure from exploitation in the event of a data breach?
The security team has been notified about multiple man-in-the-middle (MITM) attacks happening on the wireless network over the past thirty days. Management has agreed to upgrade the network infrastructure to help eliminate these attacks.
Which solution fulfills these requirements?
A professional services organization deployed security edge devices in key locations on its corporate network.
How will these devices improve the organization's security posture?
Which stream cipher is a variant of the Salsa20 cipher, designed to be fast, secure, and resistant to cryptanalysis, and is commonly used in combination with the Poly1305 authentication mode?
An engineer has noticed increased network traffic originating from an unknown internet protocol (IP) address.
Which action should be taken to analyze the unusual network traffic patterns?
An IT organization has seen a surge of ransomware and Trojan horse attacks recently.
Which action should the security team recommend to protect the IT infrastructure from commodity malware threats?
While undergoing a security audit, it is determined that an organization has several backup repositories hosted in the cloud without any level of protection.
Which action should be taken to protect the backup repositories first?
A company wants to secure its computer systems and prevent any unauthorized access to its network. The company wants to implement a security solution that can restrict network traffic to only approved services and applications.
Which security technology will meet the needs of this company?
A company is developing a new system to process personal information about its customers, including their names, addresses, and purchase histories.
Which term describes the process of identifying and evaluating the potential effects that the new system may have on the privacy of personal information and developing strategies to mitigate those risks?
An IT organization needs to enable secure communication across virtual networks in Microsoft Azure and Amazon Web Services.
Which protocol will offer the most reliable and secure method for data transport?
A financial institution conducted a cybersecurity assessment, which identified several vulnerabilities, including outdated software and weak password policies. The company also needs to implement a new core banking system that can handle a large number of transactions while ensuring the security of customer data.
Which risk mitigation process is the most effective approach to address these vulnerabilities, and what is the best topology for the new core banking system?
The security team has been notified about multiple man-in-the-middle (MITM) attacks happening on the wireless network over the past thirty days. Management has agreed to upgrade the network infrastructure to help eliminate these attacks.
An on-call security engineer has been notified after business hours that a possible threat could be impacting production applications.
Which type of threat intelligence should be used by first responders?
Which risk management strategy will ensure the secure storage of data on a new document management system?
A cybersecurity analyst at a manufacturing company is tasked with analyzing the Indicators of Compromise (IOCs) to identify potential threats and vulnerabilities within the organization. While viewing the Security Information and Event Management (SIEM), the analyst notices an unknown IP address logging in to the company's Secure Shell (SSH) server.
A large healthcare provider is acquiring a small clinic and has identified a full understanding of the clinic's organizational risks. The large provider has several tools it can implement to reduce the clinic's identified risks.
Which type of risk response should the healthcare provider use?
An employee needs to execute a program from the command line.
Which peripheral device should be used?
PDF + Testing Engine
Testing Engine
PDF (Q&A)