Free Practice Questions for the Juniper JNCIS-SEC JN0-336 Exam (2026 Updated)
At Marks4sure, we are dedicated to providing IT professionals with the most accurate and reliable preparation materials for the Juniper JN0-336 exam. To support your certification journey, we have made a selection of our premium 2026 JNCIS-SEC practice questions and answers available completely free. You can take this practice test as many times as you need. Every question includes a detailed, expertly verified explanation to ensure you fully grasp the core security concepts before test day.
In Juniper high availability (HA) SRX Series device implementations, which interface will be used to exchange session state, configuration files, and ensure session continuity across nodes using the proprietary Trivial Network Protocol?
You need to deploy an SRX Series device in your virtual environment.
In this scenario, what are two benefits of using a CSRX? (Choose two.)
When using Adaptive Threat Profiling, which two deployment modes are available on SRX Series devices? (Choose two.)
Which two statements are correct about client-protection Secure Socket Layer (SSL) proxy configurations? (Choose two.)
You need to secure communications from a mobile command center which uses a 5G mobile ISP behind CGNAT to an SRX Series Firewall at headquarters.
Which two actions should be performed on the SRX Series Firewall in this scenario? (Choose two.)
You are asked to configure your company SRX Series device to use identity-aware security policies. Information about your Active Directory network is shown in the exhibit.
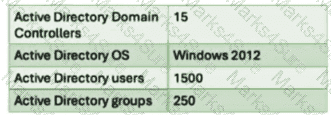
In this scenario, why must you configure JIMS instead of Active Directory as an identity source?
You are establishing an IPsec VPN and must ensure that payload data is encrypted.
In this scenario, which IPsec security protocol should you configure?
Which two statements accurately describe the role of hashing in VPNs? (Choose two.)
Which two statements are correct about the security associations of an IPsec VPN? (Choose two.)
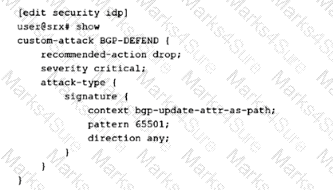
Which action will the SRX Series device take if traffic matches the custom attack object shown in the exhibit?
Which two statements are correct about fabric interfaces on an SRX Series Firewall? (Choose two.)
What are two types of attack objects included in an IDP attack object database? (Choose two.)
PDF + Testing Engine
Testing Engine
PDF (Q&A)