Free Practice Questions for the Fortinet NSE 5 Network Security Analyst NSE5_FWB_AD-8.0 Exam (2026 Updated)
At Marks4sure, we are dedicated to providing IT professionals with the most accurate and reliable preparation materials for the Fortinet NSE5_FWB_AD-8.0 exam. To support your certification journey, we have made a selection of our premium 2026 NSE 5 Network Security Analyst practice questions and answers available completely free. You can take this practice test as many times as you need. Every question includes a detailed, expertly verified explanation to ensure you fully grasp the core security concepts before test day.
You are reviewing a report from your FortiWeb logs and notice a JavaScript payload like < script > document.cookie < /script > is submitted through a product review form. The page doesn’t filter the script, and when users view the review, their session cookies are exposed.
Why is this attack dangerous?
FortiWeb is blocking groups of users behind your load balancer. In the logs, all users show the same source IP address.
Which action should you take to restore proper client identification?
You are reviewing SSL-related issues on FortiWeb. An administrator reports that they receive a certificate warning when they access the FortiWeb GUI over HTTPS. Separately, your FortiWeb device also makes outbound HTTPS requests to a back-end API server.
In which two situations would FortiWeb use its own certificates to establish or secure the connection? (Choose two.)
You are setting up a FortiWeb policy to protect a customer login portal. Users connect to https://login.training.lab, and you want FortiWeb to forward those requests to a load-balanced pool of back-end servers.
Which three components must you configure to complete the server policy?
You have configured parameter validation, file security, and machine learning (ML) anomaly detection for a web form, but some server-side request forgery tests are still succeeding. You need to advise the team on what to prioritize next to improve SSRF protection without compromising other parts of the application.
Which recommendation would best strengthen FortiWeb’s ability to block remaining SSRF attempts?
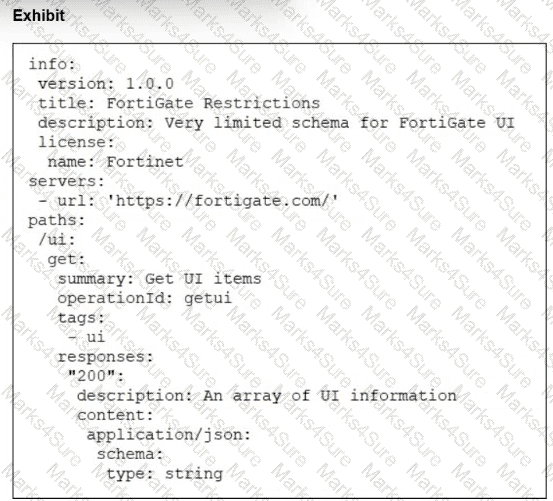
Refer to the exhibits.
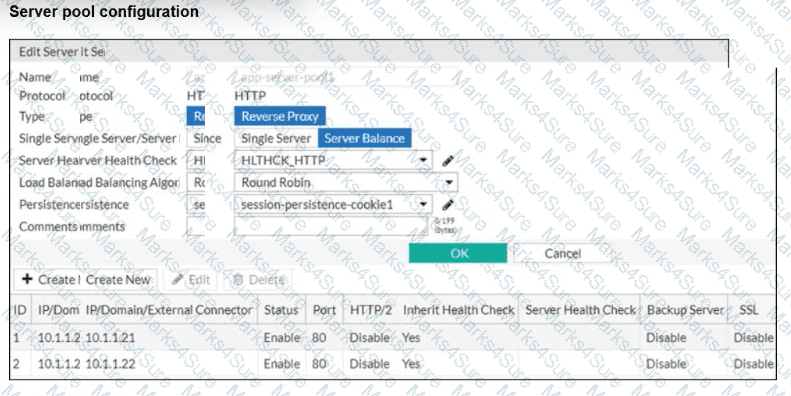
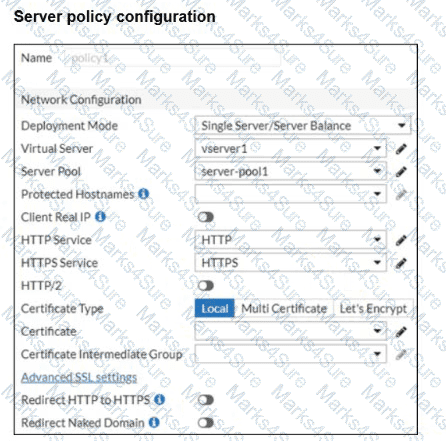
You are configuring a FortiWeb device in reverse proxy mode, placed downstream from a FortiGate. The server pool includes two back-end web servers: 10.1.1.21 and 10.1.1.22, and you’ve defined a health check policy.
After completing the server policy configuration and applying it to a virtual server, you notice that FortiWeb is not forwarding traffic to the back-end servers. No errors or health check failures appear in the logs.
Based on the configuration shown in the exhibit, which change should you make to restore back-end traffic flow?
PDF + Testing Engine
Testing Engine
PDF (Q&A)