Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: pass65

Free Practice Questions for the Fortinet Network Security Expert NSE7_CDS_AR-7.6 Exam (2026 Updated)

At Marks4sure, we are dedicated to providing IT professionals with the most accurate and reliable preparation materials for the Fortinet NSE7_CDS_AR-7.6 exam. To support your certification journey, we have made a selection of our premium 2026 Fortinet Network Security Expert practice questions and answers available completely free. You can take this practice test as many times as you need. Every question includes a detailed, expertly verified explanation to ensure you fully grasp the core security concepts before test day.

Questions 4

You must add an Amazon Web Services (AWS) network access list (NACL) rule to allow SSH traffic to a subnet for temporary testing purposes. When you review the current inbound and outbound NACL rules, you notice that the rules with number 5 deny SSH and telnet traffic to the subnet.

What can you do to allow SSH traffic?

Options:

A.

You do not have to create any NACL rules because the default security group rule automatically allows SSH traffic to the subnet.

B.

You must create a new allow SSH rule anywhere in the network ACL rule base to allow SSH traffic.

C.

You must create two new allow SSH rules, each with a number bigger than 5.

D.

You must create two new allow SSH rules, each with a number smaller than 5.

Buy Now
Questions 5

Refer to the exhibit.

NSE7_CDS_AR-7.6 Question 5

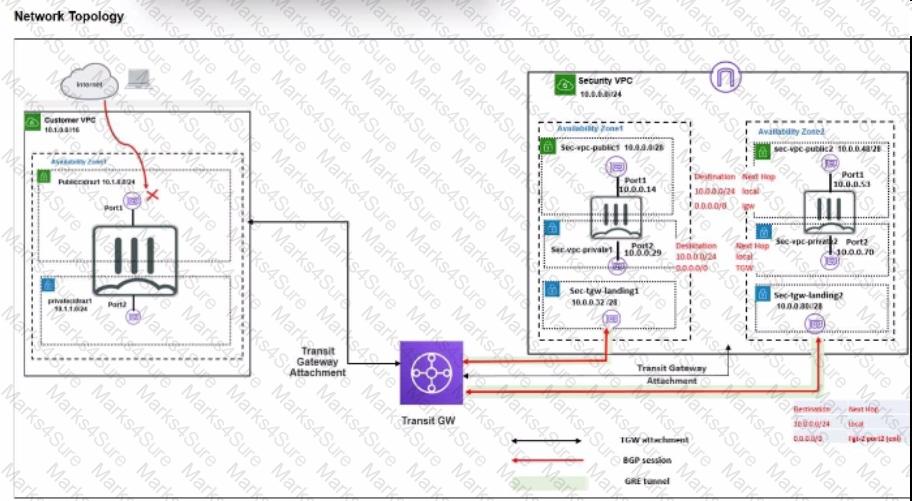
In your Amazon Web Services (AWS), you must allow inbound HTTPS access to the Customer VPC FortiGate VM from the internet. However, your HTTPS connection to the FortiGate VM in the Customer VPC is not successful.

Also, you must ensure that the Customer VPC FortiGate VM sends all the outbound Internet traffic through the Security VPC.

How do you correct this issue with minimal configuration changes? (Choose three.)

Options:

A.

Add a route with your local internet public IP address as the destination and the internet gateway as the target.

B.

Add a route with your local internet public IP address as the destination and the transit gateway as the target.

C.

Add a route to the destination 0.0.0.0/0 with the transit gateway as the target.

D.

Deploy an internet gateway, associate an EIP with the Customer VPC private subnet, and then add a new route with destination 0.0.0.0/0 with the internet gateway as the target.

E.

Deploy an internet gateway, attach it to the Customer VPC, and then associate an EIP with the port1 of the FortiGate in the Customer VPC.

Buy Now
Questions 6

Refer to the exhibit.

NSE7_CDS_AR-7.6 Question 6

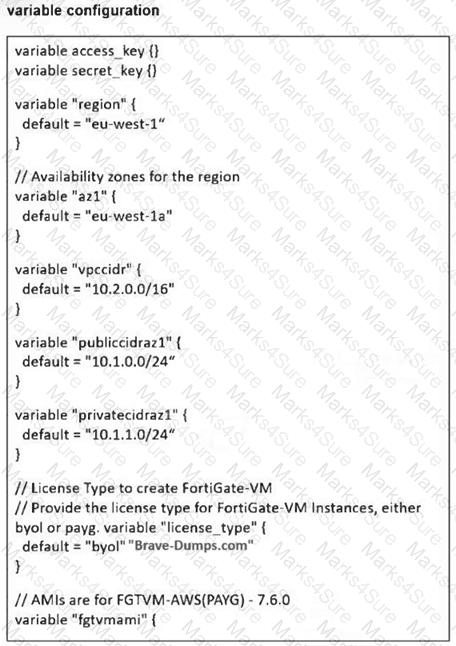
You are tasked to deploy a FortiGate VM with private and public subnets in Amazon Web Services (AWS). You examined the variables.tf file. Assume that all the other terraform files are in place. What will be the final result after running the terraform init and terraform apply commands? (Choose one answer)

Options:

A.

Terraform will not deploy a FortiGate VM.

B.

Terraform will deploy a FortiGate VM in the eu-West-1a availability zone without any subnets.

C.

Terraform will deploy a FortiGate VM in the eu-West-1 region with private and public subnets.

D.

Terraform will deploy a FortiGate VM in the eu-West-1a availability zone with two subnets and BYOL license.

Buy Now
Questions 7

Refer to the exhibit.

NSE7_CDS_AR-7.6 Question 7

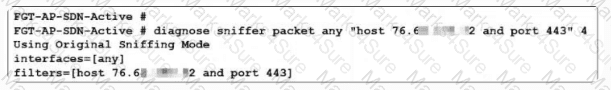
An administrator has deployed a FortiGate VM in Amazon Web Services (AWS) and is trying to access it using its public IP address from their local computer. However, the connection is not successful, and at the same time FortiGate is not receiving any HTTPS or SSH traffic on its external interface.

What should the administrator check for a possible issue?

Options:

A.

Check the FortiGate instance ID.

B.

Check the FortiGate firewall policies.

C.

Check the debug flow for any network ACLs.

D.

Check the inbound rules of the security groups.

Buy Now
Questions 8

What is the main advantage of using SD-WAN Transit Gateway Connect over traditional SD-WAN?

Options:

A.

You can use BGP over IPsec for maximum throughput.

B.

You can combine it with IPsec to achieve higher bandwidth.

C.

It eliminates the use of ECMP.

D.

You can use GRE-based tunnel attachments.

Buy Now
Questions 9

Refer to the exhibit.

NSE7_CDS_AR-7.6 Question 9

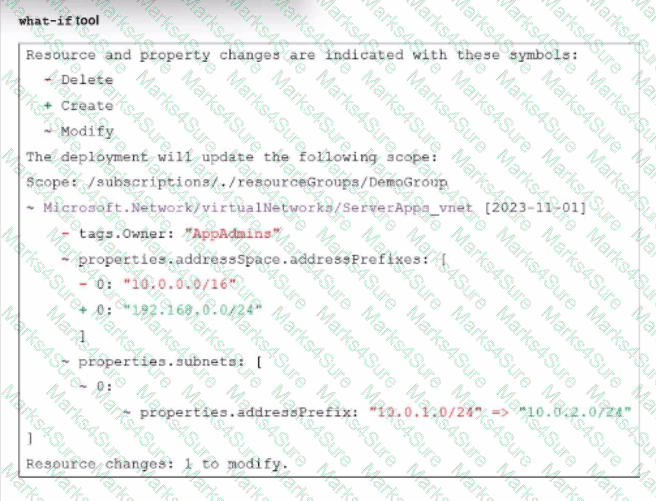
An administrator used the what-if tool to preview changes to an Azure Bicep file.

What will happen if the administrator decides to apply these changes in Azure?

Options:

A.

Subnet 10.0.1.0/24 will replace subnet 10.0.2.0/24.

B.

This deployment will fail and no changes will be applied.

C.

A new subnet will be added to ServerApps.

D.

The ServerApps VNet will be renamed.

Buy Now
Questions 10

Refer to the exhibit.

NSE7_CDS_AR-7.6 Question 10

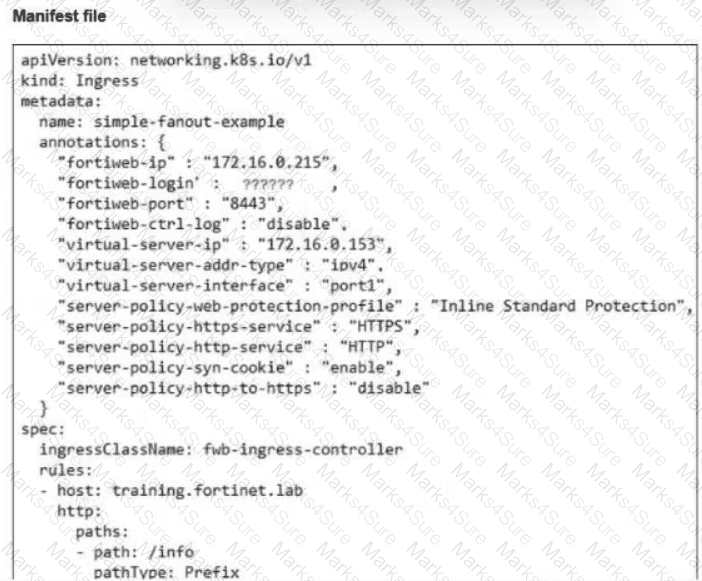
A team of AWS administrators is in the process of installing a FortiWeb ingress controller to protect containerized web applications in an Amazon Elastic Kubernetes Service (EKS) cluster. While customizing the manifest file shown in the exhibit, they realize that they do not know the correct value to enter in the fortiweb-login field.

How can they determine the correct value for this field?

Options:

A.

The correct value is the password of the FortiWeb admin account.

B.

They can find the expected value in the manifest file used to deploy the pods.

C.

They must create a Kubernetes secret with the kubectl command.

D.

They can refer to the output of the EKS cluster deployment.

Buy Now
Questions 11

You need a solution to safeguard public cloud-hosted web applications from the OWASP Top 10 vulnerabilities. The solution must support the same region in which your applications reside, with minimum traffic cost.

Which solution meets the requirements?

Options:

A.

Use FortiGate

B.

Use FortiCNP

C.

Use FortiWeb

D.

Use FortiADC

Buy Now
Questions 12

You have deployed a FortiGate HA cluster in Azure using a gateway load balancer for traffic inspection. However, traffic is not being routed correctly through the firewalls.

What can be the cause of the issue?

Options:

A.

The FortiNet VMs have IP forwarding disabled, which is required for traffic inspection.

B.

The health probes for the gateway load balancer are failing, which causes traffic to bypass the HA cluster.

C.

The gateway load balancer is not associated with the correct network security group (NSG) rules, which allow traffic to pass through.

D.

The protected VMs are in a different Azure subscription, which prevents the gateway load balancer from forwarding traffic.

Buy Now
Questions 13

Refer to the exhibit.

NSE7_CDS_AR-7.6 Question 13

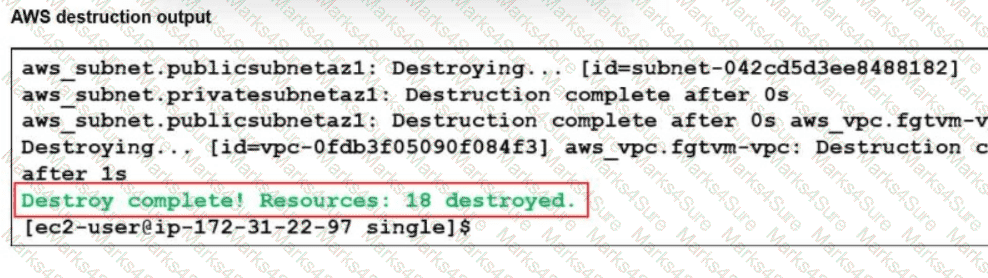
An administrator deployed a FortiGate-VM in a high availability (HA) (active/passive) architecture in Amazon Web Services (AWS) using Terraform for testing purposes. At the same time, the administrator deployed a single Linux server using AWS Marketplace.

Which two options are available for the administrator to delete all the resources created in this test? (Choose two.)

Options:

A.

The administrator must manually delete the Linux server.

B.

Use the terraform destroy all command.

C.

Use the terraform destroy command.

D.

Use the terraform validate command.

Buy Now
Questions 14

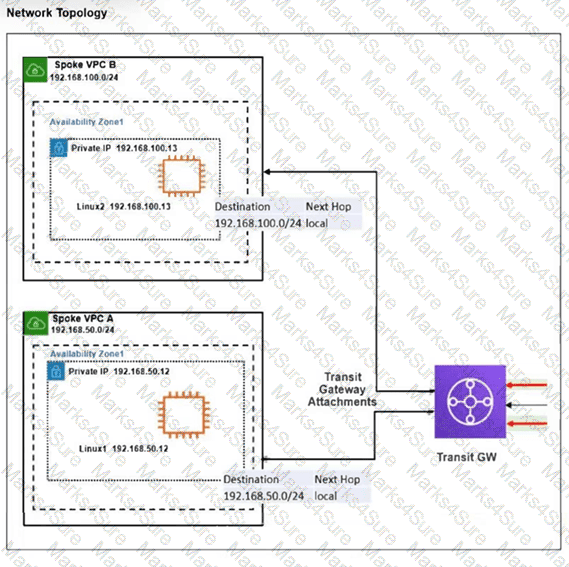
Refer to the exhibit.

NSE7_CDS_AR-7.6 Question 14

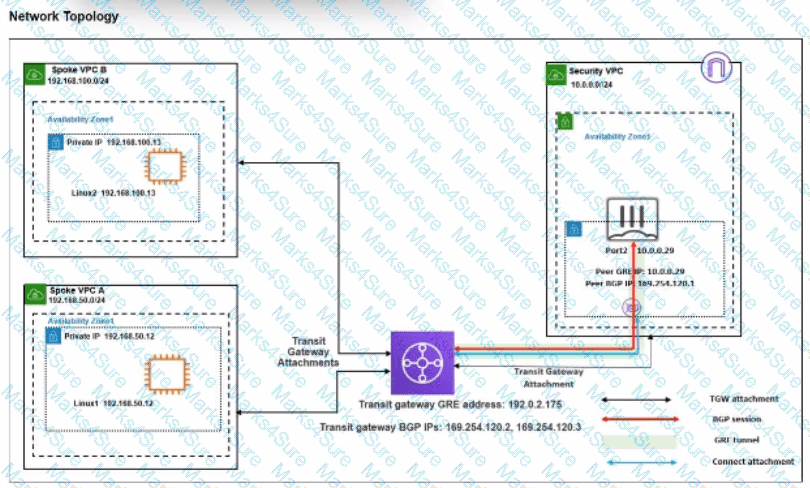
You attempted to access the Linux1 EC2 instance directly from the internet using its public IP address in AWS. However, your connection is not successful.

Given the network topology, what can be the issue?

Options:

A.

There is no connection between VPC A and VPC B.

B.

There is no internet gateway attached to the Spoke VPC A.

C.

The Transit Gateway BGP IP address is incorrect.

D.

There is no elastic IP address attached to FortiGate in the Security VPC.

Buy Now
Questions 15

Refer to the exhibit.

NSE7_CDS_AR-7.6 Question 15

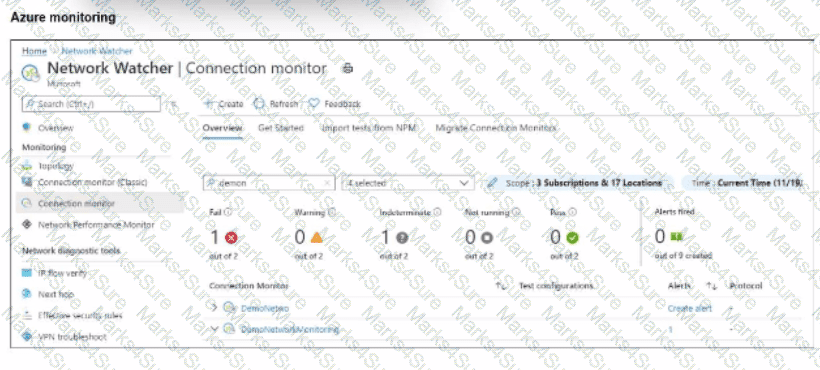
After analyzing the native monitoring tools available in Azure, an administrator decides to use the tool displayed in the exhibit.

Why would an administrator choose this tool?

Options:

A.

To view details about Azure resources and their relationships across multiple regions.

B.

To obtain, and later examine, traffic flow data with a visualization tool.

C.

To help debug issues affecting virtual network gateways.

D.

To compare the latency of an on-premises site with the latency of an Azure application.

Buy Now
Questions 16

An AWS administrator must ensure that each member of the cloud deployment team has the correct permissions to deploy and manage resources using CloudFormation. The administrator is researching which tasks must be executed with CloudFormation and therefore require CloudFormation permissions.

Which task is run using CloudFormation?

Options:

A.

Deploying a new pod with a service in an Elastic Kubernetes Service (EKS) cluster using the kubectl command

B.

Installing a Helm chart to deploy a FortiWeb ingress controller in an EKS cluster

C.

Creating an EKS cluster with the eksctl create cluster command

D.

Changing the number of nodes in a EKS cluster from AWS CloudShell

Buy Now
Questions 17

Refer to the exhibit.

NSE7_CDS_AR-7.6 Question 17

The exhibit shows a customer deployment of two Linux instances and their main routing table in Amazon Web Services (AWS). The customer also created a Transit Gateway (TGW) and two attachments. Which two steps are required to route traffic from Linux instances to the TGW? (Choose two answers)

Options:

A.

In the main subnet routing table in VPC A and B, add a new route with destination 0.0.0.0/0, next hop TGW.12

B.

In the TGW route table, associate two attachments.34

C.

In the TGW route table, add route propagation to 192.168.0.0/16.56

D.

In the main subnet routing table in VPC A and B, add a new route with7 destination 0.0.0.0/0, next hop Internet 8gateway (IGW).

Buy Now
Questions 18

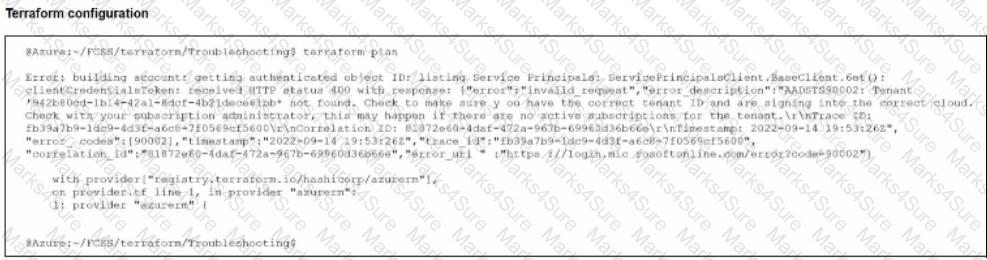
Refer to the exhibit.

NSE7_CDS_AR-7.6 Question 18

After the initial Terraform configuration in Microsoft Azure, the terraform plan command is run.

Which two statements about running the terraform plan command are true? (Choose two.)

Options:

A.

The terraform plan command will deploy the rest of the resources except the service principle details.

B.

You cannot run the terraform apply command before the terraform plan command.

C.

The terraform plan command makes terraform do a dry run.

D.

You must run the terraform init command once, before the terraform plan command.

Buy Now
Questions 19

In an SD-WAN TGW Connect topology, which three initial steps are mandatory when routing traffic from a spoke VPC to a security VPC through a Transit Gateway? (Choose three.)

Options:

A.

From the security VPC TGW subnet routing table, point 0.0.0.0/0 traffic to the FortiGate internal port.

B.

From the security VPC TGW subnet routing table, point 0.0.0.0/0 traffic to the TGW.

C.

From both spoke VPCs, and the security VPC, point 0.0.0.0/0 traffic to the Internet Gateway.

D.

From the security VPC FortiGate internal subnet routing table, point 0.0.0.0/0 traffic to the TGW.

E.

From the spoke VPC internal routing table, point 0.0.0.0/0 traffic to the TGW.

Buy Now
Questions 20

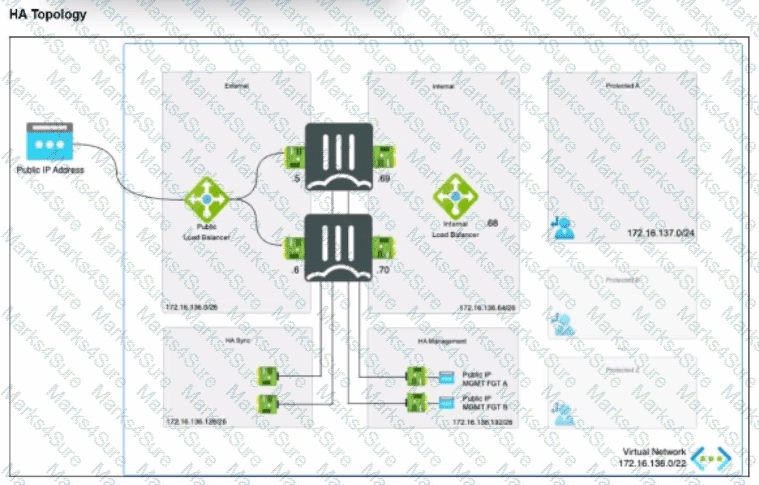
Refer to the exhibit.

NSE7_CDS_AR-7.6 Question 20

The exhibit shows an active-passive high availability FortiGate pair with external and internal Azure load balancers There is no SDN connector used in this solution.

Which configuration must the administrator implement on each FortiGate?

Options:

A.

Single BGP route to Azure probe IP address.

B.

One static route to Azure Lambda IP address.

C.

Two static routes to Azure probe IP address.

D.

Two BGP routes lo Azure probe IP address.

Buy Now
Exam Code: NSE7_CDS_AR-7.6
Exam Name: Fortinet NSE 7 - Public Cloud Security 7.6.4 Architect
Last Update: Sep 29, 2026
Questions: 67

PDF + Testing Engine

$64.99   $185.69

Testing Engine

$49.99   $142.83

PDF (Q&A)

$54.99   $157.11