Free Practice Questions for the Fortinet Certified Professional Security Operations NSE7_SOC_AR-7.6 Exam (2026 Updated)
At Marks4sure, we are dedicated to providing IT professionals with the most accurate and reliable preparation materials for the Fortinet NSE7_SOC_AR-7.6 exam. To support your certification journey, we have made a selection of our premium 2026 Fortinet Certified Professional Security Operations practice questions and answers available completely free. You can take this practice test as many times as you need. Every question includes a detailed, expertly verified explanation to ensure you fully grasp the core security concepts before test day.
Exhibit:
Which observation about this FortiAnalyzer Fabric deployment architecture is true?
Review the incident report. Shortly after being compromised, an infected host collected its own network configuration and connection details, then began sending low-volume connection attempts to multiple internal addresses to identify responding hosts. Which two MITRE ATT & CK techniques best describe this activity? Choose two answers.
When configuring an Ingest Bulk Feed playbook step, which two restrictions must you consider? Choose two answers.
Refer to Exhibits:
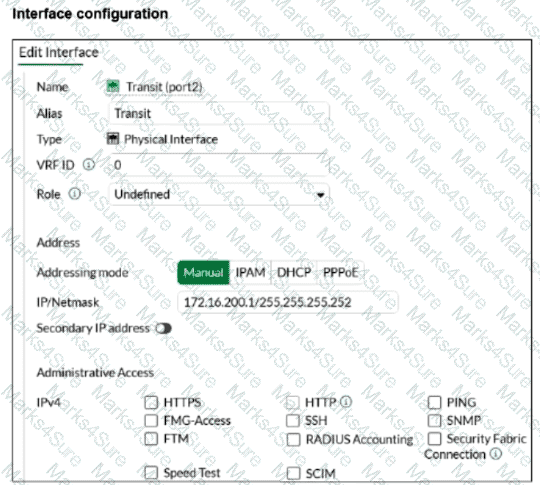
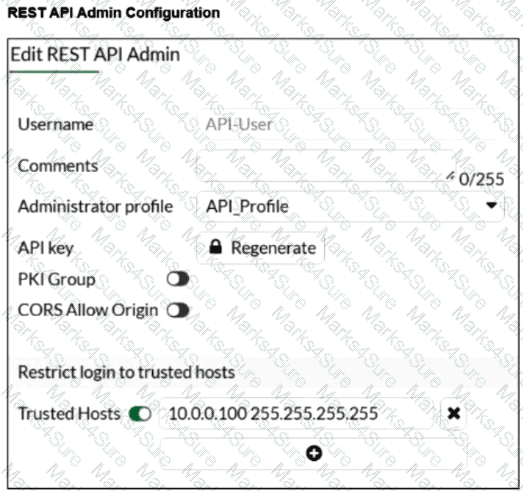
You configured the FortiGate connector on FortiSOAR. You want to allow FortiSOAR 10.200.200.160 to perform actions on FortiGate 172.16.200.1. However, the connection attempt fails. Assume that the FortiGate connector is configured correctly on the FortiSOAR side.
Which two configurations are required on FortiGate? Choose two answers.
A very long FortiSOAR playbook failed at step 30 because of an intermittent networking issue, which has now been resolved. You want to finish executing the playbook without repeating earlier steps or losing prior context. Which action should you take? Choose one answer.
Refer to the exhibit.
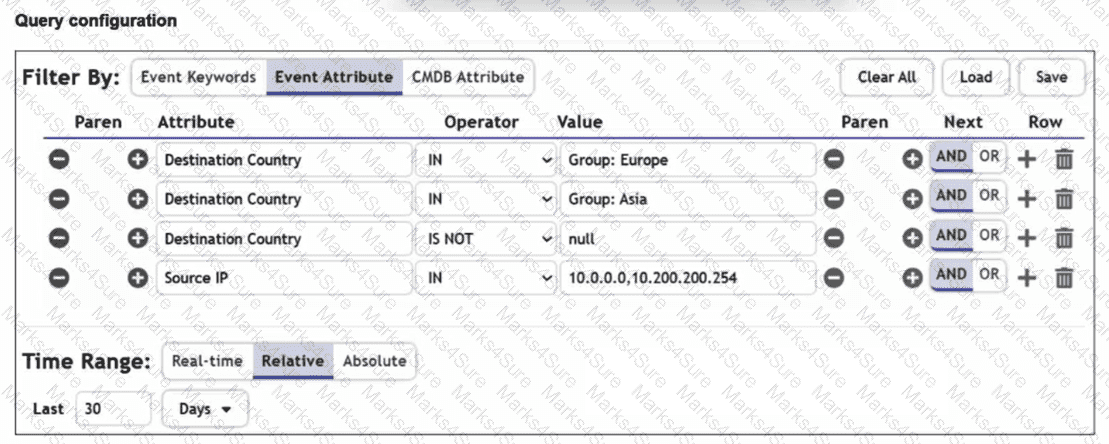
You are trying to find traffic flows to destinations that are in Europe or Asia, for hosts in the local LAN segment. However, the query returns no results. Assume these logs exist on FortiSIEM.
Which three mistakes can you see in the query shown in the exhibit? (Choose three answers)
Refer to the exhibits.
The FortiMail Sender Blocklist playbook is configured to take manual input and add those entries to the FortiMail abc. com domain-level block list. The playbook is configured to use a FortiMail connector and the ADD_SENDER_TO_BLOCKLIST action.
Why is the FortiMail Sender Blocklist playbook execution failing7
You are trying to create a playbook that uses source data from ingestion to populate the description field of a task. You successfully saved the source data to a variable called ingestion_data. Now, you must parse the results and extract a list of indicators. Which Jinja expression can accomplish this task? Choose one answer.
You are designing a FortiSOAR hybrid multi-tenant deployment. The architecture must support remote tenant execution and automation inside segmented networks. Which three elements are true for this design? Choose three answers.
Refer to the exhibits.
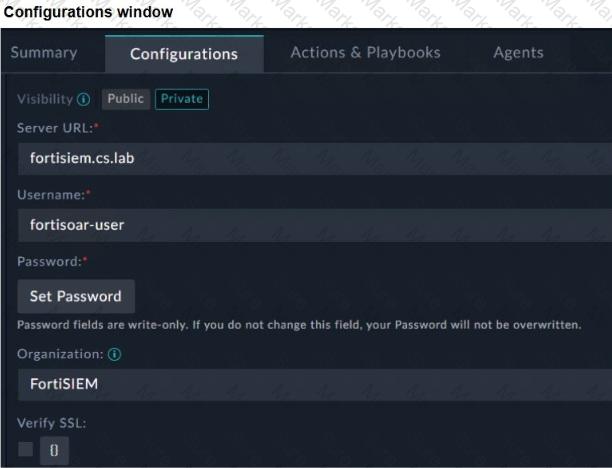
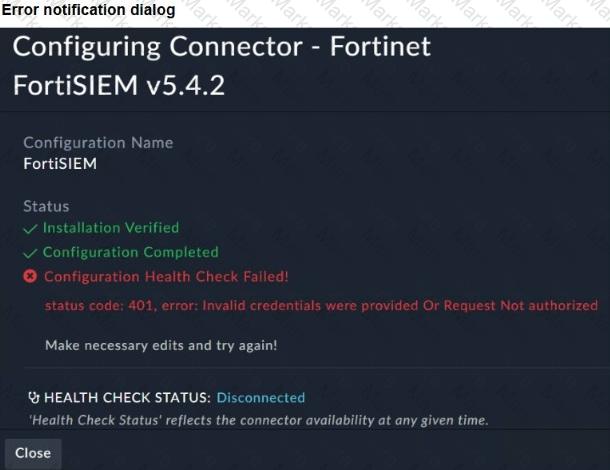
You configured the FortiSIEM connector on FortiSOAR. However, when you try to save the configuration, you see the error shown in the exhibit. What are two possible causes? Choose two answers.
Which three end user logs does FortiAnalyzer use to identify possible IOC compromised hosts? (Choose three.)
Refer to the exhibits.
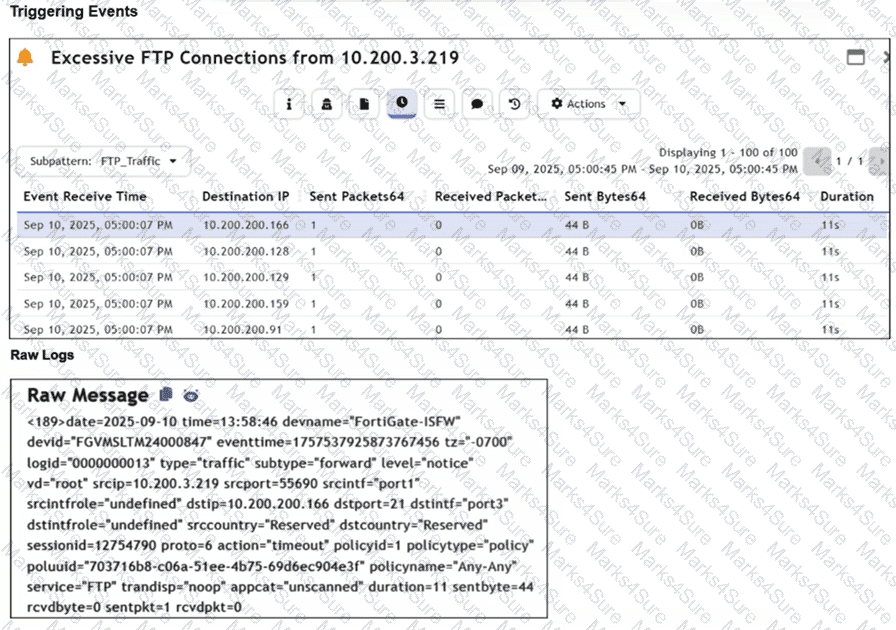
Assume that the traffic flows are identical, except for the destination IP address. There is only one FortiGate in network address translation (NAT) mode in this environment.
Based on the exhibits, which two conclusions can you make about this FortiSIEM incident? (Choose two answers)
Review the incident report:
Packet captures show a host maintaining periodic TLS sessions that imitate normal HTTPS traffic but run on TCP 8443 to a single external host. An analyst flags the traffic as potential command-and-control. During the same period, the host issues frequent DNS queries with oversized TXT payloads to an attacker-controlled domain, transferring staged files.
Which two MITRE ATT & CK techniques best describe this activity? (Choose two answers)
Refer to the exhibits.
What can you conclude from analyzing the data using the threat hunting module?
You want to use the queue and shift management feature to automatically assign newly created low-priority tasks to members of the L1 queue. However, you are unable to add the Tasks module to the Module Types list. What is the problem? Choose one answer.
Refer to the exhibit,
which shows the partial output of the MITRE ATT & CK Enterprise matrix on FortiAnalyzer.
Which two statements are true? (Choose two.)
Refer to Exhibit:
You are tasked with reviewing a new FortiAnalyzer deployment in a network with multiple registered logging devices. There is only one FortiAnalyzer in the topology.
Which potential problem do you observe?
An analyst prioritizes blocking IP addresses and domains from every phishing campaign. Based on the Pyramid of Pain model, which two statements accurately describe this approach? Choose two answers.
Refer to the exhibit.
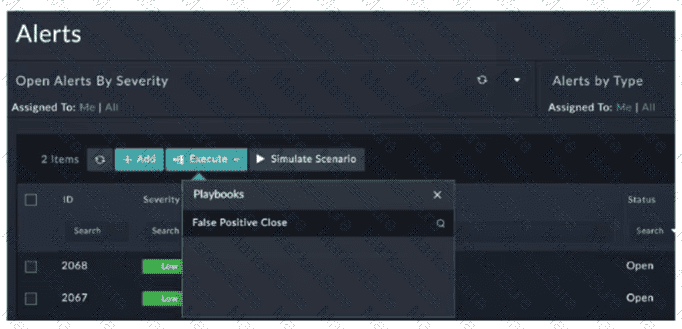
You configured a playbook named False Positive Close, and want to run it to verify if it works. However, when you click Execute and search for the playbook, you do not see it listed. Which two reasons could be the cause of the problem? (Choose two answers)
While monitoring your network, you discover that one FortiGate device is sending significantly more logs to FortiAnalyzer than all of the other FortiGate devices in the topology.
Additionally, the ADOM that the FortiGate devices are registered to consistently exceeds its quota.
What are two possible solutions? (Choose two.)
Refer to the exhibit.
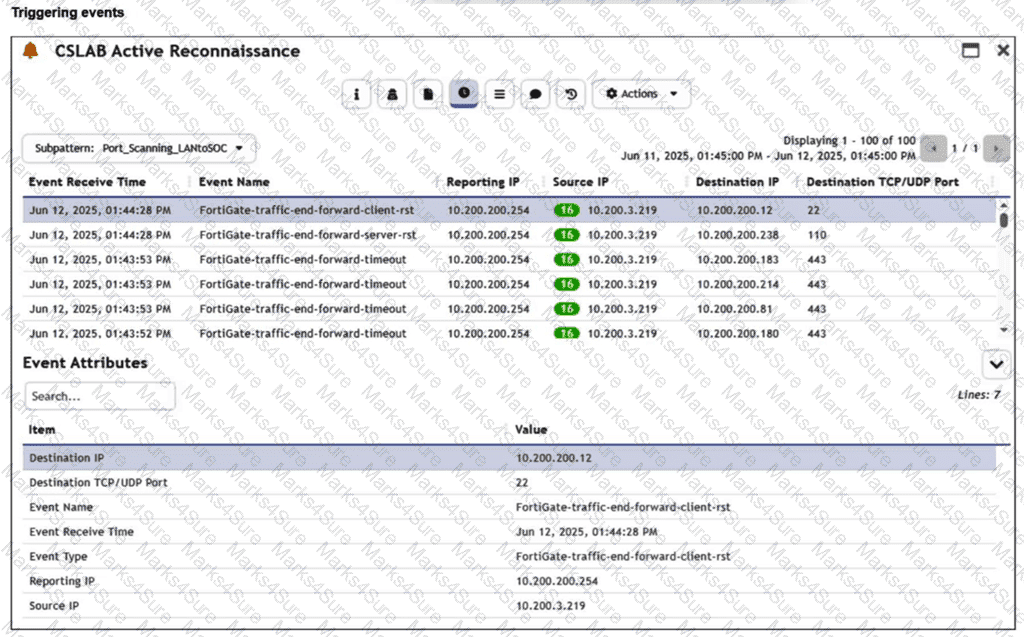
You are reviewing the Triggering Events page for a FortiSIEM incident. You want to remove the Reporting IP column because you have only one firewall in the topology. How do you accomplish this? (Choose one answer)
Which two statements about the FortiAnalyzer Fabric topology are true? (Choose two.)
Refer to the exhibits.
The DOS attack playbook is configured to create an incident when an event handler generates a denial-of-ser/ice (DoS) attack event.
Why did the DOS attack playbook fail to execute?
PDF + Testing Engine
Testing Engine
PDF (Q&A)