Halloween Sale Limited Time 70% Discount Offer Use coupon code below to save on all exam bundles!
Code: Hall70
Ends in: 0d 00h 00m 00s

Free Practice Questions for the Fortinet NSE 7 Network Security Architect NSE7_SSE_AR-26 Exam (2026 Updated)

At Marks4sure, we are dedicated to providing IT professionals with the most accurate and reliable preparation materials for the Fortinet NSE7_SSE_AR-26 exam. To support your certification journey, we have made a selection of our premium 2026 NSE 7 Network Security Architect practice questions and answers available completely free. You can take this practice test as many times as you need. Every question includes a detailed, expertly verified explanation to ensure you fully grasp the core security concepts before test day.

Questions 4

Which statement describes FortiGate behavior when you reference a zone in a static route?

Options:

A.

FoftiGate installs ECMP static routes for the first two members of the zone.

B.

FortiGate ignores the static routes defined through members referenced in the zone.

C.

FortiGate routes the traffic through the best performing member of the zone.

D.

FortiGate installs a static route for each member in the zone.

Buy Now
Questions 5

Which three traffic flows are supported by FortiSASE Secure Private Access (SPA)? (Choose three.)

Options:

A.

From private resources to the internet.

B.

From private resources to FortiSASE agent-based users.

C.

From private resources to other private resources (SPA to SPA).

D.

From agent-based users to private resources behind the Fortinet SD-WAN.

E.

From thin branches/branch on-ramp to private resources behind the Fortinet SD-WAN.

Buy Now
Questions 6

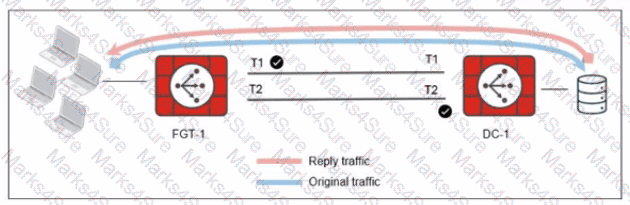
Refer to the exhibit. The administrator analyzed the traffic between a branch FortiGate and the server located in the data center, and noticed the behavior shown in the diagram. When the LAN clients located behind FGT1 establish a session to a server behind DC-1, the administrator observes that, on DC-1, the reply traffic is routed overT2. even though T1 is the preferred member in the matching SD-WAN rule. What can the administrator do to instruct DC-1 to route the reply traffic through the member with the best performance?
NSE7_SSE_AR-26 Question 6

Exhibit 1

Options:

A.

Enable snat-route-change under config system global.

B.

Enable reply-session under config system sdwan.

C.

Enable auxiliary-session under config system settings.

D.

FortiGate route lookup for reply traffic only considers routes over the original ingress interface.

Buy Now
Questions 7

Refer to the exhibit.

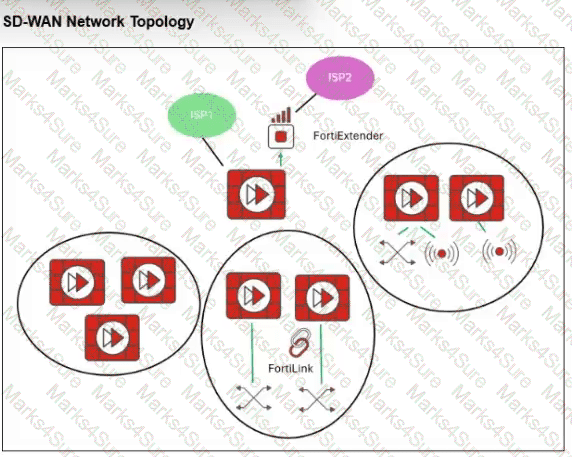
You want to configure SD-WAN on a network, as shown in the exhibit.

The network contains many FortiGate devices. Some are used as next-generation firewalls (NGFW), and some are installed with extensions such as FortiSwitch, FortiAP, or FortiExtender.

Which factors should you consider when planning your deployment?
NSE7_SSE_AR-26 Question 7

Exhibit — SD-WAN network topology

Options:

A.

You should exclude the FortiGate devices with two types of extensions from the SD-WAN topology.

B.

You should build multiple SD-WAN topologies. Each topology should contain only one type of extension.

C.

You can build an SD-WAN topology that includes all devices. The hubs can be FortiGate devices with FortiExtender.

D.

You can build an SD-WAN topology that includes all devices. You must define multiple regions and group devices by extension type.

Buy Now
Questions 8

You plan a large SD-WAN deployment for a global company. You want to divide the network architecture into five geographical regions and install two hubs in each region for increased redundancy. You expect a significant amount of traffic within each region and limited traffic flow between spokes in different regions. You plan to connect the small branch sites to only the closest hub in their regions and the large branch sites to the two hubs in the regions. Which statement about your plan is true? Choose one answer.

Options:

A.

It is possible. You should use eBGP as the routing protocol between the regions.

B.

It is not possible. FortiOS 7.6 supports multihub topologies with up to four hubs.

C.

It is possible. You should use FortiManager and the overlay orchestrator multihub topology to simplify the deployment.

D.

It is not possible. In a region, all spokes must have either single-hub or dual-hub connectivity.

Buy Now
Questions 9

In a FortiSASE proxy-based deployment, which two features protect against web-based threats? (Choose two.)

Options:

A.

Web application firewall (WAF) for web applications

B.

Intrusion prevention system (IPS) for web traffic

C.

SSL deep inspection for encrypted web traffic

D.

Malware protection with sandboxing capabilities

Buy Now
Questions 10

Refer to the exhibit.

NSE7_SSE_AR-26 Question 10

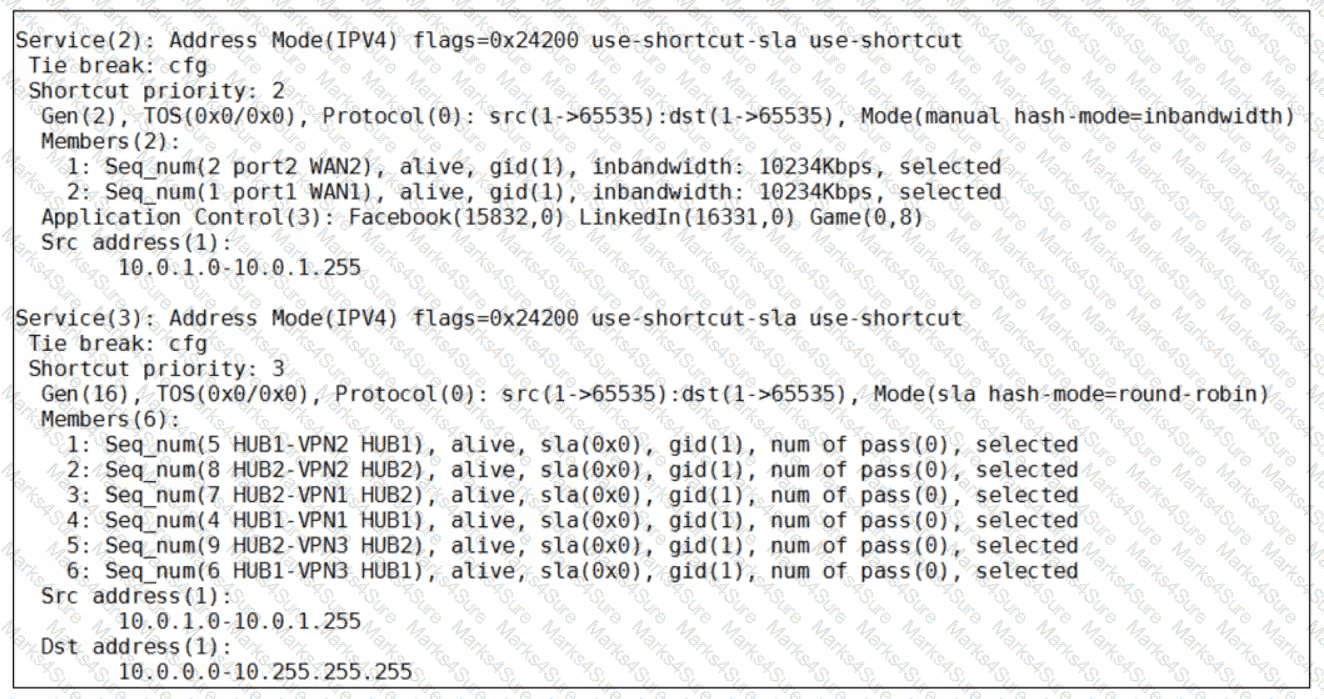
The administrator configured two SD-WAN rules to load balance traffic.

Which interfaces does FortiGate use to steer the SMTP traffic from 10.0.1.124 to 10.0.0.254?

Options:

A.

Any interface in the WAN1 or WAN2 zones.

B.

FortiGate routes the traffic according to the FIB.

C.

HUB1-VPN2

D.

Any interface in the HUB1 or HUB2 zones.

Buy Now
Questions 11

When you use the command diagnose sys session list, how do you identify the sessions that correspond to traffic steered according to SD-WAN rules?

Options:

A.

You identify sessions steered according to SD-WAN rules with the flag vwl.

B.

You cannot identify SD-WAN sessions. You must use the sdwar. session filter.

C.

You identify sessions steered according to SD-WAN rules with the data vwl_mbr_seq.

D.

You identify sessions steered according to SD-WAN rules with the data 3dwan_service_id.

Buy Now
Questions 12

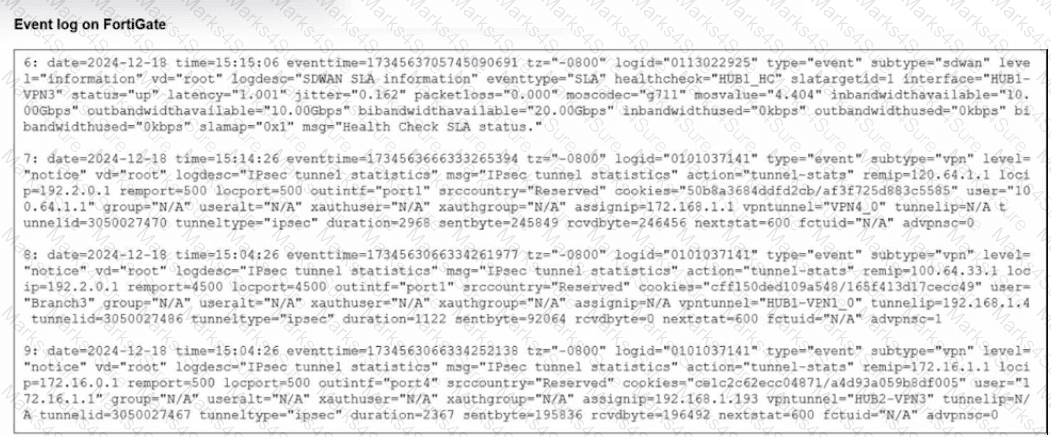
Refer to the exhibit that shows event logs on FortiGate. Based on the output shown in the exhibit, what can you say about the tunnels on this device?
NSE7_SSE_AR-26 Question 12

Exhibit 1

Options:

A.

The master tunnel HUB2-VPN3 cannot accept ADVPN shortcuts.

B.

The device steers voice traffic through the VPN tunnel HUB1-VPN3.

C.

The VPN tunnel HUB1-VPN1_0 is a shortcut tunnel.

D.

There is one shortcut tunnel built from master tunnel VPN4.

Buy Now
Questions 13

Refer to the exhibit.

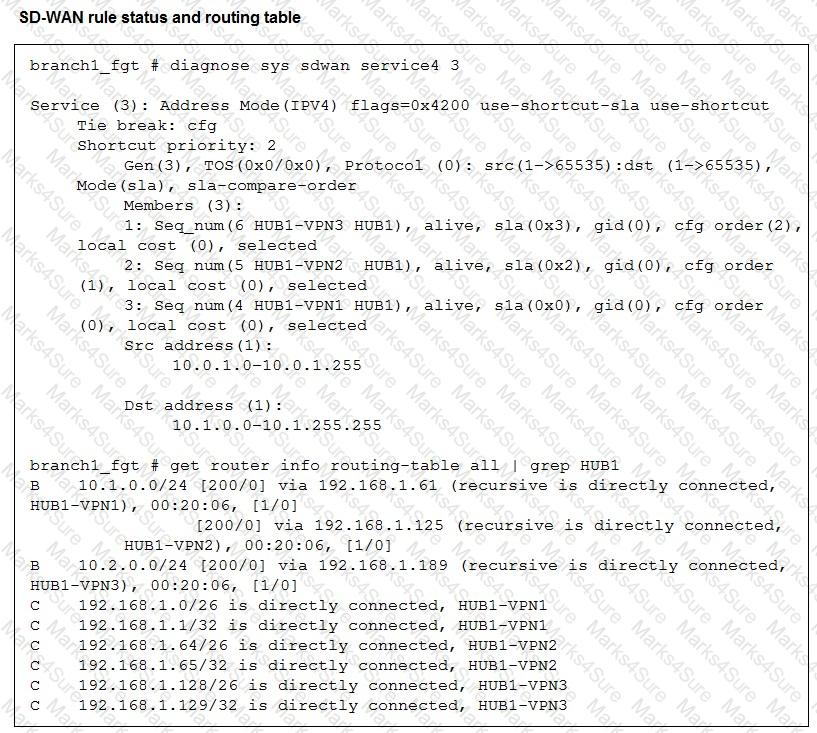
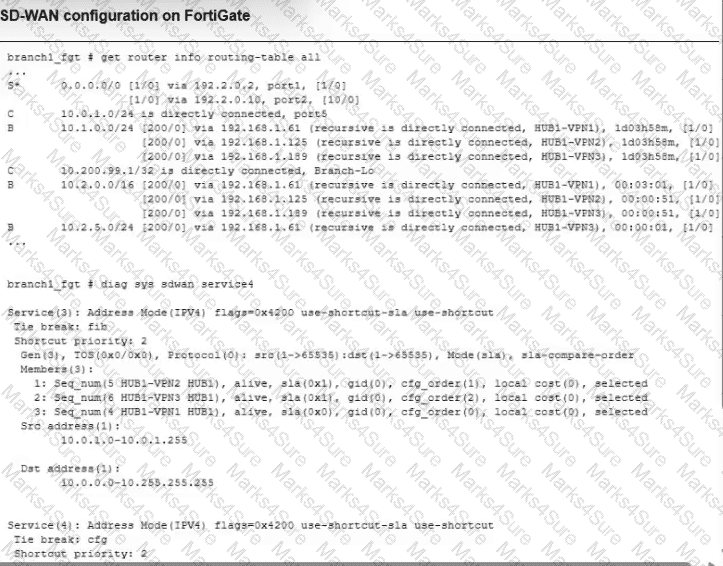
Which SD-WAN rule and interface uses FortiGate to steer the traffic from the LAN subnet 10.0.1.0/24 to the corporate server 10.2.5.254?
NSE7_SSE_AR-26 Question 13

Exhibit — SD-WAN rule and routing outputs

Options:

A.

SD-WAN service rule 3 and interface HUB1-VPN3.

B.

SD-WAN service rule 3 and interface HUB1-VPN2.

C.

SD-WAN service rule 4 and interface port2.

D.

SD-WAN service rule 4 and port1 or port2.

Buy Now
Questions 14

An administrator is attempting to create two static routes: one for the SD-WAN zone wan-link and one pointing to a specific SD-WAN member interface that currently belongs to the wan-link zone.

Which configuration is required to make this scenario valid? (Choose one answer.)

Options:

A.

The destination subnets of the two static routes must be different.

B.

Both routes must have the same administrative distance to allow equal-cost multipath (ECMP).

C.

The destination subnet configured on the SD-WAN zone cannot be a default route.

D.

SD-WAN member must be an IPsec interface.

Buy Now
Questions 15

The SD-WAN overlay template helps to prepare SD-WAN deployments. To complete the tasks performed by the SD-WAN overlay template, the administrator must perform some post-run tasks. What are two mandatory post-run tasks that must be performed? (Choose two.)

Options:

A.

Configure routing through the overlay tunnels created by the SD-WAN overlay template.

B.

Create policy packages and assign them to the branch devices.

C.

Assign a hub id metadata variable to each hub device.

D.

Configure SD-WAN rules

E.

Assign an sdwan_id metadata variable to each device (branch and hub)

Buy Now
Questions 16

Which two features must you configure before FortiGate can steer traffic according to SD-WAN rules? Choose two answers.

Options:

A.

Security profiles

B.

Underlay links

C.

Overlay links

D.

Traffic shaping

E.

Firewall policies

Buy Now
Questions 17

In an enterprise deployment of FortiSASE, single sign-on (SSO) is used to streamline user authentication across security services.

Which statement correctly describes an SSO capability on FortiSASE?

Options:

A.

It requires users to authenticate separately for each security service for improved segmentation.

B.

It bypasses identity verification when users access trusted networks.

C.

It allows authentication to be delegated to an external identity provider such as Azure AD or SAML-based identity providers (IdPs).

D.

It stores user credentials locally on FortiSASE to reduce dependency on external systems.

Buy Now
Questions 18

In a deployment of FortiSASE, a network architect is designing branch connectivity using the branch on-ramp feature to simplify secure access to cloud and Software-as-a-Service (SaaS) resources without requiring a full, traditional WAN infrastructure at each site.

What is the primary purpose of the FortiSASE branch on-ramp feature?

Options:

A.

To provide direct internet breakout from branch FortiGate only

B.

To extend secure connectivity from branches without full WAN infrastructure

C.

To replace all endpoint security agents with cloud-based inspection only

D.

To perform application performance optimization for SaaS traffic at the branch level

Buy Now
Questions 19

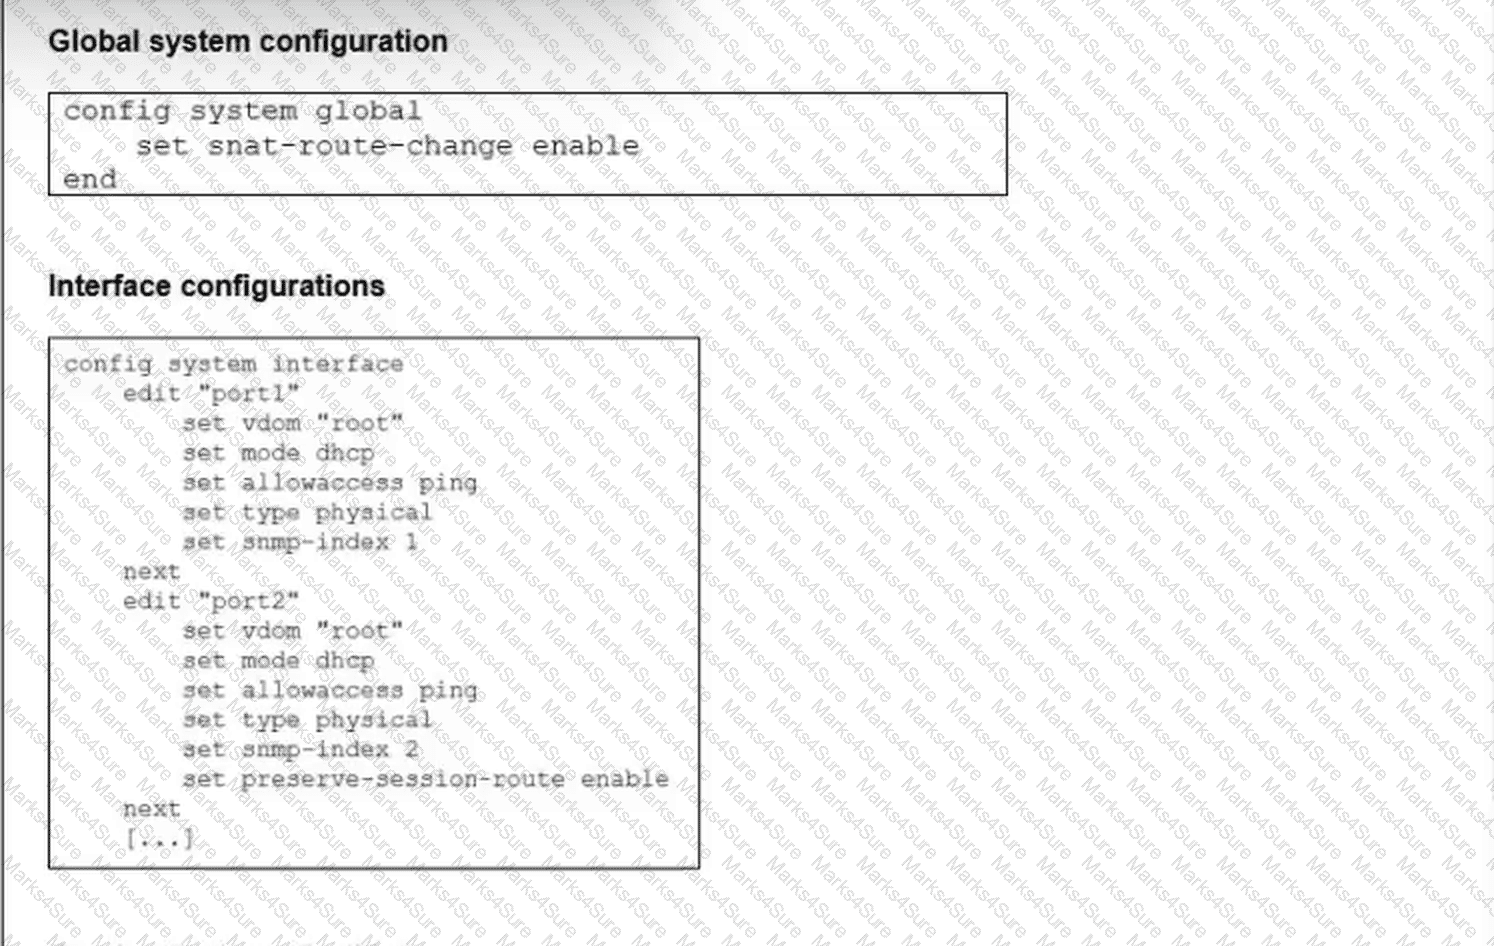
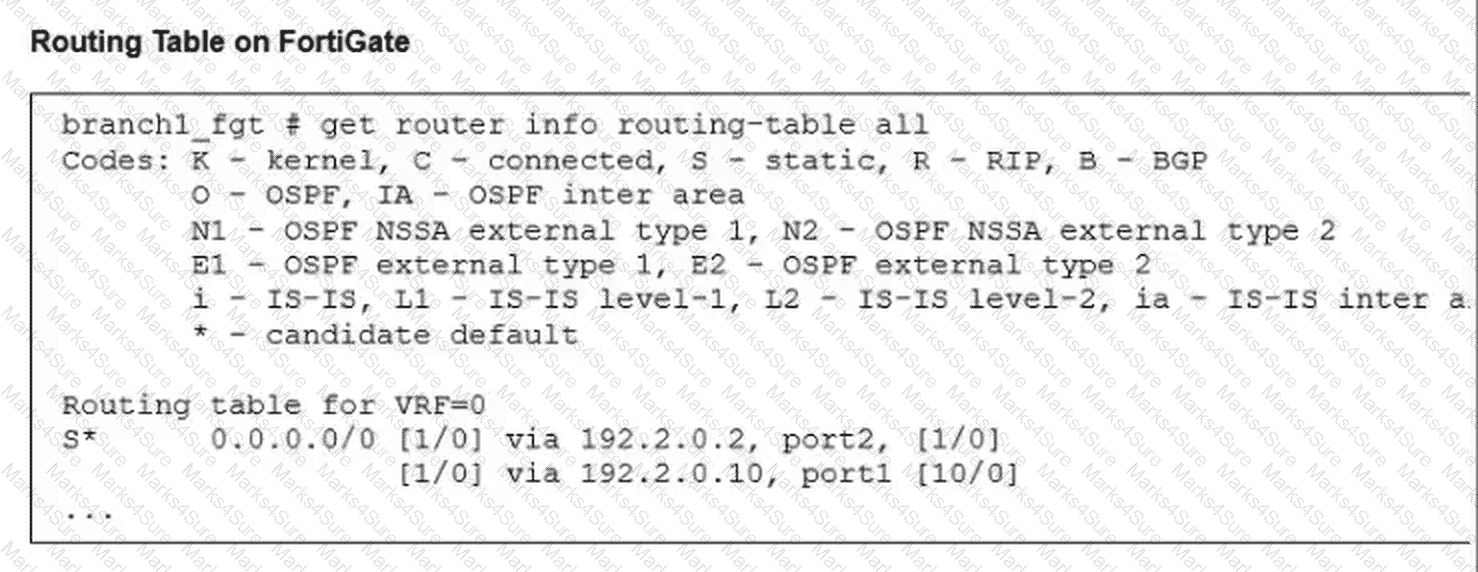
Refer to the exhibits.

The administrator increases the member priority on port2 to 20.

Assuming the route egressing port2 is still valid, upon configuration changes and the receipt of new packets.

Which two actions does FortiGate perform on existing sessions established over port2? (Choose two.)
NSE7_SSE_AR-26 Question 19

Exhibit 1 — Global system and interface configuration
NSE7_SSE_AR-26 Question 19

Exhibit 2 — FortiGate routing table

Options:

A.

FortiGate updates the gateway information of the sessions with SNAT so that they use port1 instead of port2.

B.

FortiGate flags all source network address translation (SNAT) sessions as dirty only if the administrator has assigned an IP pool to the firewall policies with NAT.

C.

FortiGate routes new sessions over port1.

D.

FortiGate flags all sessions as dirty.

E.

FortiGate continues routing all existing sessions over port2.

Buy Now
Questions 20

Which two statements correctly describe what happens when traffic matches the implicit SD-WAN rule? (Choose two.)

Options:

A.

The session information output displays no SD-WAN service id.

B.

Traffic is load balanced using the algorithm set for the v4-ecmp-mode setting.

C.

The traffic is distributed, regardless of weight, through all available static routes.

D.

Traffic does not match any of the entries in the policy route table.

E.

FortiGate flags the session with may_dirty and vwl_def ault.

Buy Now
Questions 21

A customer wants to ensure secure access for private applications for their users by replacing their VPN.

Which two SASE technologies can you use to accomplish this task? (Choose two.)

Options:

A.

SD-WAN on-ramp

B.

zero trust network access (ZTNA)

C.

secure SD-WAN

D.

secure web gateway (SWG) and cloud access security broker (CASB)

Buy Now
Questions 22

In a newly deployed FortiSASE environment using default configuration settings, an administrator provisions endpoint connectivity through FortiClient. As part of the onboarding process, specific configuration elements are automatically synchronized from FortiSASE to connected endpoints without manual intervention.

Which two settings are automatically pushed from FortiSASE to FortiClient, in this default deployment scenario? (Choose two.)

Options:

A.

FortiSASE certificate authority (CA) certificate

B.

Tunnel profile configuration for secure connectivity

C.

FortiSandbox settings

D.

Security posture tag definitions

Buy Now
Questions 23

As an IT manager for a healthcare company, you want to delegate the installation and management of your SD-WAN deployment to a managed security service provider (MSSP). Each site must maintain direct internet access and ensure that it is secure. You expected significant traffic flow between the sites and want to delegate as much of the network administration and management as possible to the MSSP. Which two MSSP deployment blueprints best address the customer’s requirements? (Choose two.)

Options:

A.

Use a shared hub at the MSSP premises with a dedicated VDOM for the new customer, and install the spokes at the customer premises.

B.

Use a shared hub at the MSSP premises and a dedicated hub at the customer premises and install the spokes at the customer premises.

C.

Install a dedicated hub at the MSSP premises for the new customer, and install the spokes at the customer premises.

D.

Install the hub and spokes at the customer premises and enable the MSSP to manage the SD-WAN deployment using FortiManager with a dedicated ADOM.

Buy Now
Questions 24

Which two matching traffic criteria are available to steer traffic in SD-WAN rules?

Options:

A.

Physical interface type

B.

BGP attributes

C.

Application categories

D.

Internet Service Database (ISDB)

Buy Now
Questions 25

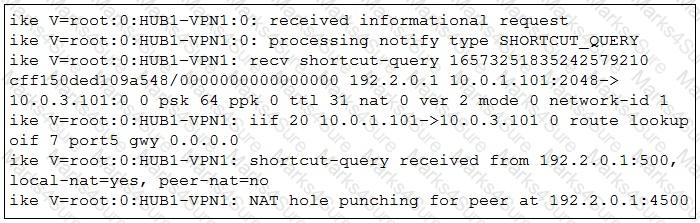
Refer to the exhibit. Which statement best describe the role of the ADVPN device in handling traffic?
NSE7_SSE_AR-26 Question 25

Exhibit 1

Options:

A.

This is a spoke that has received a direct shortcut query from a remote spoke.

B.

This is a hub, and two spokes, 192.2.0.1 and 10.0.3.101, establish a shortcut.

C.

This is a hub that has received a shortcut query from a spoke and has forwarded it to another spoke.

D.

This is a spoke that has received a shortcut query from a remote hub.

Buy Now
Questions 26

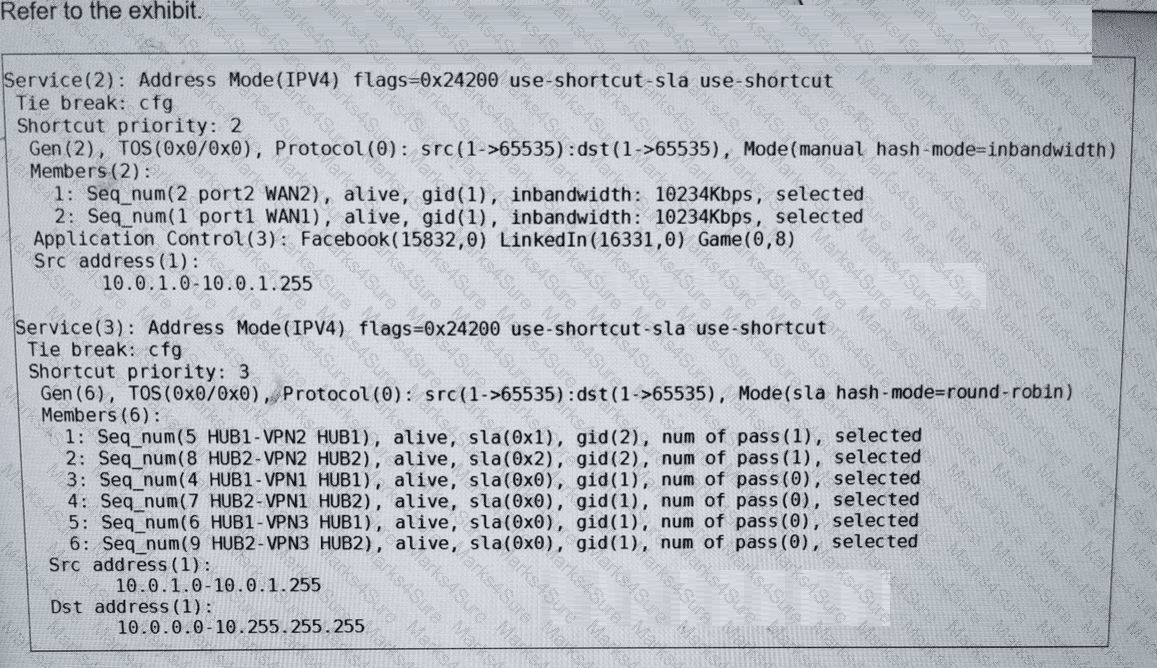
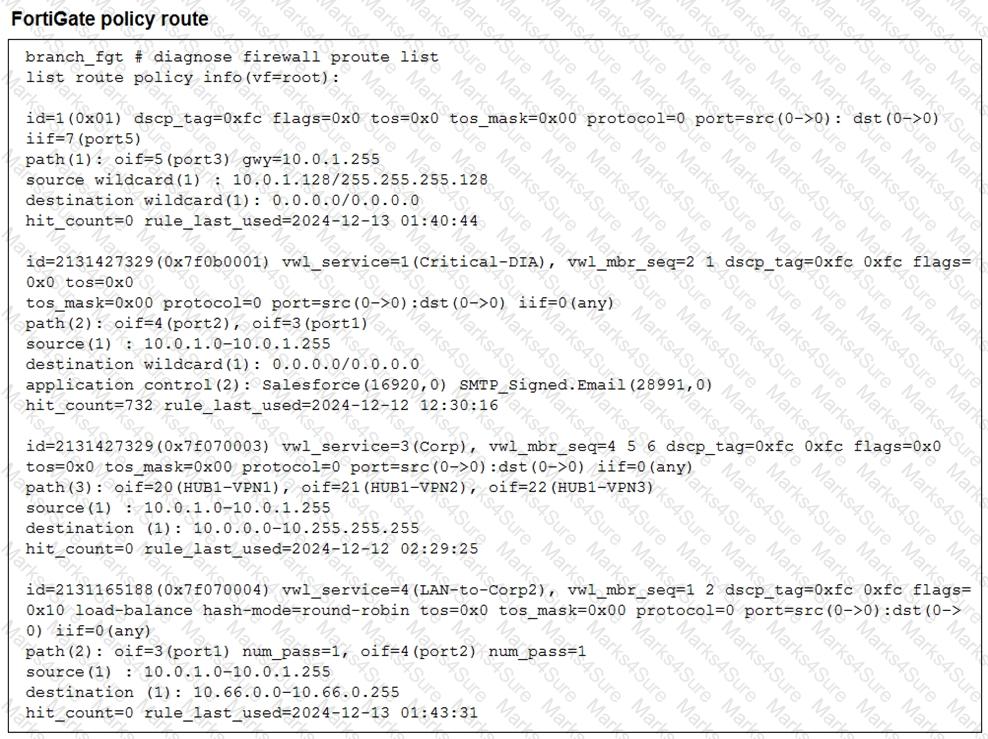
Refer to the exhibit. The administrator configured two SD-WAN rules to load balance the traffic. Which interfaces does FortiGate use to steer the traffic from 10.0.1.124 to 10.0.0.254? Choose one answer.
NSE7_SSE_AR-26 Question 26

Exhibit 1

Options:

A.

HUB2-VPN2

B.

HUB1-VPN2 or HUB2-VPN2

C.

port1 or port2

D.

Any interface in the HUB1 or HUB2 zones

Buy Now
Questions 27

As an MSSP administrator, you are asked to configure ADVPN on an existing SD-WAN topology. FortiManager manages the customer devices in a dedicated ADOM. The previous administrator used the SD-WAN overlay topology. Which two statements apply to this scenario? (Choose two.)

Options:

A.

You can activate auto-discovery VPN in the SD-WAN overlay template only if it is a single hub topology.

B.

When auto-discovery VPN is enabled, FortiManager updates the IPsec and BGP templates in the hub.

C.

After you enable auto-discovery VPN in the overlay template, you must select between ADVPN 2.0 and ADVPN 1.0.

D.

You can activate auto-discovery VPN in the SD-WAN overlay template for any type of topology, including a primary-primary dual-hub topology.

Buy Now
Questions 28

Refer to the exhibit. What conclusions can you draw about the traffic received by FortiGate originating from the source LAN device 10.0.1.133 and destined for the company’s SMTP mail server at 10.66.0.125?
NSE7_SSE_AR-26 Question 28

Exhibit 1

Options:

A.

FortiGate steers the traffic from the LAN device 10.0.1.133 to the company SMTP mail server 10.66 0.125 through port3.

B.

ForliGate steers the traffic from the LAN device 10.0.1.133 to the company SMTP mail server 10.66.0.125 through port2.

C.

FortiGate steers the traffic from the LAN device 10.0.1.133 to the company SMTP mail server 10.66.0.125 through the SD-WAN member ID 4.

D.

FortiGate steers the traffic from the LAN device 10.0.1.133 to the SMTP mail server 10.66.0.125 through the SD-WAN member ID 1 or 2.

Buy Now
Questions 29

Refer to the exhibit.

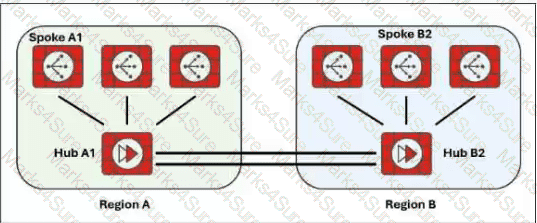
Two hub-and-spoke groups are connected through redundant site-to-site IPsec VPNs between Hub 1 and Hub 2.

Which two configuration settings are required for spoke A1 to establish an auto-discovery VPN (ADVPN) shortcut with spoke B2? (Choose two.)
NSE7_SSE_AR-26 Question 29

Exhibit — Hub-and-spoke ADVPN topology

Options:

A.

On the spokes, auto-discovery-receiver must be enabled on the IPsec VPNs to the hub.

B.

On the spokes, auto-discovery-sender must be enabled on the IPsec VPNs to hubs.

C.

On the hubs, auto-discovery-receiver must be enabled on the IPsec VPNs to spokes.

D.

On the hubs, auto-discovery-forwarder must be enabled on the IPsec VPNs to hubs.

Buy Now
Questions 30

Refer to the exhibits. The exhibits show two IPsec templates to define Branch IPsec 1 and Branch_IPsec_2. Each template defines a VPN tunnel. The error message that FortiManager displayed when the administrator tried to assign the second template to the FortiGate device is also shown. Which statement best describes the cause of the issue?
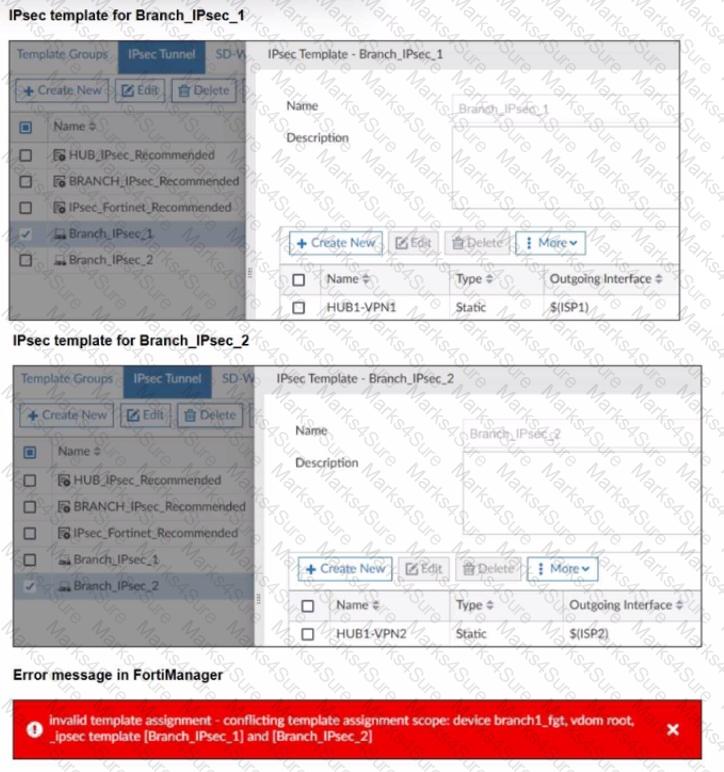
NSE7_SSE_AR-26 Question 30

Exhibit 1

Options:

A.

You can assign only one template with a tunnel type of static to each FortiGate device.

B.

You can assign only one IPsec template to each FortiGate device.

C.

You should review the branch1_fgt configuration for configured tunnels in the rootVDOM.

D.

You should use the same outgoing interface of both templates.

Buy Now
Questions 31

During the implementation of endpoint-based access controls on FortiSASE, an administrator must determine how security posture tags will improve policy enforcement and performance across managed devices.

In this context, what are two advantages of using security posture tags? (Choose two.)

Options:

A.

Security posture tags can help monitor endpoint system resource use.

B.

Security posture tags can be used to allow or deny access to network resources.

C.

Security posture tags can determine the security posture of an endpoint.

D.

Security posture tags can be assigned to endpoint profiles based on user groups.

Buy Now
Questions 32

Refer to the exhibit. For your ZTP deployment, you review the CSV file shown in exhibit and note that it is missing important information. Which two elements must you change before you can import it into FortiManager? (Choose two.)
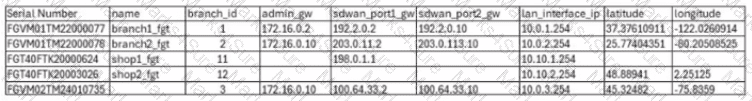
NSE7_SSE_AR-26 Question 32

Exhibit 1

Options:

A.

You must associate a device blueprint with each device

B.

You must define a name for each device

C.

You must define a value for each device and each metadata variable that defines an IP address.

D.

You must define a value for each device and each user-defined metadata variable.

Buy Now
Questions 33

Refer to the exhibits, which show the configuration of an SD-WAN rule and the corresponding rule status and routing table. The administrator wants to understand the expected behavior for traffic matching the SD-WAN rule. Based on the exhibits, what can the administrator expect for traffic matching the SD-WAN rule?
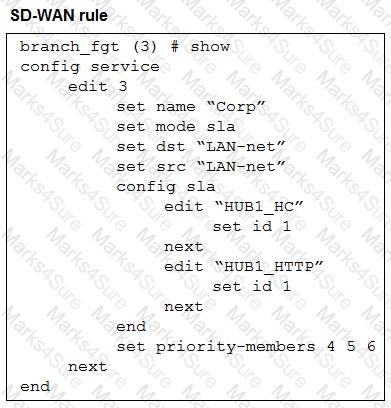
NSE7_SSE_AR-26 Question 33

Exhibit 1

NSE7_SSE_AR-26 Question 33

Exhibit 2

Options:

A.

The traffic will be routed over HUB1-VPN3.

B.

The traffic will be routed over HUB1-VPN2

C.

The traffic will be routed over HUB1-VPN1.

D.

The traffic will be load balanced across all three overlays

Buy Now
Exam Code: NSE7_SSE_AR-26
Exam Name: Fortinet NSE 7 - FortiSASE 26 Architect
Last Update: Oct 23, 2026
Questions: 110

PDF + Testing Engine

$55.71   $185.69

Testing Engine

$42.85   $142.83

PDF (Q&A)

$47.13   $157.11