Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: pass65

Free Practice Questions for the Fortinet Network Security Expert NSEI_OTS_AR-7.6 Exam (2026 Updated)

At Marks4sure, we are dedicated to providing IT professionals with the most accurate and reliable preparation materials for the Fortinet NSEI_OTS_AR-7.6 exam. To support your certification journey, we have made a selection of our premium 2026 Fortinet Network Security Expert practice questions and answers available completely free. You can take this practice test as many times as you need. Every question includes a detailed, expertly verified explanation to ensure you fully grasp the core security concepts before test day.

Questions 4

For the installation of your first FortiGate device, you want to minimize the impact in your OT network. Therefore, you deploy it initially as an offline IDS. Which two statements about this deployment are correct? (Choose two answers)

Options:

A.

The FortiGate device acts as a network sensor.

B.

The cybersecurity visibility increases with the security profiles.

C.

Attacks, including zero-day attacks, are blocked.

D.

OT traffic flows through the FortiGate device.

Buy Now
Questions 5

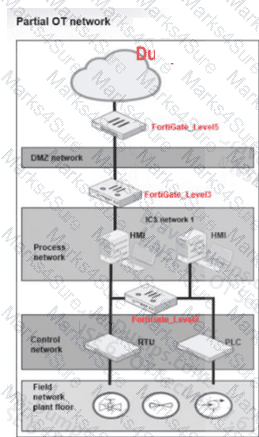
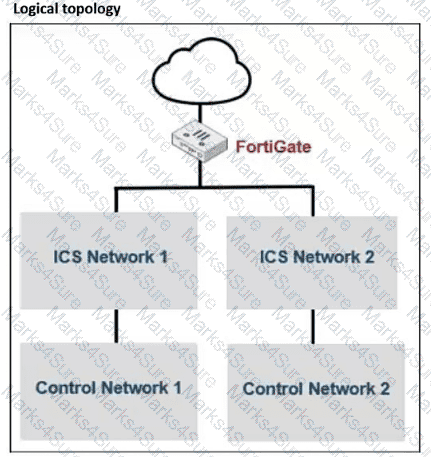
Refer to the exhibit. A partial OT network is shown. You must improve the security of this OT network and implement internal segmentation between network 1 and network 2. How can you achieve the segmentation? (Choose one answer)
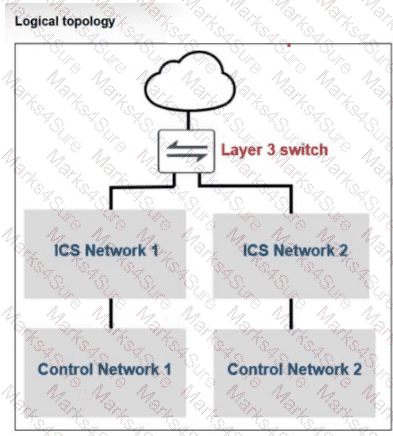
NSEI_OTS_AR-7.6 Question 5

Options:

A.

You can configure universal ZTNA.

B.

You can configure one traffic VDOM.

C.

You can configure an explicit software switch.

D.

You can configure forward domain IDs for each network.

Buy Now
Questions 6

Refer to the exhibit.

NSEI_OTS_AR-7.6 Question 6

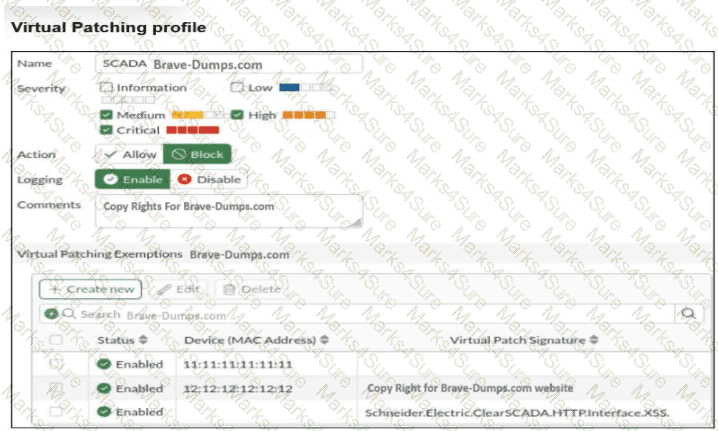
A Virtual Patching profile is shown. You have recently updated your SCADA system and would like to apply the SCADA virtual patching profile. Which two statements about this profile are correct? (Choose two answers)

Options:

A.

Only the vulnerability Schneider.Electric.ClearSCADA.HTTP.Interface.XSS is still present.

B.

Low severity signatures are not blocked for the device with the MAC address 12:12:12:12:12.

C.

This profile blocks critical severity signatures for all the devices.

D.

The device with the MAC address 11:11:11:11:11 is considered to have no vulnerabilities.

Buy Now
Questions 7

According to the IEC 62443 standard, your security level is 4 . What is your OT environment defending against? (Choose one answer)

Options:

A.

Intentional cyberthreats posed by skilled malicious users

B.

An intentional attack with low resources

C.

A syndicate of cyber extortion with extensive resources

D.

A casual exposure

Buy Now
Questions 8

Refer to the exhibit.

NSEI_OTS_AR-7.6 Question 8

A partial OT network is shown. In this OT network, you must add additional security measures to detect OT protocols and, therefore, increase the traffic visibility. Which security sensor must you implement to detect the OT protocols in this network? (Choose one answer)

Options:

A.

Device detection on all the FortiGate interfaces.

B.

Inline IDS on FortiGate_Level3.

C.

Application sensor set to monitor on all the FortiGate devices.

D.

IPS sensor on FortiGate_Level5.

Buy Now
Questions 9

As the first step in your OT network protection plan, you must identify the OT protocols that the FortiGate device supports. Which two configurations must you implement on this FortiGate device? (Choose two answers)

Options:

A.

You must enable Device detection on all the interfaces.

B.

You must implement an Application Control security profile that monitors OT.

C.

You must enable the OT signatures.

D.

You must implement an Intrusion Prevention security profile that monitors OT.

Buy Now
Questions 10

Refer to the exhibits.

NSEI_OTS_AR-7.6 Question 10

NSEI_OTS_AR-7.6 Question 10

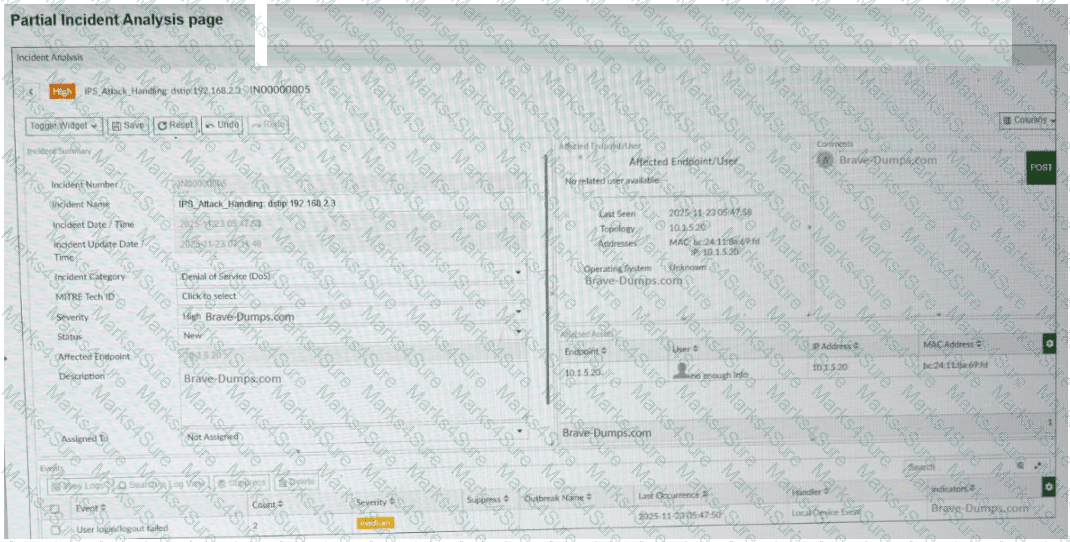
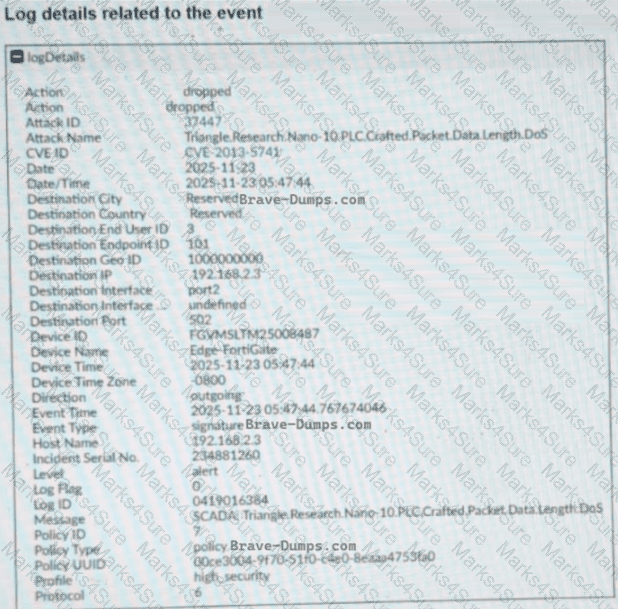
A partial Incident Analysis page and the log details related to the event are shown. An attack is reported on your OT network. You analyze the corresponding incident. Based on the information provided on the Incident Analysis page and the log details, which two statements are correct? (Choose two answers)

Options:

A.

The attack uses the Modbus protocol.

B.

The attack is mitigated.

C.

The attack uses the IEC 104 protocol.

D.

The event severity is high.

E.

The target device IP address is 10.1.5.20.

Buy Now
Questions 11

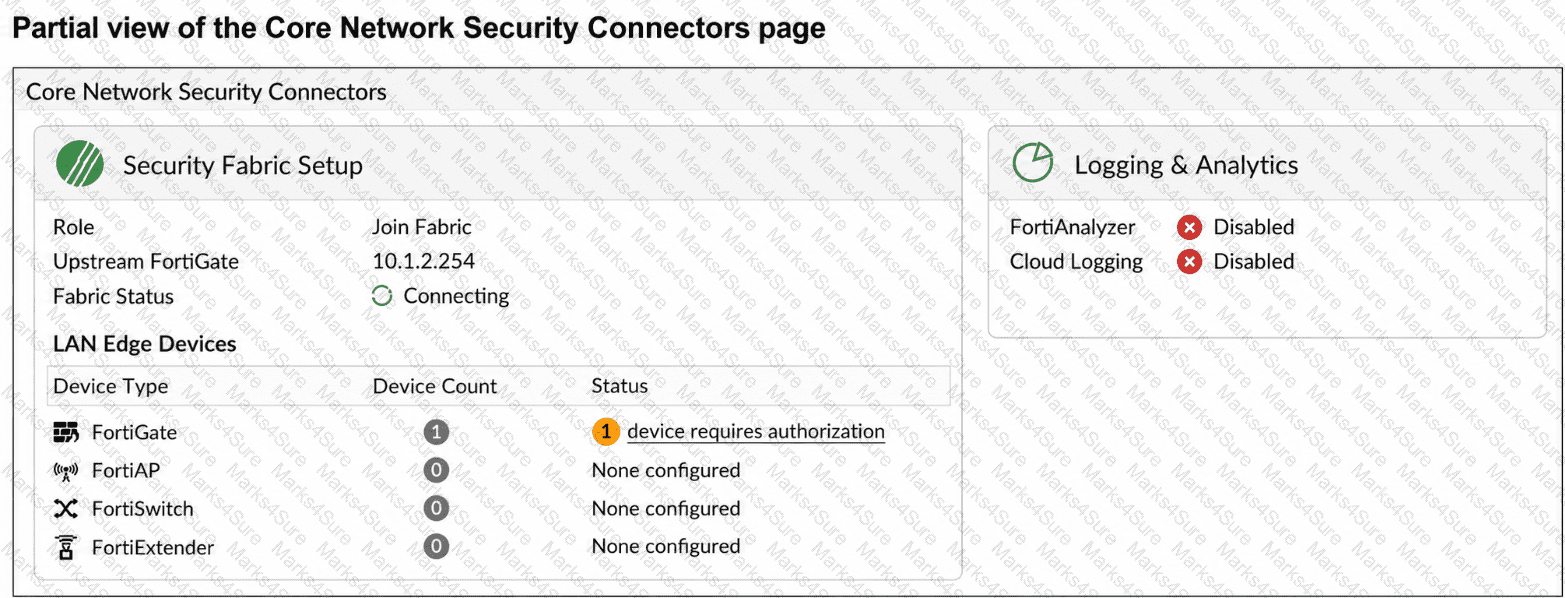
Refer to the exhibit.

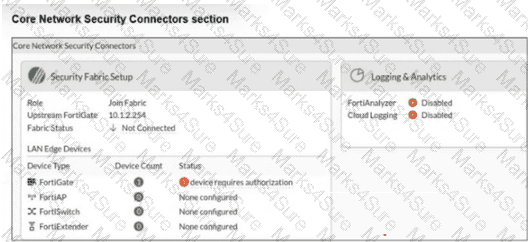
NSEI_OTS_AR-7.6 Question 11

The Core Network Security Connectors page of a FortiGate device is shown. You are configuring the Security Fabric in your OT network. One of the devices is not sending logs to FortiAnalyzer. When you check the status of the FortiGate device, it is Disabled as shown in the exhibit. Which two actions must you perform to enable this FortiGate device to send logs to FortiAnalyzer? (Choose two answers)

Options:

A.

You must configure the Logging & Analytics settings on this FortiGate device.

B.

You must configure the Fabric settings on FortiAnalyzer.

C.

You must authorize this FortiGate device on FortiAnalyzer.

D.

You must authorize this FortiGate device on the root FortiGate.

Buy Now
Questions 12

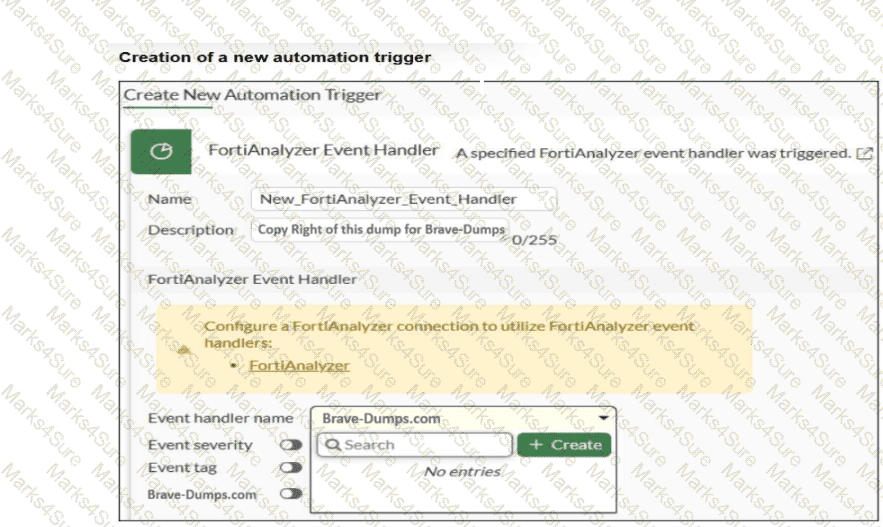
Refer to the exhibit.

NSEI_OTS_AR-7.6 Question 12

An automation trigger creation wizard is shown. You want to automate some tasks in your OT network. In a FortiGate device, you create a new automation trigger based on a FortiAnalyzer event handler. When you want to configure the Event handler name field, the event handler created in FortiAnalyzer is not shown. What are two reasons for this? (Choose two answers)

Options:

A.

You must configure the Fabric settings on the FortiGate device.

B.

You must enable Automation Stitch in the event handler on FortiAnalyzer.

C.

You must click + Create in the Event handler name field.

D.

You must add the FortiGate device to FortiAnalyzer and authorize it.

Buy Now
Questions 13

Refer to the exhibit.

NSEI_OTS_AR-7.6 Question 13

A partial OT network is shown.

The OT network is divided into two main networks with a FortiGate device operating in NAT mode.

How can you further segment network 1 from network 2?

Options:

A.

You can configure universal ZTNA.

B.

You can configure the FortiGate interface as an implicit software switch.

C.

You can configure two traffic VDOMs.

D.

You can configure different forward domain IDs for network 1 and network 2.

Buy Now
Questions 14

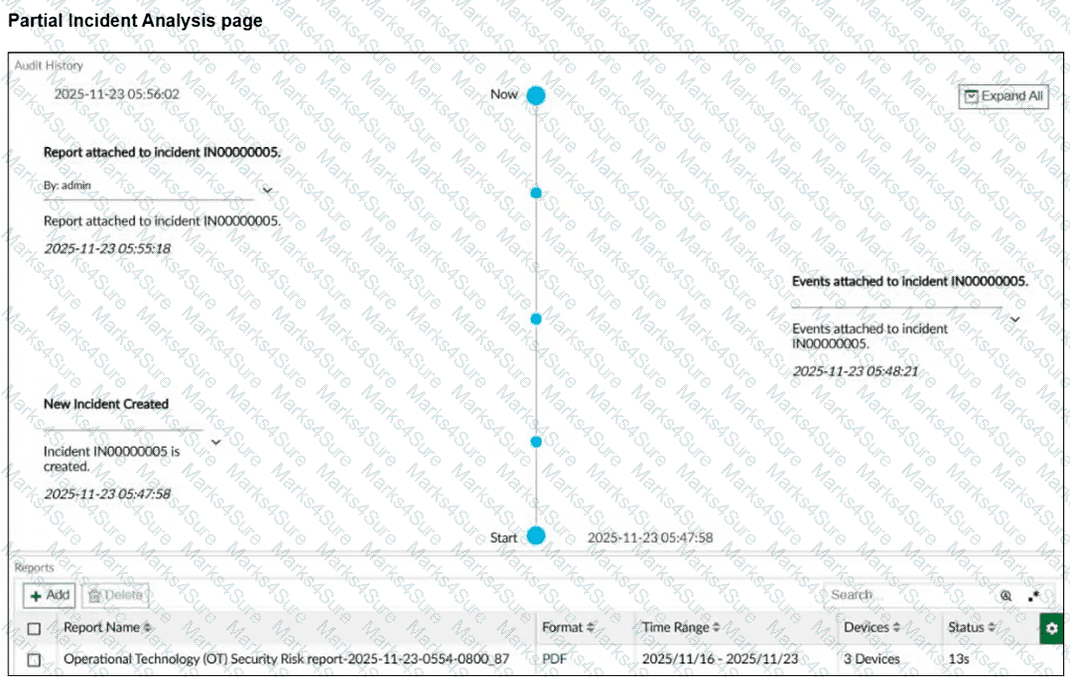
Refer to the exhibit.

NSEI_OTS_AR-7.6 Question 14

A partial Incident Analysis page is shown. How was the 360-Degree Security Review OT report attached to the incident? (Choose one answer)

Options:

A.

Automatically by a stitch

B.

Automatically by an event handler

C.

Automatically by a playbook

D.

Manually by an administrator

Buy Now
Questions 15

You want to protect OT devices that are not updated against known vulnerabilities so you apply virtual patching to the firewall policies. What must you check to confirm that the OT devices are virtually patched? (Choose one answer)

Options:

A.

The output of the CLI command get virtual-patch profile

B.

The OT View page

C.

The output of the CLI command get rule otvp status

D.

The Asset Identity List page

Buy Now
Questions 16

Refer to the exhibit.

NSEI_OTS_AR-7.6 Question 16

The Core Network Security Connectors page of the FortiGate-2 device is shown. Which statement is correct? (Choose one answer)

Options:

A.

FortiGate-2 serves as Fabric Root.

B.

You must enable Security Fabric Connection on the FortiGate-2 interface.

C.

You must configure the FortiAnalyzer settings on FortiGate-2.

D.

FortiGate-2 is not authorized on the root FortiGate.

Buy Now
Exam Code: NSEI_OTS_AR-7.6
Exam Name: Fortinet NSE I - OT Security 7.6 Architect
Last Update: Sep 11, 2026
Questions: 56

PDF + Testing Engine

$64.99   $185.69

Testing Engine

$49.99   $142.83

PDF (Q&A)

$54.99   $157.11