Free Practice Questions for the Microsoft Certified: Cybersecurity Architect Expert SC-100 Exam (2026 Updated)
At Marks4sure, we are dedicated to providing IT professionals with the most accurate and reliable preparation materials for the Microsoft SC-100 exam. To support your certification journey, we have made a selection of our premium 2026 Microsoft Certified: Cybersecurity Architect Expert practice questions and answers available completely free. You can take this practice test as many times as you need. Every question includes a detailed, expertly verified explanation to ensure you fully grasp the core security concepts before test day.
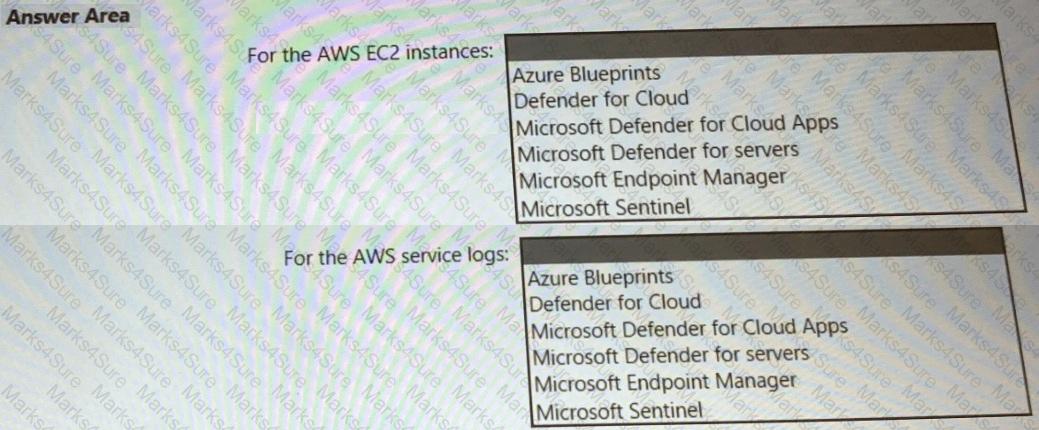
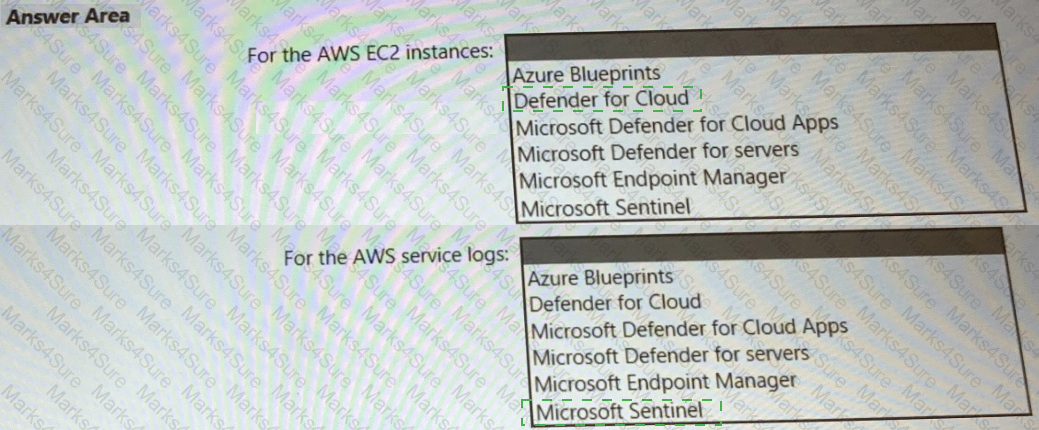
You need to recommend a solution to meet the AWS requirements.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You need to recommend a solution to meet the security requirements for the virtual machines.
What should you include in the recommendation?
SC-100 Report Card
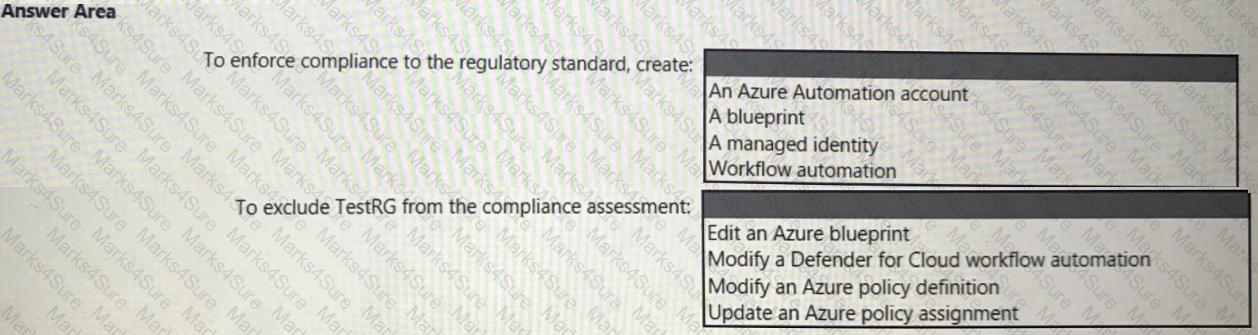
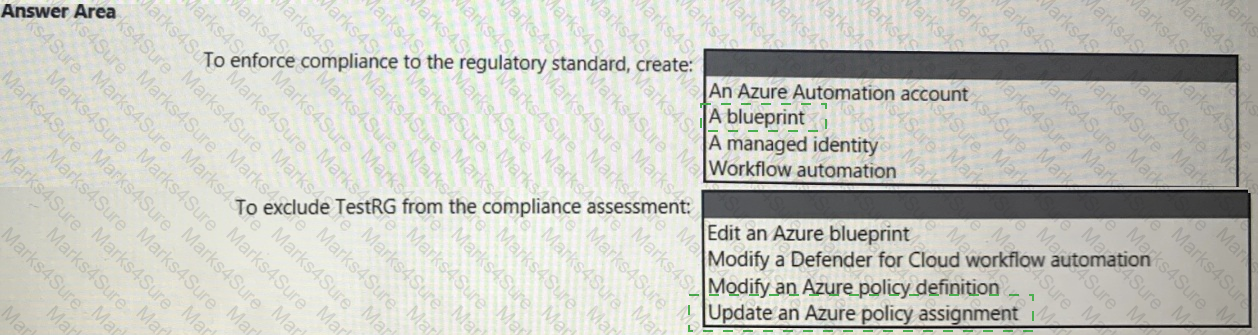
You need to recommend a solution to meet the compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
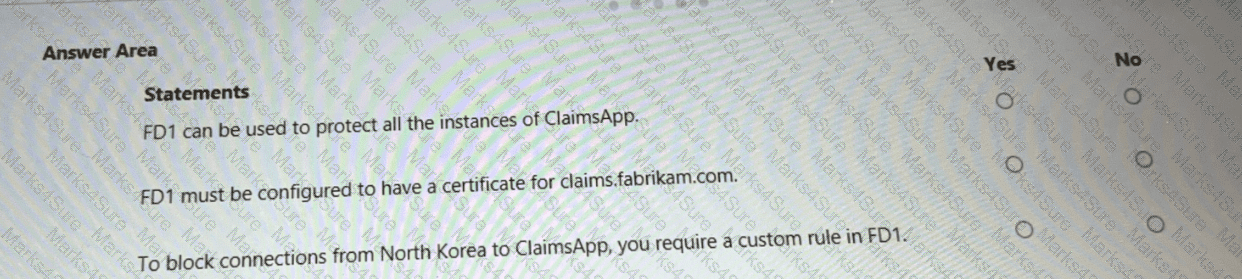
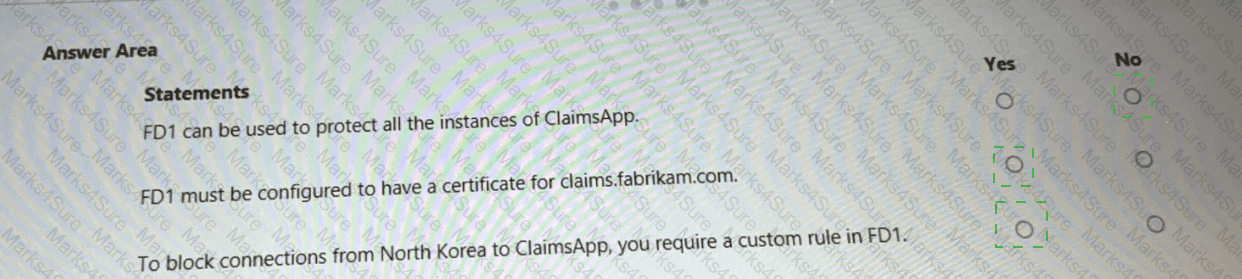
You are evaluating the security of ClaimsApp.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE; Each correct selection is worth one point.
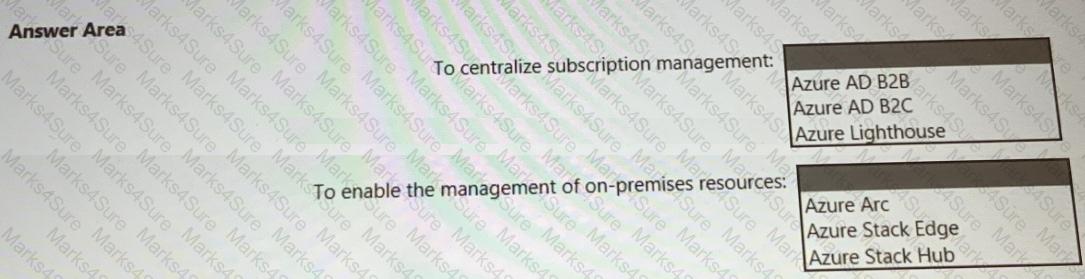
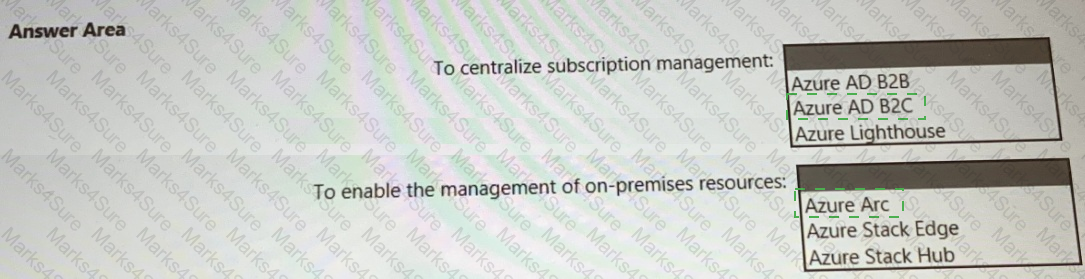
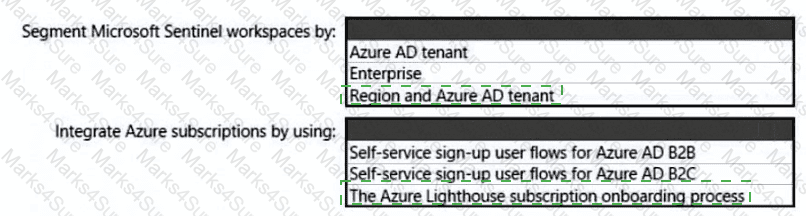
You need to recommend a multi-tenant and hybrid security solution that meets to the business requirements and the hybrid requirements. What should you recommend? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
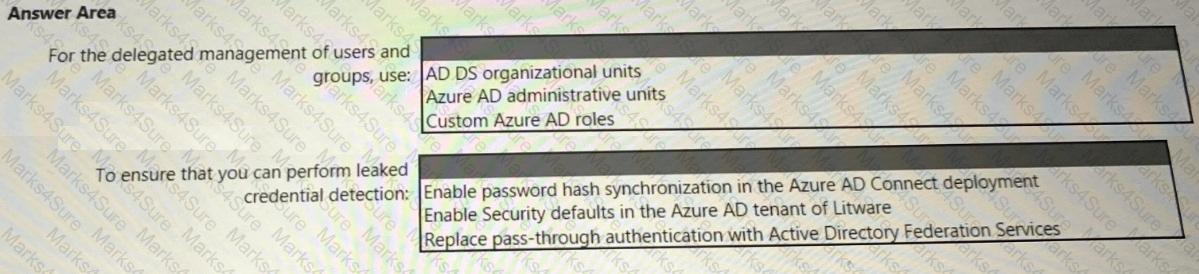
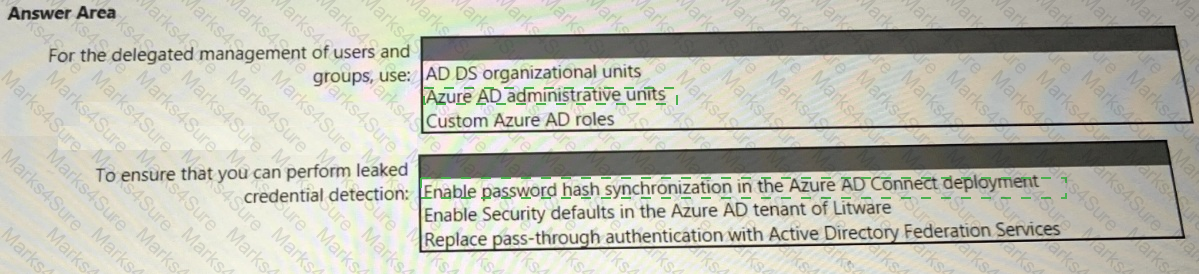
You need to recommend an identity security solution for the Azure AD tenant of Litware. The solution must meet the identity requirements and the regulatory compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You need to design a strategy for securing the SharePoint Online and Exchange Online data. The solution must meet the application security requirements.
Which two services should you leverage in the strategy? Each correct answer presents part of the solution. NOTE; Each correct selection is worth one point.
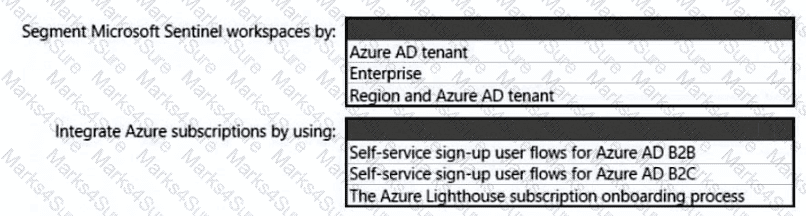
You need to recommend a SIEM and SOAR strategy that meets the hybrid requirements, the Microsoft Sentinel requirements, and the regulatory compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
To meet the application security requirements, which two authentication methods must the applications support? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
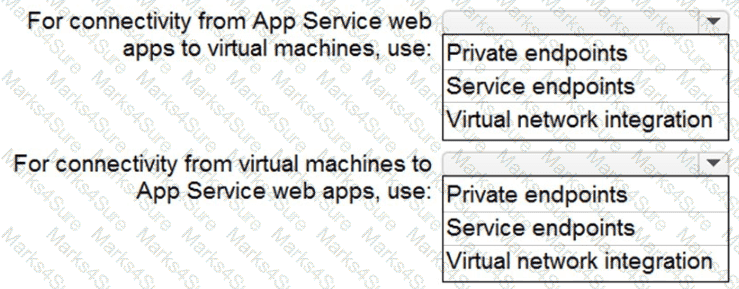
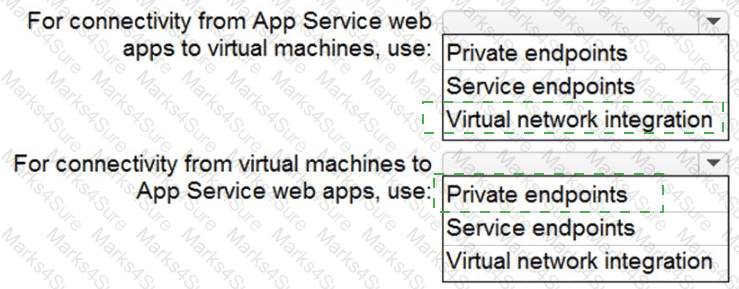
You need to recommend a strategy for App Service web app connectivity. The solution must meet the landing zone requirements. What should you recommend? To answer, select the appropriate options in the answer area. NOTE Each correct selection is worth one point.
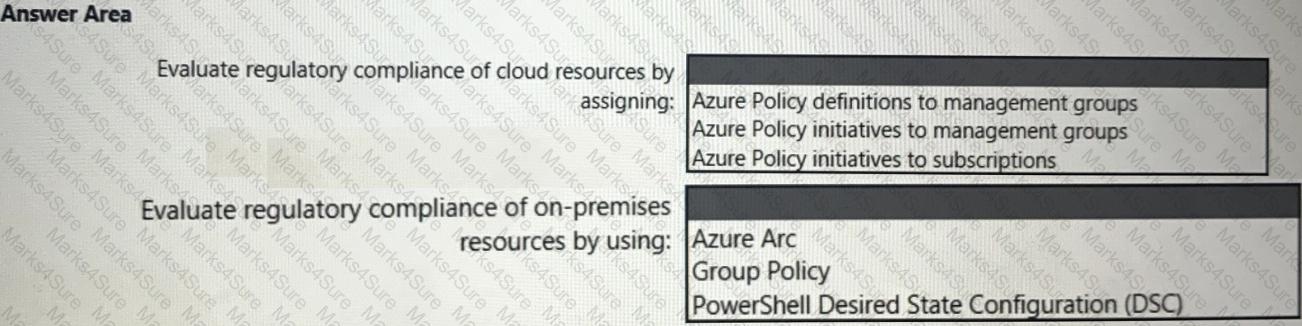
You need to recommend a solution to evaluate regulatory compliance across the entire managed environment. The solution must meet the regulatory compliance requirements and the business requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
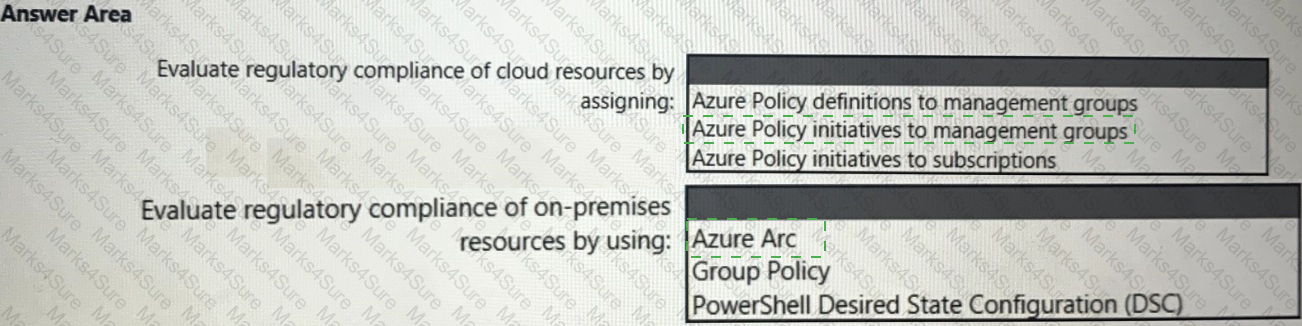
You need to recommend a strategy for securing the litware.com forest. The solution must meet the identity requirements. What should you include in the recommendation? To answer, select the appropriate options in the answer area. NOTE; Each correct selection is worth one point.
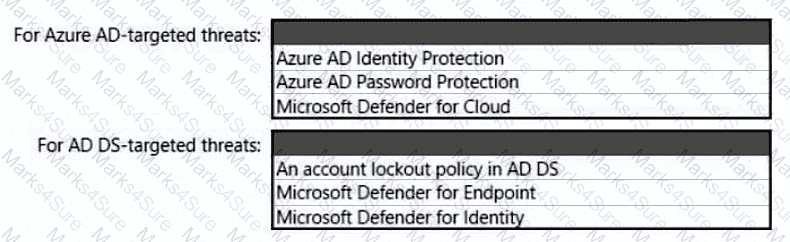
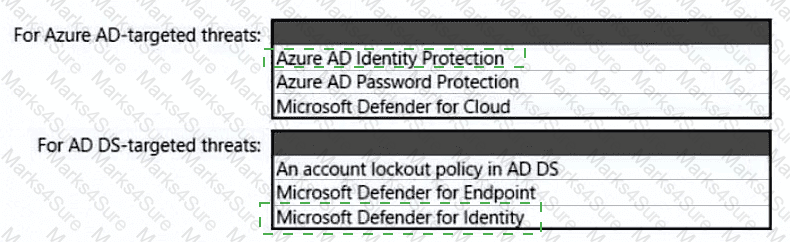
You have a Microsoft 365 subscription and an Azure subscription. Microsoft 365 Defender and Microsoft Defender for Cloud are enabled.
The Azure subscription contains 50 virtual machines. Each virtual machine runs different applications on Windows Server 2019.
You need to recommend a solution to ensure that only authorized applications can run on the virtual machines. If an unauthorized application attempts to run or be installed, the application must be blocked automatically until an administrator authorizes the application.
Which security control should you recommend?
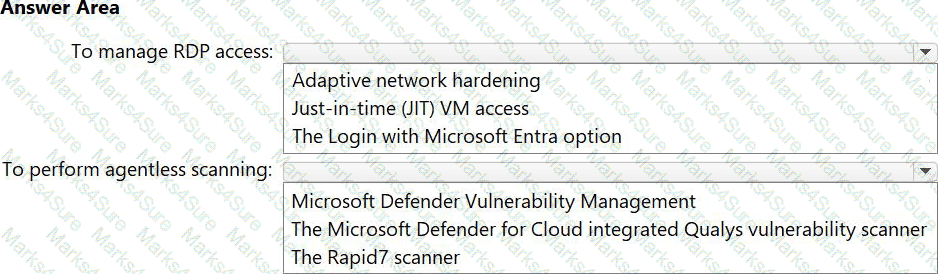
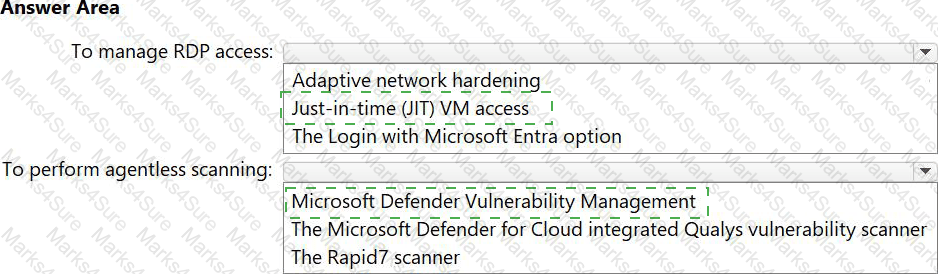
You have an Azure subscription. The subscription contains an Azure Bastion host and 100 virtual machines that run Windows Server 2022. The virtual machines have Microsoft Defender for Servers Plan 2 enabled.
You need to recommend a security solution for the virtual machines that meets the following requirements:
• Administrators must request RDP access to the virtual machines by using the Azure portal.
• Remote Desktop sessions must be limited to a maximum of three hours.
• Agentless scanning must be scheduled to run on each virtual machine.
What should you recommend using? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
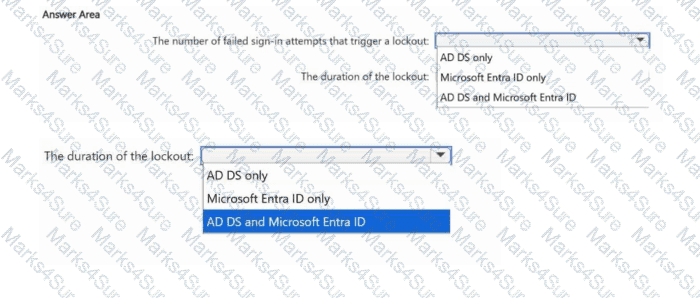
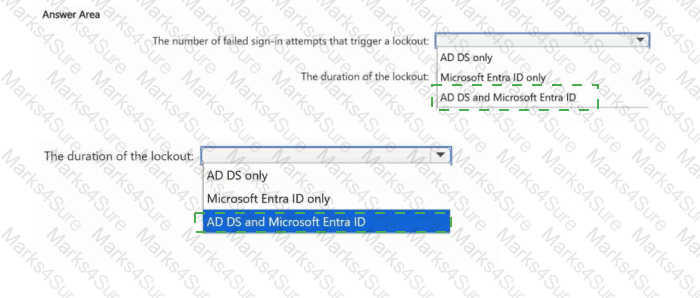
Your network contains an Active Directory Domain Services (AD DS) domain named Domain1.
You have a Microsoft Entra tenant.
Domain1 syncs with the tenant by using Microsoft Entra Connect.
You need to evaluate Microsoft Entra smart lockout by testing the following account lockout considerations:
The number of failed sign-in attempts that trigger a lockout.
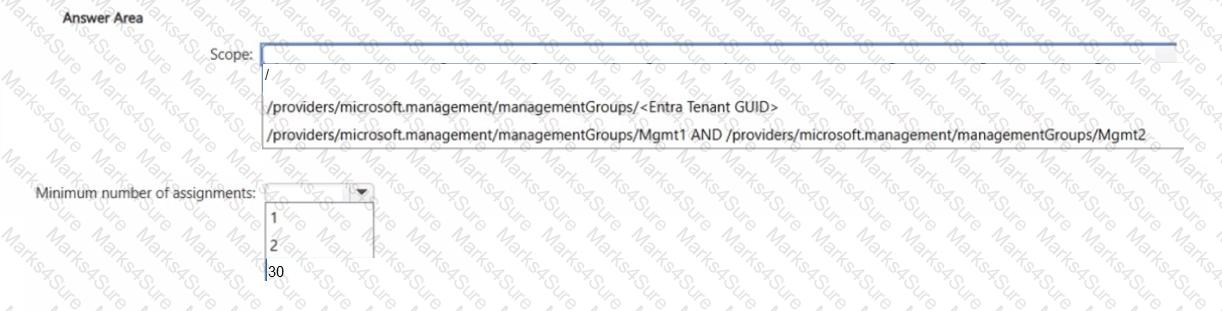
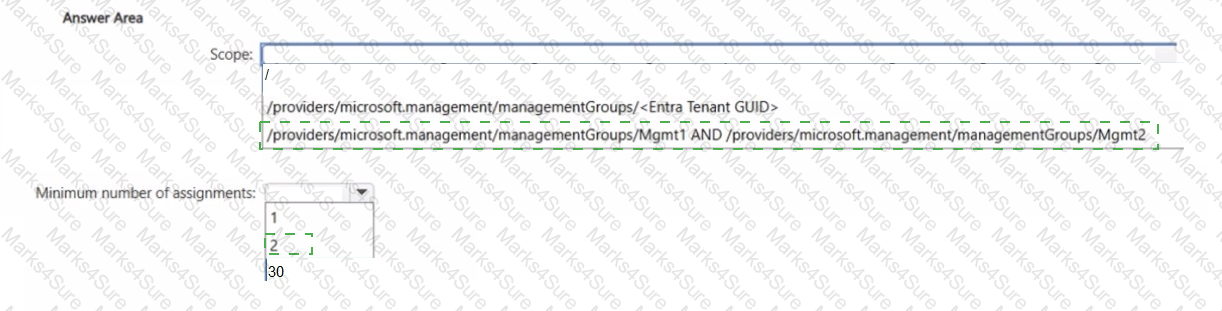
You have a Microsoft Entra tenant named contoso.com. You have 30 Azure subscriptions that are linked to contoso.com. The tenant contains the management groups shown in the following table.
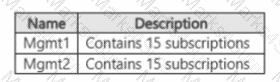
You need to design a governance solution to manage access to all the Azure Storage accounts across the subscriptions. The solution must meet the following requirements:
• Use custom role-based access control (RBAQ to provide granular access to control plane and data plane operations.
• Minimize administrative effort.
At which scope should you assign the roles, and what is the minimum number of assignments per role? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
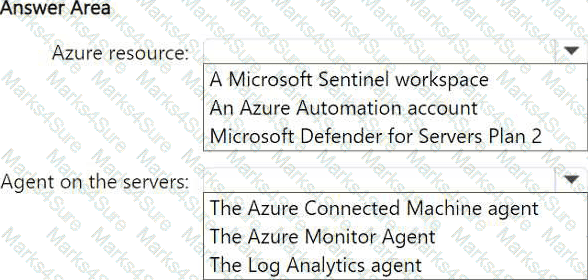
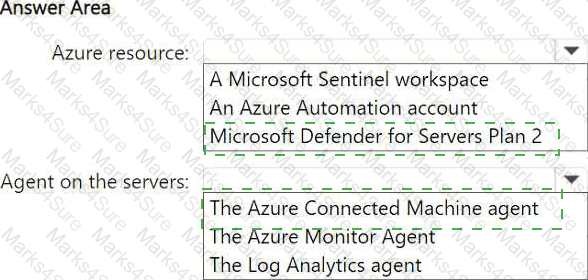
You have 1,000 on-premises servers that run Windows Server 2022 and 500 on-premises servers that run Linux.
You have an Azure subscription that contains the following resources:
• A Log Analytics workspace
• A Microsoft Defender Cloud Security Posture Management (CSPM) plan
You need to deploy Update Management for the servers.
What should you configure? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
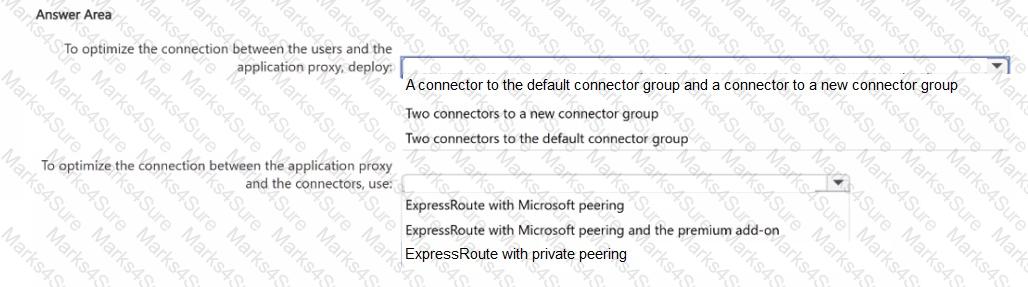
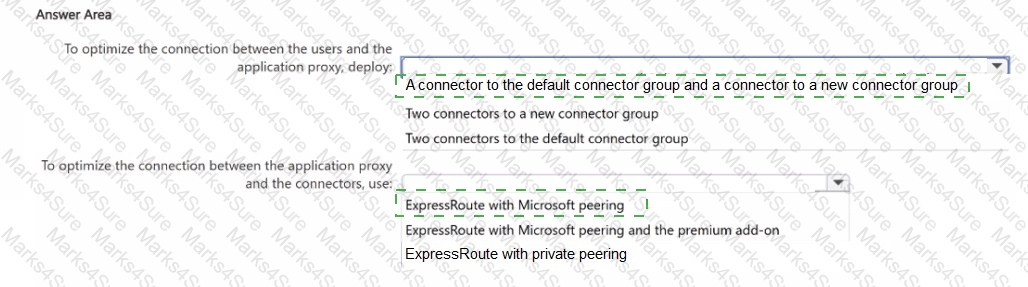
Your company has offices in New York City and London. The London office contains an on-premises app named Appl.
You have a Microsoft Entra tenant named contoso.com that is hosted in North America.
You plan to manage access to App1 for the users in the London office by using Microsoft Entra Private Access. You will deploy Private Access by performing the following actions in the London office:
• Deploy Microsoft Entra Private Network connectors.
• Provision an ExpressRoute circuit to the closest peering location.
You need to optimize the network for the planned deployment. The solution must meet the following requirements:
• Maximize redundancy for connectivity to Appl.
• Minimize network latency when accessing Appl.
• Maximize security.
• Minimize costs.
What should you include in the solution? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You design cloud-based software as a service (SaaS) solutions.
You need to recommend ransomware attacks. The solution must follow Microsoft Security Best Practices.
What should you recommend doing first?
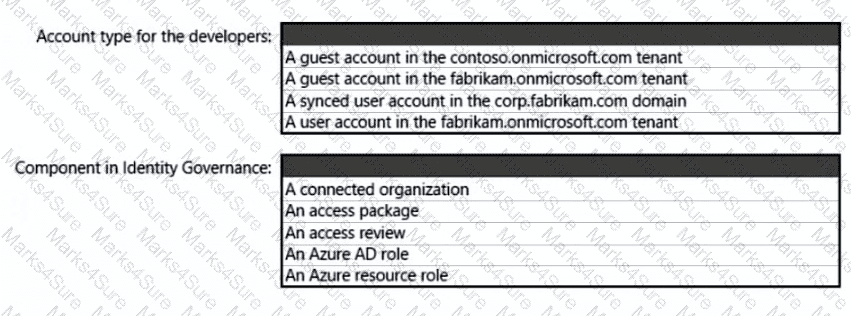
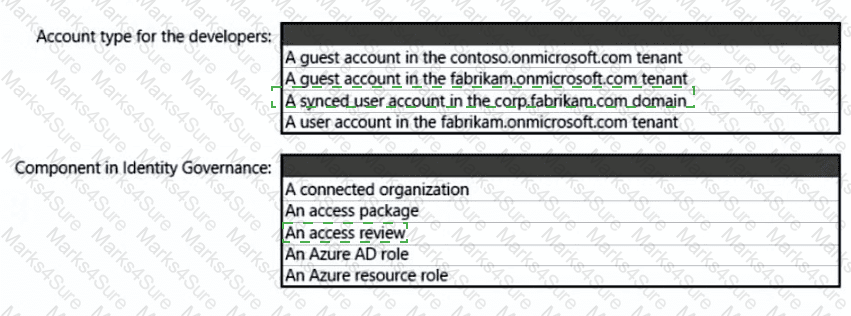
You need to recommend a solution to secure the MedicalHistory data in the ClaimsDetail table. The solution must meet the Contoso developer requirements.
What should you include in the recommendation?
You need to recommend a solution for securing the landing zones. The solution must meet the landing zone requirements and the business requirements.
What should you configure for each landing zone?
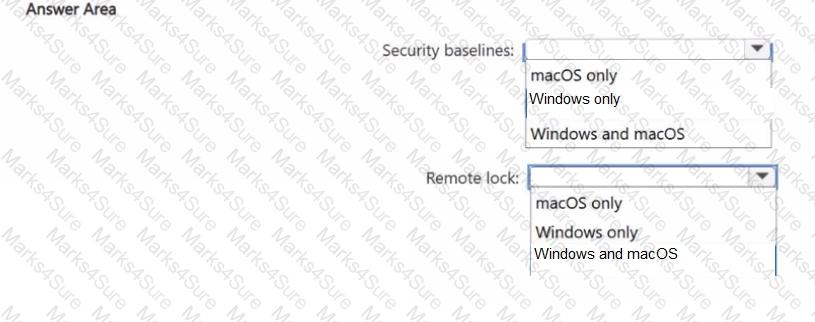
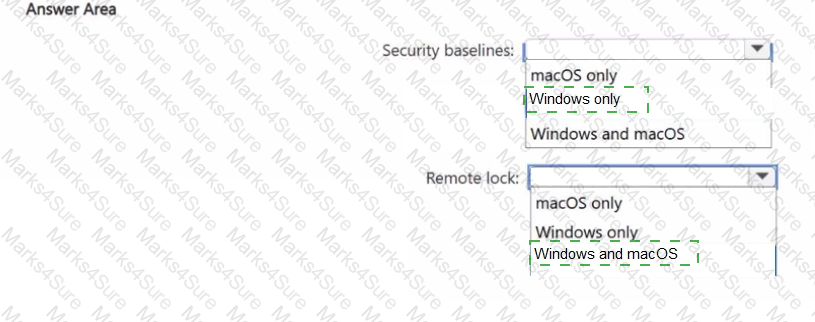
You have 500 Windows 11 devices and 200 macOS devices. The devices are managed by using Microsoft Intune and are subject to compliance policies.
You plan to deploy the following Intune features:
• Security baselines
• Remote lock of noncompliant devices
Which feature will be supported by each platform? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Your company has an Azure subscription that uses Microsoft Defender for Cloud. The company signs a contract with the United States government. You need to review the current subscription for NIST 800-53 compliance. What should you do first?
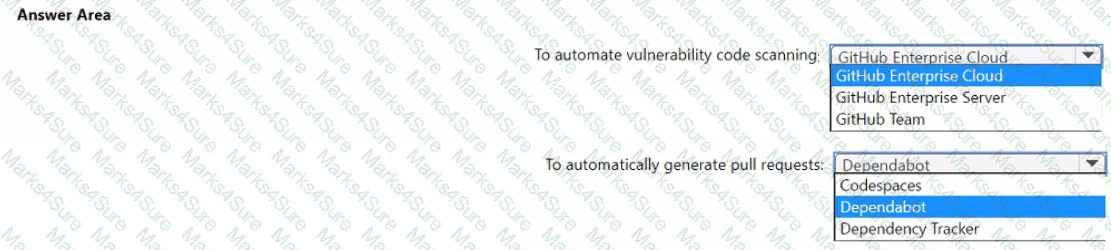
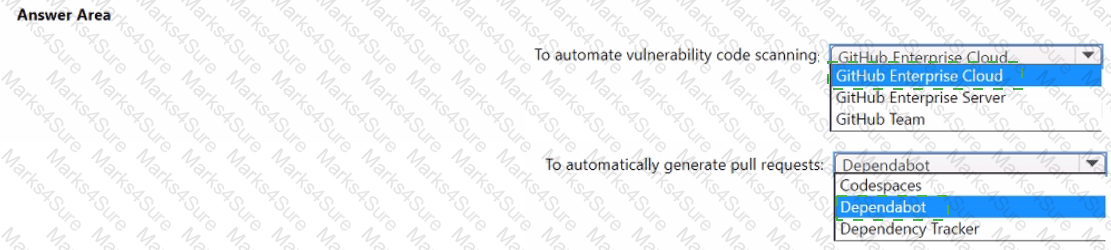
You plan to automate the development and deployment of a Nodejs-based app by using GitHub.
You need to recommend a DevSecOps solution for the app. The solution must meet the following requirements:
• Automate the generation of pull requests that remediate identified vulnerabilities.
• Automate vulnerability code scanning for public and private repositories.
• Minimize administrative effort.
• Minimize costs.
What should you recommend using? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have an on-premises app that processes Personally Identifiable Information (PII) and sends the data to Azure .
The app includes the following components:
• APIs that receive and send the PII
• A data ingestion pipeline that stores the PII in an Azure Data Lake Storage Gen2 account
A compliance policy requires that all the PII data be encrypted by using encryption keys that are regularly rotated and stored in a central repository.
You need to recommend a solution that adhere to the compliance policy. The solution must minimize administrative effort.
Which two components should you include in the recommendation? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point
You have a Microsoft 365 subscription that uses Microsoft Purview.
You need to recommend a solution that will provide guidance on how to ensure that Personally Identifiable Information (PII) in the subscription adheres to local privacy regulations. The solution must minimize administrative effort.
Which Microsoft Purview solution should you include in the recommendation?
Your company is developing an invoicing application that will use Azure Active Directory (Azure AD) B2C. The application will be deployed as an App Service web app. You need to recommend a solution to the application development team to secure the application from identity related attacks. Which two configurations should you recommend? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
You have a Microsoft 365 subscription that uses Microsoft Defender XDR. The subscription contains 500 devices that are enrolled in Microsoft Intune. The subscription contains 500 users that connect to external software as a service (SaaS) apps by using the devices.
You need to implement a solution that meets the following requirements:
• Allows user access to SaaS apps that Microsoft has identified as low risk
• Blocks user access to Saas apps that Microsoft has identified as high risk
Solution: From the Microsoft Defender portal, you set Web content filtering to On and create a web content filtering policy. Does this meet the goal?
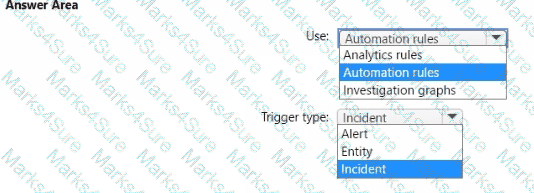
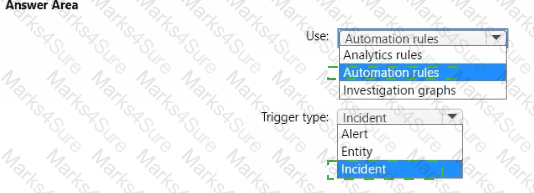
You have an Azure subscription that contains a Microsoft Sentinel workspace named MSW1. MSW1 includes 50 scheduled analytics rules.
You need to design a security orchestration automated response (SOAR) solution by using Microsoft Sentinel playbooks. The solution must meet the following requirements:
• Ensure that expiration dates can be configured when a playbook runs.
• Minimize the administrative effort required to configure individual analytics rules.
What should you use to invoke the playbooks, and which type of Microsoft Sentinel trigger should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have legacy operational technology (OT) devices and loT devices.
You need to recommend best practices for applying Zero Trust principles to the OT and loT devices based on the Microsoft Cybersecurity Reference Architectures (MCRA). The solution must minimize the risk of disrupting business operations.
Which two security methodologies should you include in the recommendation? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point
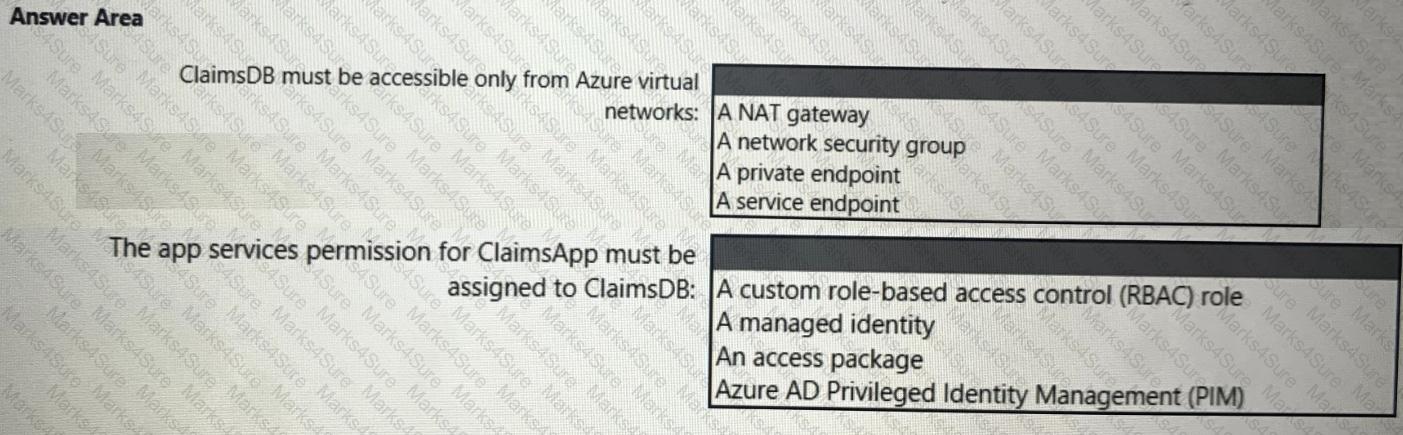
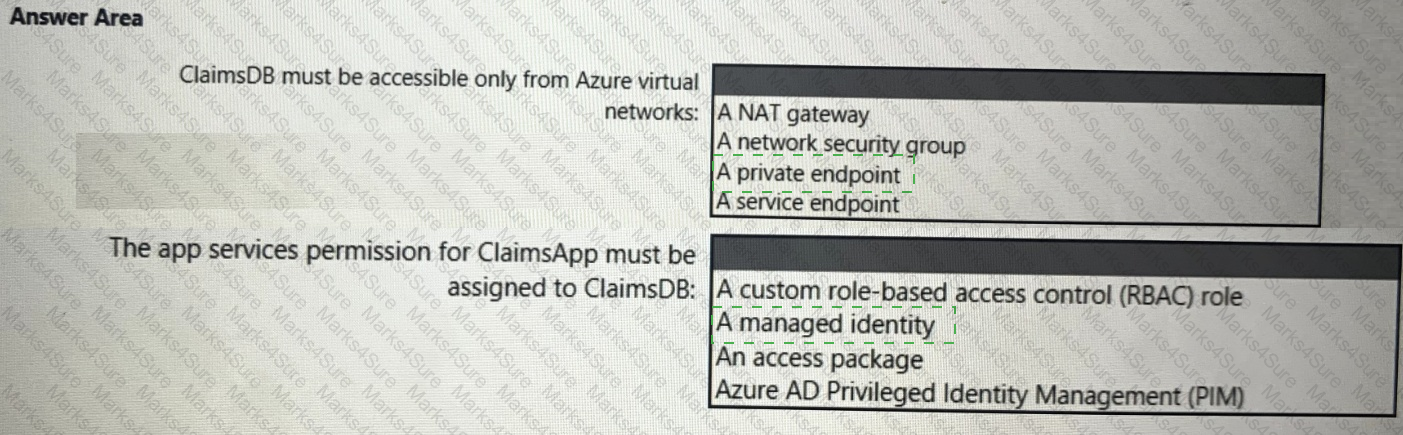
You need to recommend a solution to meet the requirements for connections to ClaimsDB.
What should you recommend using for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
PDF + Testing Engine
Testing Engine
PDF (Q&A)