Free Practice Questions for the WGU Courses and Certificates Secure-Software-Design Exam (2026 Updated)
At Marks4sure, we are dedicated to providing IT professionals with the most accurate and reliable preparation materials for the WGU Secure-Software-Design exam. To support your certification journey, we have made a selection of our premium 2026 Courses and Certificates practice questions and answers available completely free. You can take this practice test as many times as you need. Every question includes a detailed, expertly verified explanation to ensure you fully grasp the core security concepts before test day.
The security team has a library of recorded presentations that are required viewing tor all new developers in the organization. The video series details organizational security policies and demonstrates how to define, test for. and code tor possible threats.
Which category of secure software best practices does this represent?
Which concept is demonstrated when every module in a particular abstraction layer of a computing environment can only access the information and resources that are necessary for its legitimate purpose?
Company leadership has contracted with a security firm to evaluate the vulnerability of all externally lacing enterprise applications via automated and manual system interactions. Which security testing technique is being used?
The security team is reviewing whether changes or open issues exist that would affect requirements for handling personal information documented in earlier phases of the development life cycle.
Which activity of the Ship SDL phase is being performed?
The final security review determined that two low-risk security issues identified in testing are still outstanding. Developers have assured the security team that both issues can be resolved quickly once they have time to fix them. The security team is confident that developers can fix the flaws in the first post-release patch.
What is the result of the final security review?
Using a web-based common vulnerability scoring system (CVSS) calculator, a security response team member performed an assessment on a reported vulnerability in the company ' s customer portal. The base score of the vulnerability was 9.9 and changed to 8.0 after adjusting temporal and environmental metrics.
Which rating would CVSS assign this vulnerability?
Senior IT staff has determined that a new product will be hosted in the cloud and will support web and mobile users. Developers will need to deliver secure REST services. Android and IOS mobile apps. and a web application. Developers are currently determining how to deliver each part of the overall product.
Which phase of the software development lifecycle (SDLC) is being described?
Which category classifies identified threats that have defenses in place and do not expose the application to exploits?
Which secure coding best practice says to ensure that buffers are allocated correctly and at the right size, that input strings are truncated to a reasonable length, and that resources, connections, objects, and file handles are destroyed once the application no longer needs them?
Which category classifies identified threats that have some defenses in place and expose the application to limited exploits?
Which DKEAD category has a risk rating based on the threat exploit ' s potential level of harm?
Security testers have completed testing and are documenting the results of vulnerability scans and penetration analysis They are also creating documentation lo share with the organization ' s largest customers.
Which deliverable is being prepared?
The scrum team decided that before any change can be merged and tested, it must be looked at by the learns lead developer, who will ensure accepted coding patterns are being followed and that the code meets the team ' s quality standards.
Which category of secure software best practices is the team performing?
Which security assessment deliverable identities possible security vulnerabilities in the product?
Which secure coding best practice ensures sensitive information is not disclosed in any responses to users, authorized or unauthorized?
The product team has been tasked with updating the user interface (UI). They will change the layout and also add restrictions to field lengths and what data will be accepted.
Which secure coding practice is this?
Due to positive publicity from the release of the new software product, leadership has decided that it is in the best interests of the company to become ISO 27001 compliant. ISO 27001 is the leading international standard focused on information security.
Which security development life cycle deliverable is being described?
During fuzz testing of the new product, random values were entered into input elements Search requests were sent to the correct API endpoint but many of them failed on execution due to type mismatches.
How should existing security controls be adjusted to prevent this in the future?
The security testing team received a report from one of the contracted penetration testing vendors that details a flaw discovered in the login component of the new software product, along with a recommended fix.
Which phase of the penetration testing process is the team in?
In which step of the PASTA threat modeling methodology is vulnerability and exploit analysis performed?
Which secure coding best practice ensures sensitive information is not disclosed in any responses to users, authorized or unauthorized?
An individual is developing a software application that has a back-end database and is concerned that a malicious user may run the following SOL query to pull information about all accounts from the database:
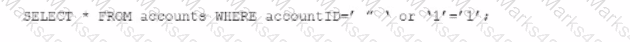
Which technique should be used to detect this vulnerability without running the source codes?
Which SDL security goal is defined as ensuring timely and reliable access to and use of information?
A recent vulnerability scan uncovered an XML external entity (XXE) Haw that could allow attackers to return the contents of a system file by including a specific payload in an XML request.
How should the organization remediate this vulnerability?
A company is moving forward with a new product. Product scope has been determined, teams have formed, and backlogs have been created. Developers are actively writing code for the new product, with one team concentrating on delivering data via REST services, one Team working on the mobile apps, and a third team writing the web application.
Which phase of the software development lifecycle (SDLC) is being described?
After being notified of a vulnerability in the company’s online payment system, the Product Security Incident Response Team (PSIRT) was unable to recreate the vulnerability in a testing lab.
What is the response team’s next step?
Which type of security analysis is performed by reviewing source code line-by-line after other security analysis techniques have been executed?
Developers have finished coding, and changes have been peer-reviewed. Features have been deployed to a pre-production environment so that analysts may verify that the product is working as expected.
Which phase of the Software Development Life Cycle (SDLC) is being described?
PDF + Testing Engine
Testing Engine
PDF (Q&A)