Free Practice Questions for the CompTIA Security+ SY0-801 Exam (2026 Updated)
At Marks4sure, we are dedicated to providing IT professionals with the most accurate and reliable preparation materials for the CompTIA SY0-801 exam. To support your certification journey, we have made a selection of our premium 2026 CompTIA Security+ practice questions and answers available completely free. You can take this practice test as many times as you need. Every question includes a detailed, expertly verified explanation to ensure you fully grasp the core security concepts before test day.
A marketing team launches a new AI solution that trains on sensitive customer data to help provide recommendations on its next possible marketing campaign. This team requires granular access to the tool for different levels of sensitive data. Which of the following should a systems administrator prioritize when provisioning access?
Two companies with separate, private cloud deployments plan to collaborate on a short-term project. Company A creates a new, public cloud deployment for Company B to access during this project. Which of the following describes the new cloud architecture for both companies?
A company implements a new web-based application for internal use. To limit creating separate accounts and passwords, the security administrator wants to use the company's existing cloud identity provider to log in to the application. Which of the following should the administrator choose?
A security administrator reviews vulnerability assessment reports. Which of the following should the security administrator prioritize if all vulnerabilities have the same Common Vulnerability Scoring System (CVSS) score of 9.1?
A security administrator must deploy security monitoring of servers in a subnet without adding network overhead. Which of the following should the administrator implement?
During an investigation of a known malicious IP address, the security operations center (SOC) team analyzes the following packet capture output:
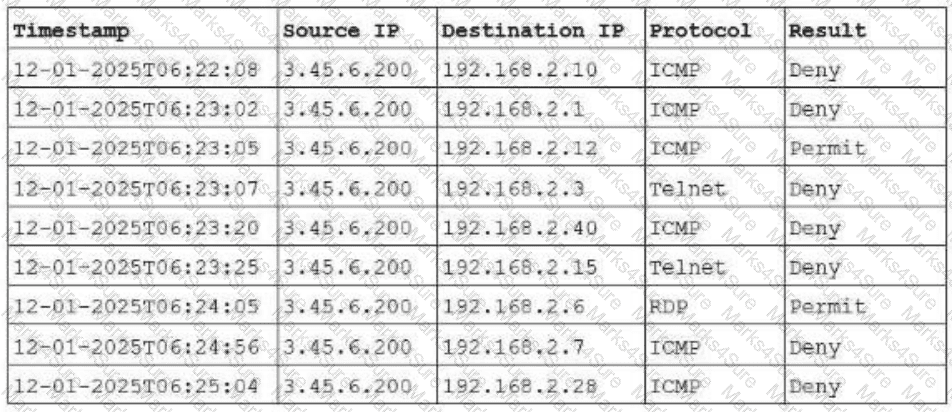
Which of the following should the SOC team do first?
Which of the following takes the outcomes of a third-party risk assessment as input?
Which of the following is best suited to monitor and control the outbound movement of sensitive file content?
PDF + Testing Engine
Testing Engine
PDF (Q&A)