Select your duration, then choose PDF, simulator or the complete bundle.
- 356 Q&A with explanations
- Printable PDF, any device
- Offline access, no login
ECCouncil 212-89 Dumps Questions Answers
- Timed mock exams
- Domain score analytics
- Web-based + downloadable
See the Exam Simulator in Action
Prepare with our 212-89 Practice Questions before taking the exam.
Practice 212-89 questions in real-time no install required
First Try then Buy
- 212-89 All Real Exam Questions
- 212-89 Exam easy to use and print PDF format
- Cover All syllabus and Objectives
- Download Free 212-89 Demo (Try before Buy)
- Free Frequent Updates
- 100% Passing Guarantee by Marks4sure
212-89 Report Card
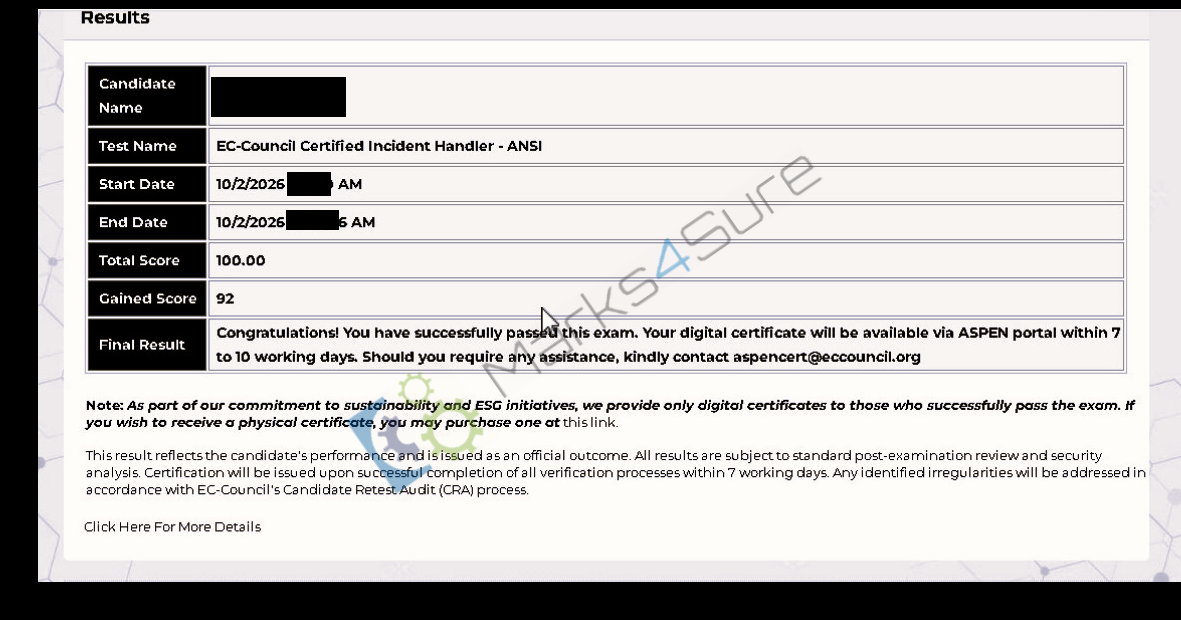
ECCouncil 212-89 Last Week Results!
198
Customers Passed
ECCouncil 212-89
94%
Average Score In Real Exam
At Testing Centre
89%
Questions came word by
word from this dump
Browse 212-89 Practice Questions by Domain
Every 212-89 question is tagged to its official exam domain, so you can jump straight to the 212-89 topic you need to strengthen instead of working through the set in random order.
Practicing in the Online or Download Engine? Your score is automatically broken down the same way - domain by domain - so you can see exactly where you're strongest and weakest as you go.
212-89 Q&A's Detail
Top ECCouncil Certifications
Updated Exam Questions
Easily Downloadable on all Smart devices
100% Guaranteed Success on the First Try
Designed by Subject matter Experts
Printable Questions & Answers (PDF)
90 Days Free updates Subscription
212-89 Practice Questions — Mapped to the Official EC-Council ECIH v3 Blueprint
The 212-89 exam is the certification exam behind EC-Council Certified Incident Handler (ECIH) v3 — a specialist-level credential built entirely around one job: detecting, containing, and recovering from cybersecurity incidents. Where a foundational cert like Security+ touches incident response as one topic among many, ECIH spends its entire ten-module curriculum on it, from building a response plan and assembling a team through handling specific incident types and writing the report that closes the case.
Version 3 is a meaningful update over ECIH v2, adding a dedicated Endpoint Security module covering mobile, IoT, and OT/ICS incidents — a direct response to how much incident response has shifted beyond the traditional network perimeter. The credential is 100% aligned with the NICE 2.0 and CREST frameworks and maps to real job titles: Incident Handler, Incident Responder, SOC Analyst, CSIRT Analyst, Cyber Forensic Investigator, and similar roles.
Marks4sure's 212-89 practice test is written directly against the official ECIH v3 module blueprint, using scenario-based questions that mirror how the real exam tests incident-response judgment — not simple definition recall. Every question includes a full explanation covering the reasoning behind the correct containment, eradication, or recovery decision, so you're building the same operational judgment the exam is designed to validate.
If you're pursuing ECIH certification, this page walks through exactly what's tested, how the exam is structured, and how Marks4sure's question set, testing engine, and study formats are built around the real, current blueprint.
Official 212-89 Exam Format & Modules
| Detail | Specification |
|---|---|
| Exam Code | 212-89 |
| Certification | EC-Council Certified Incident Handler (ECIH v3) |
| Vendor | EC-Council |
| Number of Questions | 100 multiple-choice questions |
| Duration | 3 hours |
| Passing Score | No single published percentage — EC-Council uses multiple exam forms with varying cut scores; 70% is the figure most consistently cited by training providers as a study benchmark |
| Delivery | EC-Council Exam Portal, with online remote proctoring available |
| Exam Voucher Cost | $450 (often bundled with official training) |
| Certification Validity | 3 years, with continuing education requirements |
| Framework Alignment | NICE 2.0 and CREST compliant |
212-89 ECIH v3 Modules
| # | Module | Focus |
|---|---|---|
| 1 | Introduction to Incident Handling and Response | Threats, frameworks (NIST SP 800-61), IR team roles, SOAR fundamentals, relevant laws and standards |
| 2 | Incident Handling and Response (IH&R) Process | The 9-step workflow: Preparation → Detection and Recording → Triage and Notification → Containment → Evidence Gathering → Forensic Analysis → Eradication → Recovery → Post-Incident Activities |
| 3 | Forensic Readiness and First Response | Securing the crime scene, order of volatility, write-blockers, chain of custody |
| 4 | Handling and Responding to Malware Incidents | Identification, isolation, eradication strategies, backups, recovery |
| 5 | Handling and Responding to Email Security Incidents | Phishing triage, header/body analysis, URL and attachment detonation, blocklists |
| 6 | Handling and Responding to Network Security Incidents | Network-layer detection, containment, and recovery |
| 7 | Handling and Responding to Web Application Security Incidents | Web attack detection and response |
| 8 | Handling and Responding to Cloud Security Incidents | AWS, Azure, and GCP incident response side by side |
| 9 | Handling and Responding to Insider Threats | Detection and response for internal actors |
| 10 | Handling and Responding to Endpoint Security Incidents (new in v3) | Mobile, IoT, and OT/ICS incident response |
Marks4sure 212-89 Practice Questions — What You Get
Marks4sure's 212-89 question set is written against the official ten-module ECIH v3 blueprint above, using original incident-responder scenarios rather than simple recall questions. Every question includes a full explanation with "why wrong" analysis for the incorrect options, so you're learning to sequence a response correctly — for example, never eradicating a threat before evidence is preserved — rather than memorizing an isolated answer key.
- Comprehensive Q&A set with expert explanations, mapped to all 10 official ECIH v3 modules
- Single-choice format matching the real exam's multiple-choice style
- Covers the full v3 scope, including the new Endpoint Security module (mobile, IoT, OT/ICS)
- Available as PDF, Online Testing Engine, and offline Download Engine
- Domain-level score analytics to identify weak areas
- Free demo questions available before purchase
- 3-month free content updates included
- 100% money back guarantee if you don't pass
- 356 Verified Questions & Answers covering every exam domain
- 354 Single Choice Questions with detailed explanations
- 2, fill in the blanks
Study Formats
| Format | Best For | Key Features |
|---|---|---|
| PDF Study Pack | Reading offline, printing, any device | Printable, no login required, works offline |
| Online Testing Engine | Studying from any browser | Timed & practice modes, domain score analytics, no install |
| Download Engine | Studying without internet access | Full offline installer, same analytics as online engine |
| PDF + Testing Engine Bundle | Candidates who want both formats | Combines all PDF content with full simulator access |
Because the IH&R Process and Malware Incidents modules carry the heaviest weighting, domain-level analytics matter here — you want to know precisely whether you're weak on the nine-step response sequence versus a specific incident type, not just an overall score.
Why Marks4sure Instead of Ordinary Dumps
Search results for 212-89 are full of sites promising "real exam Braindumps" or claiming their content is pulled word-for-word from the actual test. Here's why that's a risk you don't want to take — and what Marks4sure does differently:
| Feature | Ordinary "Exam Dumps" Sites | Marks4sure Premium |
|---|---|---|
| Question source | Often claims of leaked/reconstructed exam content | Independently written from EC-Council's official ECIH v3 module blueprint |
| Certification risk | Using leaked exam content can violate EC-Council's certification agreement and put your credential at risk | No policy violation — content is original prep material, not exam content |
| Explanations | Often answer-only, little to no reasoning provided | Every question includes a full explanation with why-wrong analysis, mapped to the exact module being tested |
| Real-world readiness | Memorization-focused, doesn't build real incident-response judgment | Scenario-based, built to reflect how 212-89 actually tests response sequencing and containment decisions |
| Content freshness | Frequently outdated — especially risky given the v3 update added an entirely new Endpoint module | Updated as EC-Council revises the ECIH blueprint |
| Long-term value | Passing without understanding puts real security incidents — and your credibility — at risk | Understanding-first prep means the certification actually reflects your incident-handling skills |
Start Preparing for 212-89 (ECIH v3) Today
Marks4sure's 212-89 practice questions are built for EC-Council's official ECIH v3 module blueprint, with full explanations, domain analytics, and your choice of PDF, Online, or Download Engine format. Try the free demo dumps questions before you buy, and get 3 months of updates included with every package — backed by a 100% money back guarantee.
ECCouncil 212-89 Exam Dumps FAQs
The best ECIH Exam preparation strategy includes:
- Studying official ECCouncil guides
- Practicing with Marks4sure’s 212-89 real PDF questions
- Using our 212-89 testing engine for real exam simulation
- Reviewing previous 212-89 exam questions and dumps
Purchasing study materials for the ECCouncil 212-89 Exam on marks4sure.com is a breeze. Just follow these simple steps:
- Visit Marks4sure.com.
- Use the search bar to find ECCouncil 212-89 study guide materials, such as PDFs or testing engines.
- Select the materials you need and add them to your cart.
- Proceed to checkout and complete the payment process.
Once your payment is processed, you'll have instant access to the 212-89 study materials, helping you start your preparation right away.
EC Council Certified Incident Handler (ECIH v3) Questions and Answers
James is a professional hacker and is employed by an organization to exploit their cloud services. In order to achieve this, James created anonymous access to the cloud services to carry out various attacks such as password and key cracking, hosting malicious data, and DDoS attacks. Which of the following threats is he posing to the cloud platform?
Malicious Micky has moved from the delivery stage to the exploitation stage of the kill chain. This malware wants to find and report to the command center any useful services on the system. Which of the following recon attacks is the MOST LIKELY to provide this information?
Following a spear-phishing campaign targeting executive-level employees, a mid-sized financial firm experienced unauthorized access to internal systems, leading to widespread disruption of customer-facing applications. Although the technical issues were resolved within days, the breach triggered legal scrutiny and negative press coverage. Several major customers expressed concern about the firm ' s risk posture and began transitioning to competitors. Investor confidence was impacted as the stock value dipped, and senior leadership initiated a damage control campaign. Which of the following best categorizes the broader consequences experienced by the organization?
212-89 PDF vs Testing Engine
Both 212-89 PDF and Testing Engine have all the Real Questions including Multiple Choice, Simulation and Drag Drop Questions.
We provide you 3 Months Free ECCouncil 212-89 Exam Updates at no cost.
We provide you 212-89 dump with 100% passing Guarantee With Money Back Guarantee.
Purchase ECCouncil 212-89 Exam Product with fully SSL Secure system and available in your Marks4Sure Account.
We respect full Privacy of our customers and would not share information with any third party.
Experience Real Exam Environment with our testing engine.
Testing Mode and Practice Mode.
Our 212-89 Testing Engine will Save your 212-89 Exam Score so you can Review it later to improve your results.
Marks4Sure Test engine Provides Option to choose randomize and non-randomize Questions Set.
Our 212-89 Testing Engine provides option to save your exam Notes.
What our customers are saying
 East Timor
 France
I cleared my ECCouncil 212-89 test by a score of 90%. This was all possible due to marks4sure for helping me out.
 Gambia The
I prepared for the ECCouncil 212-89 test and scored 91% on the exam. I am grateful to marks4sure for providing such top-quality education.
 Costa Rica
 Qatar
 Albania