Free Practice Questions for the CompTIA SecAI+ CY0-001 Exam (2026 Updated)
At Marks4sure, we are dedicated to providing IT professionals with the most accurate and reliable preparation materials for the CompTIA CY0-001 exam. To support your certification journey, we have made a selection of our premium 2026 CompTIA SecAI+ practice questions and answers available completely free. You can take this practice test as many times as you need. Every question includes a detailed, expertly verified explanation to ensure you fully grasp the core security concepts before test day.
A disgruntled employee changed the company policies that a chatbot references in order to create confusion and disrupt the business.
Which of the following AI-generated vulnerabilities is the employee exploiting?
A large number of employees receive a video message in which the company ' s CEO states that the company will be filing for bankruptcy. After an investigation, it was discovered that the CEO did not send this message.
Which of the following is this scenario an example of?
CY0-001 Report Card

A security operations center (SOC) analyst needs to automate multiple security tasks by breaking them down into smaller parts.
Which of the following AI tools is the best for this task?
Which of the following is the primary security risk when deploying AI models in production?
A loan company compares a machine learning model that was found on the dark web with the company ' s proprietary model. Using proprietary information, the company generates the following:
Input
Dark web model
Company ' s proprietary model
Jane A.
Approve
Approve
John B.
Deny
Deny
Ann J.
Deny
Deny
Joe H.
Approve
Approve
Which of the following should the AI red team recommend to mitigate risks for future deployments?
A security administrator must provide access controls for AI systems to list tables.
Which of the following should the administrator implement?
Which of the following is the most concerning risk for a company that allows corporate end users to use public-facing large language models (LLMs)?
An organization recently created a custom model that integrates with a language model (LLM). The developer notices that the application programming interface (API) costs have increased.
Which of the following is the best control to reduce cost?
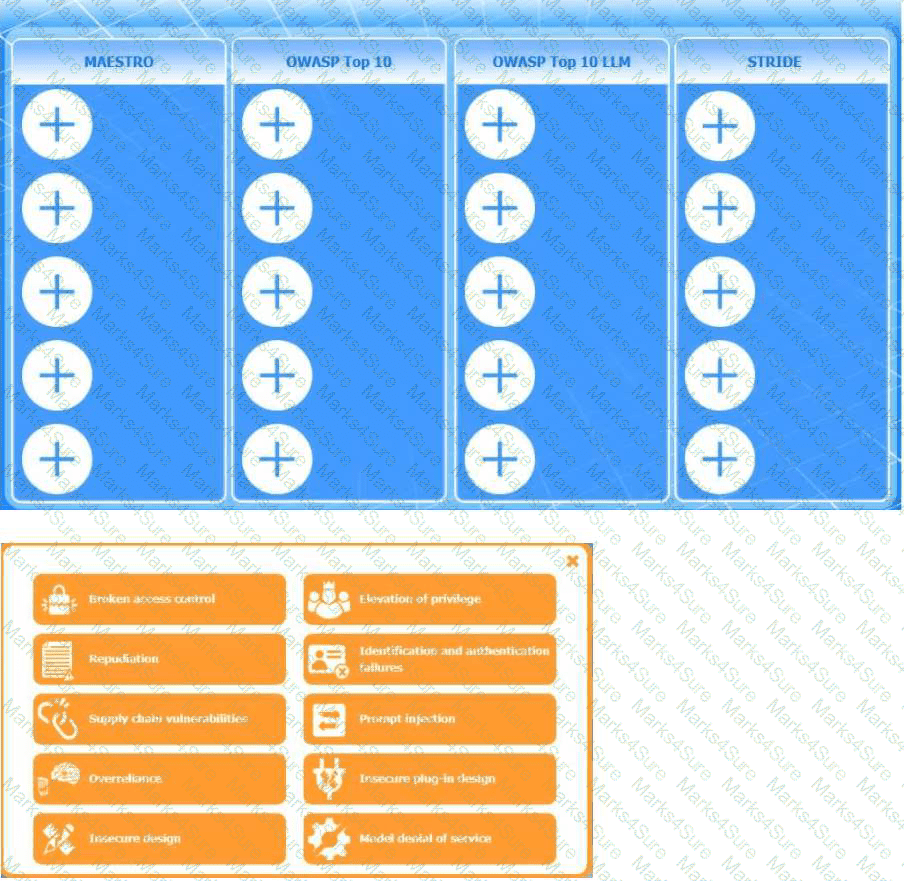
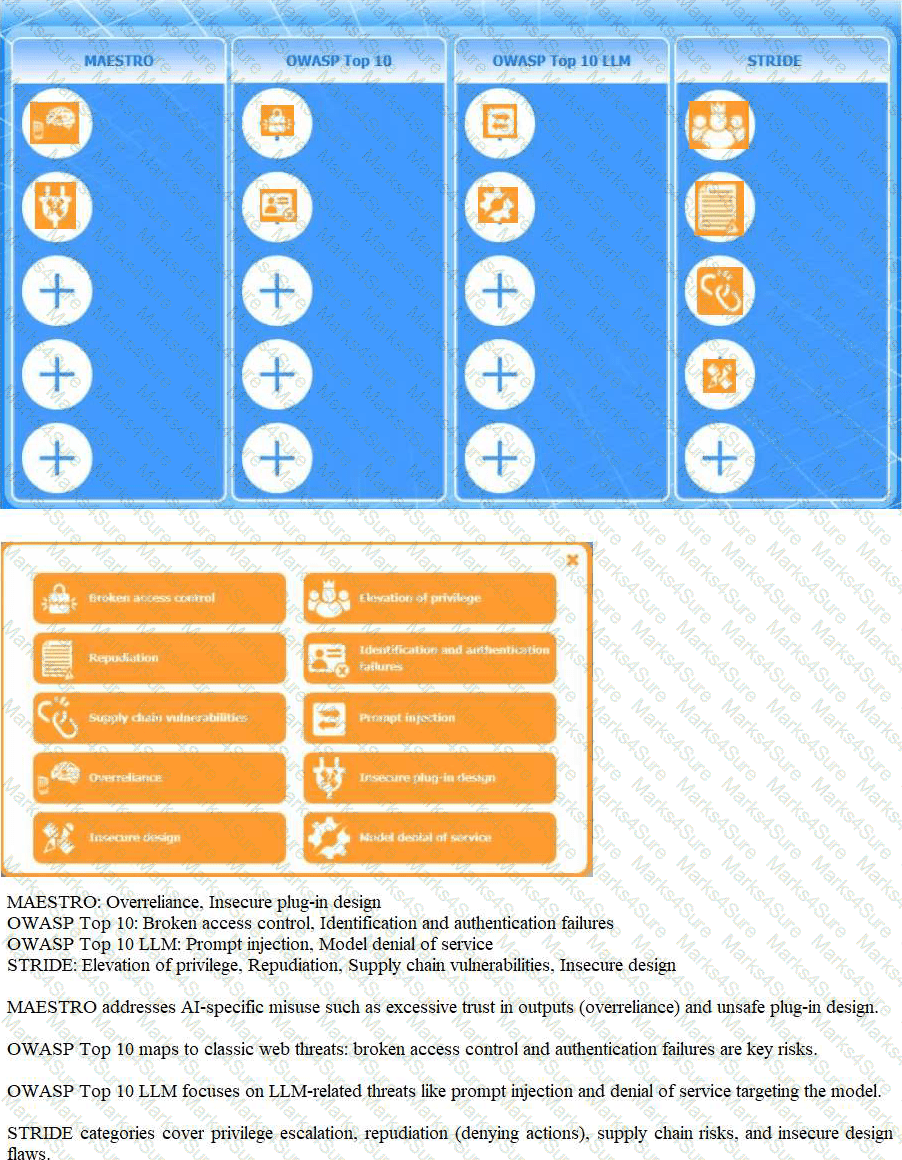
Instructions: Click the (+) to assign each threat category into its appropriate framework.
An architect is modeling an agentic system to meet security standards.
A security analyst receives an alert about an AI system and is investigating the following output:

Which of the following is the most appropriate control the analyst should recommend?
A detection engineering team wants to use AI to automatically prevent vulnerable code from reaching production.
Which of the following is the most effective way to accomplish this task?
A security administrator needs to improve an AI model. During an initial investigation, the administrator notices that two successive login failures are recorded every day, and then a successful login occurs after a specific time interval. All the successful login attempts have been during office hours.
Which of the following techniques should the administrator use to improve the AI model ' s security?
A SOC analyst identifies that a user extracted the full system prompt from the company ' s chatbot by prompting it to repeat the last query and provide the entire conversation context. Which of the following mitigations reduces the risk to the AI system?
A user interface engineer adds new graphics to the latest release of an AI-integrated application. During the update, the engineer accidentally causes the model to retrain on unverified data. After the update, the model begins to return many errors.
Which of the following is the best way to mitigate future errors?
A cybersecurity administrator must examine the cost of AI and implement controls so the research environment operates within a specified budget.
Which of the following controls is best for this situation?
A SOC team has an AI agent that performs web searches and calls to the SOAR solution. The team is concerned about enterprise uptime and case resolution time.
Which of the following is the most appropriate use of the AI agent?
A security administrator sees suspicious queries on AI logs.
Which of the following should the administrator implement to address this issue?
A company develops an AI model to diagnose patients. Hospitals access the model through an integrated application programming interface (API). The security team performs a denial-of-service (DoS) attack via brute force on the model.
Which of the following controls would have prevented this issue?
A company deploys an internet-facing chatbot using RAG. Logs show that an administrator can retrieve employee names and usernames while an employee receives ' information not available. ' Which of the following is reducing the risk of sensitive data exposure in this scenario?
A security consultant must summarize the impact of posture management on a machine learning (ML) use case.
Which of the following is the most appropriate reference for this purpose?
A security administrator wants to prevent prompt injection attacks and ensure responses have sanitized output.
Which of the following provides a primary compensating control for these requirements?
Which of the following International Organization for Standardization (ISO) standards should be selected for certification to use for third-party assurance for responsible AI practices?
Which of the following would most likely be used to prove that an image is AI generated?
A line of business wants to onboard an application that uses a custom AI model for employee assessments. The Chief Information Officer (CIO) agrees to allow the engagement to proceed but first wants a threat model.
Which of the following is the most appropriate to use for an AI threat model?
An organization develops a chatbot that does not provide harmful or explicit responses, must use clean and professional language, and ensures that responses are accurate.
Which of the following should the organization conduct after the chatbot is fully developed but before a customer-facing deployment?
Which of the following roles best supports the implementation of AI governance, risk, and compliance (GRC)? (Choose two.)
A cybersecurity administrator needs a security mechanism that can validate input.
Which of the following controls should the administrator use?
A manufacturing company wants to use AI within its operations to improve the efficiency and accuracy of its processes.
Which of the following should the organization do first to enable adoption and achieve the business objectives?
Which of the following responsible AI standards refers to a principle that clearly states the reasons behind the decisions for a particular conclusion?
A legal firm permits employees to use a company-authorized chatbot for their research and reporting. In the past year, the firm had to retract some of its released documents because of incorrect references.
Which of the following best describes the weakness that caused this issue?
An IT company implements an adaptable chatbot that learns from user prompts. Based on the conversation shown — where User 2 injected false information about a company acquisition that caused the chatbot to give incorrect responses to User 3 — which of the following compensating controls should an administrator implement to mitigate the issue?
An airline corporation wants to implement a chatbot application using a large language model (LLM) so its customers can ask questions and receive answers about flight details and have the option to upload files.
Which of the following security controls should the airline use to protect against malicious input and unauthorized use beyond the service-level agreement? (Choose two.)
During an update, an AI system flags some potential compatibility issues and provides recommendations. An administrator reviews the recommendations before addressing the issues.
Which of the following processes describes this scenario?
An automobile manufacturer implements a chatbot to assist with configuration options for customer automobiles. Given a customer ' s prompt, the chatbot gives offensive responses.
Which of the following describes this behavior?
Which of the following is required first in order to send a prompt query and response in a language model (LLM) system when authentication is enabled?
A cybersecurity analyst wants to choose a machine learning (ML) model to classify log entries while providing the best explainability.
Which of the following models should the analyst use?
A data scientist investigates reports that a production machine learning (ML) model no longer performs with accuracy.
The data scientist finds the following pipeline log entries:
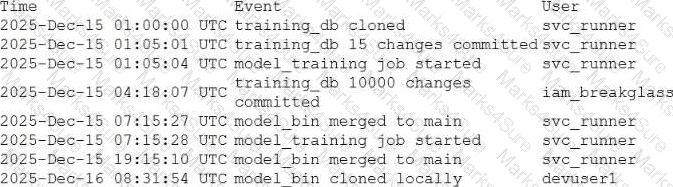
Which of the following should the security team do to mitigate future occurrences?
A security analyst finds that the AI system is under a denial-of-wallet attack.
Which of the following should the analyst enforce to protect the company? (Choose two.)
An organization implements a domain-specific AI chatbot. After operating normally for weeks, the model returns contextually incorrect responses — treating ' worm ' as a biological pest rather than a computer worm when answering a cybersecurity question.
Which of the following should the organization do to address the issue?
Which of the following is the best example of an AI model that is trained to identify multiple points from input using a neural network to provide output for authentication?
PDF + Testing Engine
Testing Engine
PDF (Q&A)