Free Practice Questions for the HP Aruba Certified Switching Expert HPE7-A10 Exam (2026 Updated)
At Marks4sure, we are dedicated to providing IT professionals with the most accurate and reliable preparation materials for the HP HPE7-A10 exam. To support your certification journey, we have made a selection of our premium 2026 Aruba Certified Switching Expert practice questions and answers available completely free. You can take this practice test as many times as you need. Every question includes a detailed, expertly verified explanation to ensure you fully grasp the core security concepts before test day.
A customer has an AOS-10 architecture managed by HPE Aruba Networking Central. HPE Aruba Networking infrastructure devices authenticate clients against an HPE Aruba Networking ClearPass cluster.
In HPE Aruba Networking Central, you are reviewing network traffic flows for a wireless IoT device categorized as "Raspberry Pi" clients. You observe SSH traffic. You then review several additional wireless IoT clients and find that they are also sending SSH.
Refer to the scenario.
You are assisting the customer in evaluating ways to mitigate the potential threat detected. The customer wants to temporarily block misbehaving clients for a penalty period. If a client reconnects and no longer sends SSH traffic, it should be permitted to stay connected.
What approach should you take?
You are helping a developer create a custom NAE script for an AOS-CX switch. What information might you need to provide so the developer can define the parameters correctly?
You must install a certificate on a standalone HPE Aruba Networking Mobility Controller (MC). The MC must use the certificate for the Web UI and to implement RadSec with HPE Aruba Networking ClearPass Policy Manager. You have received a certificate with these settings:
Subject: CN=mc49.site30.example.com
No SANs
Issuer: CN=ca89.example.com
EKUs: Server Authentication, Client Authentication
What problem does this certificate have for its intended uses?
The customer needs a secure wireless solution that lets users onboard new wireless clients. You are recommending a new WLAN that will give users limited access for this process.
Which WLAN security should you recommend, assuming users have a mixture of WPA2- and WPA3-capable devices?
A customer requires you to configure Aruba ClearPass Policy Manager (CPPM) to authenticate domain users on domain computers. Domain users, domain computers, and domain controllers obtain certificates from a Windows CA. CPPM must validate these certificates and confirm that the users and computers have accounts in Windows AD. The customer requires encrypted communication for all traffic between CPPM and the domain controllers.
You have imported the Windows CA root certificate into the ClearPass CA Trust list.
Based on these requirements, which usages should be added to it?
Refer to the exhibit.
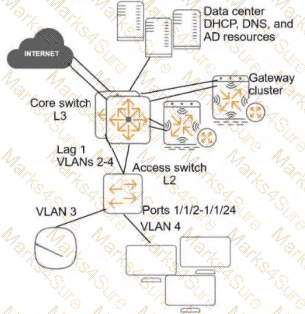
A customer needs protection from ARP poisoning in VLAN 4. The following lists all settings for VLAN 4 and the physical interfaces associated with VLAN 4 on the AOS-CX access-layer switch:
interface 1/1/2-1/1/24
no shutdown
no routing
vlan access 4
exit
interface lag 1
no shutdown
no routing
vlan trunk native 1
vlan trunk allowed 2-4
arp inspection trust
exit
vlan 4
arp inspection
exit
What is one problem with this configuration?
A customer has an AOS-10 architecture managed by HPE Aruba Networking Central. HPE Aruba Networking infrastructure devices authenticate clients against an HPE Aruba Networking ClearPass cluster.
In HPE Aruba Networking Central, you are reviewing network traffic flows for a wireless IoT device categorized as "Raspberry Pi" clients. You observe SSH traffic. You then review several additional wireless IoT clients and find that they are also sending SSH.
Refer to the scenario.
You are helping the customer evaluate ways to mitigate the potential threat that was detected. The customer suggests simply adding a rule that denies SSH traffic to the IoT client’s AOS user role.
What is the security drawback of this approach?
You are helping a company add HPE Aruba Networking ClearPass to its network, which uses HPE Aruba Networking infrastructure devices.
The company already has a Windows domain and Windows CA. The Windows CA issues certificates to domain computers, domain users, and servers such as domain controllers.
ClearPass cluster IP addressing and hostnames
Publisher = 10.47.47.5
Subscriber 1 = 10.47.47.6
Subscriber 2 = 10.47.47.7
Virtual IP with Subscriber 1 and Subscriber 2 = 10.47.47.8
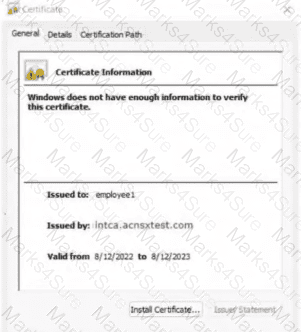
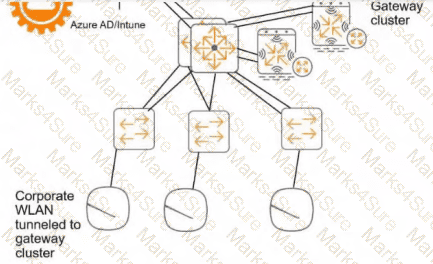
Refer to the scenario.
You have begun creating a CA to meet the customer's requirements for issuing certificates to mobile clients, as shown in the exhibit below.
Certificate Authority Settings:
Name: Exam Onboard CA
Mode: Root CA
Authority Info Access: Do not include OCSP Responder URL
Validity Period: 365 days
Clock Skew Allowance: 15
Subject Alternative Name: [X] Include device information in TLS client certificates
Digest Algorithm: SHA-512
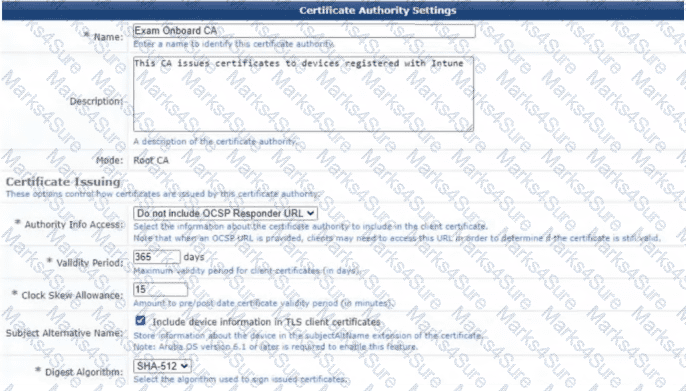
What change will help meet those requirements and the requirements for authenticating clients?
An HPE Aruba Networking Mobility Controller is configured with the following commands:
`aaa rfc-3576-server 10.1.2.3 key mysecretkey & ^%!7531 replay-protection window-duration 300`
Later, this output is displayed:
`(host)#show aaa rfc-3576-server statistics`
`RADIUS RFC 3576 Statistics - 10.1.2.3`
`Disconnect Requests: 2534 | Disconnect Accepts: 2534 | Disconnect Rejects: 0`
`No Secret: 0 | No Session ID: 0 | Bad Authenticator: 0 | Invalid Request: 0`
`Packets Dropped: 1431 | Unknown service: 0`
`CoA Requests: 2453 | CoA Accepts: 1022 | CoA Rejects: 0 | No permission: 0`
What should be investigated?
A company uses an HPE Aruba Networking EdgeConnect SD-Branch solution. The customer wants to integrate the solution with HPE Aruba Networking SSE.
What is one step that must be completed in HPE Aruba Networking SSE and is not automated as part of the typical setup?
A customer has an AOS-10 architecture that includes HPE Aruba Networking APs. The customer recently enabled WIDS at the high level on the APs. Administrators see several "ad hoc using valid SSID" events.
What should you explain?
Introduction to the customer
You are assisting a company with adding HPE Aruba Networking ClearPass to its network, which uses HPE Aruba Networking infrastructure devices.
The company already has a Windows domain and Windows CA. The Windows CA issues certificates to domain computers, domain users, and servers such as domain controllers.
ClearPass cluster IP addressing and hostnames
A customer's ClearPass cluster uses these IP addresses:
Publisher = 10.47.47.5
Subscriber 1 = 10.47.47.6
Subscriber 2 = 10.47.47.7
Virtual IP with Subscriber 1 and Subscriber 2 = 10.47.47.8
The customer's DNS server contains these entries:
cp.acnsxtest.com = 10.47.47.5
cps1.acnsxtest.com = 10.47.47.6
cps2.acnsxtest.com = 10.47.47.7
radius.acnsxtest.com = 10.47.47.8
onboard.acnsxtest.com = 10.47.47.8
Refer to the scenario.
The Onboard CA uses the settings shown in the exhibits below.
* CA Name: Onboard CA, CA ID: 2
* Common Name: ClearPass Intune Certificate Authority
Microsoft Entra ID (Azure AD) administrators need assistance configuring the app registration for integration with ClearPass Onboard.
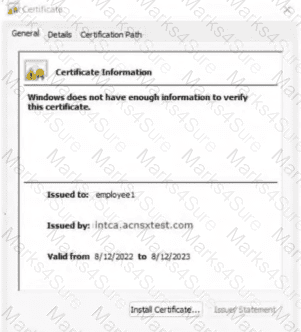
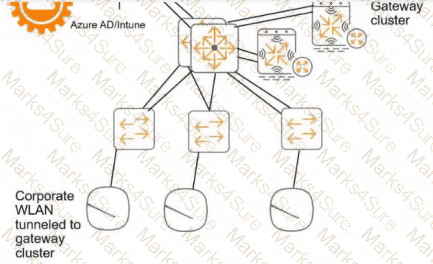
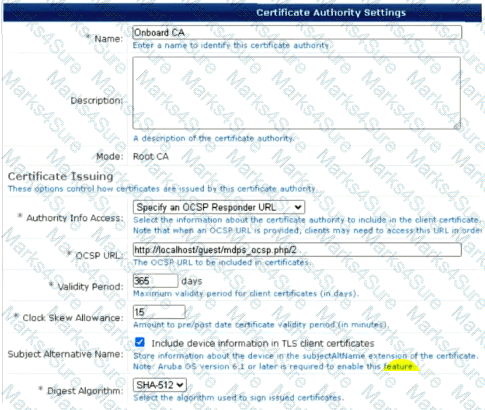
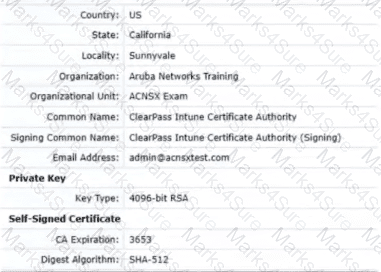
Which URL should you tell them to use?
A customer has an AOS-10 architecture managed by HPE Aruba Networking Central. HPE Aruba Networking infrastructure devices authenticate clients against an HPE Aruba Networking ClearPass cluster.
In HPE Aruba Networking Central, you are reviewing network traffic flows for a wireless IoT device categorized as a “Raspberry Pi” client. You observe SSH traffic. You then review several additional wireless IoT clients and find that they are also sending SSH.
Refer to the scenario.
You are assisting the customer in assessing ways to mitigate the potential threat detected. For the foreseeable future, until the security team has addressed the threat, the company wants to block most traffic from any IoT client detected sending SSH traffic. The company does want to allow limited access for these clients so that administrators can remediate them remotely.
What action should you take?
A customer operates two AOS-10 HPE Aruba Networking gateways at a site. The gateways are part of an SD-Branch solution managed by HPE Aruba Networking Central, and their cluster setting uses WLAN mode (the non-default gateway mode).
You are configuring a manual HPE Aruba Networking gateway cluster for dynamic authorization. The gateways have these IP addresses on a subnet that CPPM can access:
Gateway 1 = 10.56.20.2
Gateway 2 = 10.56.20.3
Which VRRP IP address assignments are valid for the gateways? Assume that all IP address options are available.
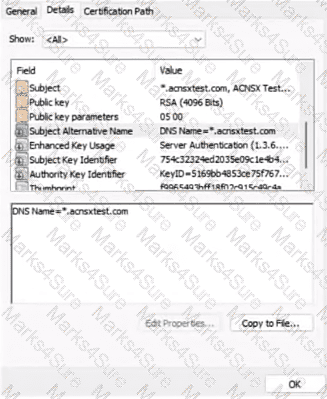
Refer to the exhibit.
Field: Subject
Value: .acnsxtest.com, ACNSX Test...
Field: Subject Alternative Name
Value: DNS Name=.acnsxtest.com
Field: Enhanced Key Usage
Value: Server Authentication (1.3.6.1.5.5.7.3.1)
You have received this certificate to install on an HPE Aruba Networking ClearPass server for RADIUS/EAP and RadSec use. What is one issue?
You are assisting a company with designing role-based access control policies on HPE Aruba Networking AOS-10 gateways. The security policy dictates that traffic originating from authenticated corporate user roles must be inspected statefully, allowing client-initiated outbound flows to the data center while strictly dropping any unsolicited inbound connection attempts initiated from data center servers back toward the clients.
What design principle ensures this traffic flow behavior?
Refer to the exhibit.
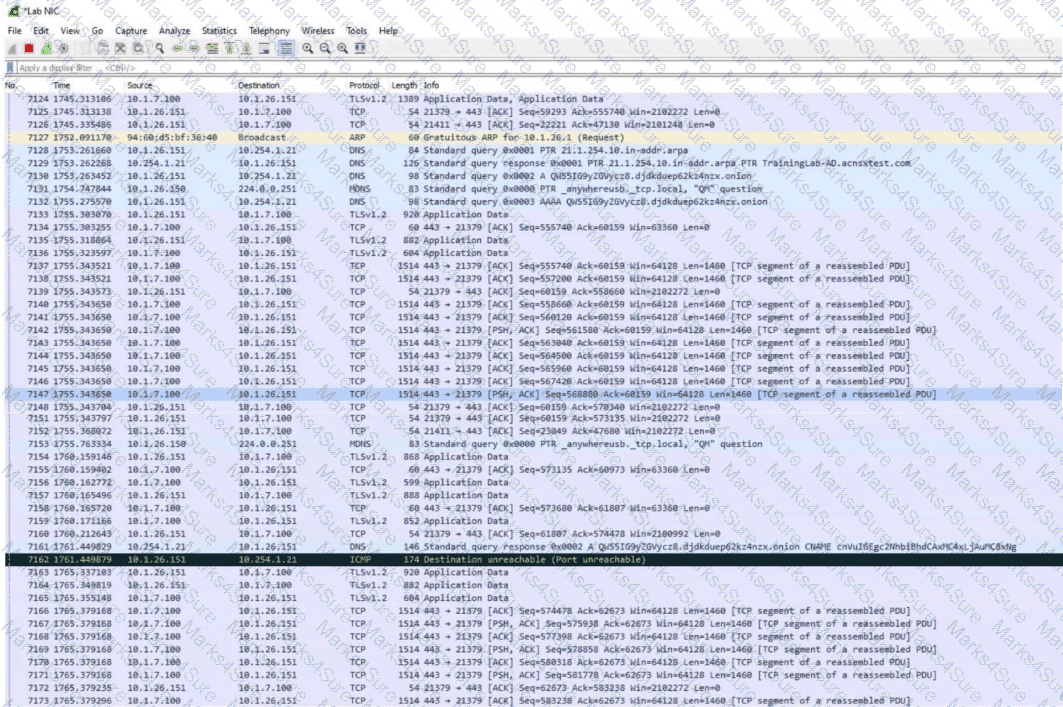
Frame 7128: 10.1.26.151 - > 10.254.1.21 DNS Standard query 0x0001 PTR 21.1.254.10.in-addr.arpa
Frame 7130: 10.1.26.151 - > 10.254.1.21 DNS Standard query 0x0002 A Qw5SIG9yZGvycz8.djdkduep62kz4nzx.onion
Frame 7147: 10.1.26.151 - > 10.1.7.100 TCP 443 - > 21379 [PSH, ACK]
Frame 7162: 10.1.26.151 - > 10.254.1.21 ICMP Destination unreachable (Port unreachable)
Which IP address should be recorded as a potentially compromised client?
A company has HPE Aruba Networking gateways and plans to begin implementing gateway IDS/IPS. The customer has chosen Block as the Fail Strategy.
What could you recommend to help reduce unexpected outages caused by this particular fail strategy?
Your company uses HPE Aruba Networking AOS-10 APs and gateways, along with AOS-CX switches, all managed through HPE Aruba Networking Central. In HPE Aruba Networking Central, you need to collect a packet capture for a client connected to an AP.
What is a prerequisite?
PDF + Testing Engine
Testing Engine
PDF (Q&A)